Halloween Sale Special Limited Time 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: CFsave75

Pass the Cisco CCNP Security 300-710 Questions and answers with CertsForce

Viewing page 2 out of 14 pages
Viewing questions 11-20 out of questions
Questions # 11:

An engineer must build redundancy into the network and traffic must continuously flow if a redundant switch in front of the firewall goes down. What must be configured to accomplish this task?

Options:

A.

redundant interfaces on the firewall cluster mode and switches


B.

redundant interfaces on the firewall noncluster mode and switches


C.

vPC on the switches to the interface mode on the firewall duster


D.

vPC on the switches to the span EtherChannel on the firewall cluster


Expert Solution
Questions # 12:

An engineer must configure an ERSPAN passive interface on a Cisco Secure IPS by using the Cisco Secure Firewall Management Center. These configurations have been performed already:

Configure the passive interface.

Configure the ERSPAN IP address.

Which two additional settings must be configured to complete the configuration? (Choose two.)
Options:

A.

Source IP


B.

Bypass Mode


C.

TCP Intercept


D.

Flow ID


E.

Destination MAC


Expert Solution
Questions # 13:

Question # 13

Question # 13

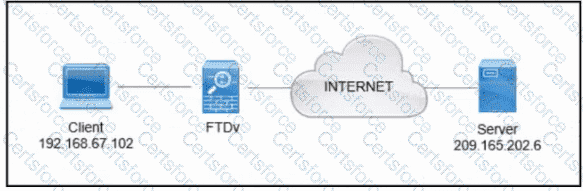
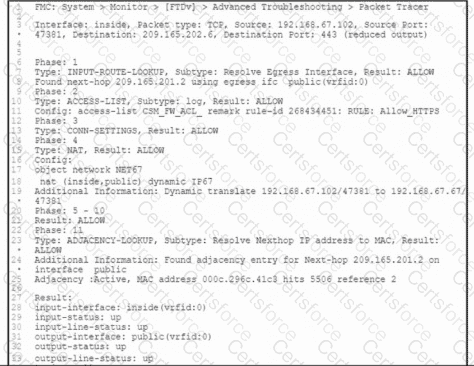
Refer to the exhibit. A client that has IP address 192.168.67.102 reports issues when connecting to a remote server. Based on the topology and output of packet tracer tool, which action resolves the connectivity issue?

Options:

A.

Add the route to the destination.


B.

Unblock the access rule on FTDv.


C.

Restart the client-side application.


D.

Reconfigure NAT on FTDv.


Expert Solution
Questions # 14:

An engineer must deploy a Cisco FTD device. Management wants to examine traffic without requiring network changes that will disrupt end users. Corporate security policy requires the separation of management traffic from data traffic and the use of SSH over Telnet for remote administration. How must the device be deployed to meet these requirements?

Options:

A.

in routed mode with a diagnostic interface


B.

in transparent mode with a management Interface


C.

in transparent made with a data interface


D.

in routed mode with a bridge virtual interface


Expert Solution
Questions # 15:

An engineer is troubleshooting the upgrade of a Cisco Secure Firewall Threat Defense device on the Secure Firewall Management Center 7.0 GUI. The engineer wants to collect the upgrade data and logs. Which two actions must the engineer take? (Choose two.)

Options:

A.

View the system and troubleshooting details.


B.

Select the Secure Firewall Threat Defense device properties.


C.

Select the Secure Firewall Management Center device.


D.

Access the Health Events page.


E.

Access the Health Monitor page.


Expert Solution
Questions # 16:

A Cisco FTD device is running in transparent firewall mode with a VTEP bridge group member ingress interface. What must be considered by an engineer tasked with specifying a destination MAC address for a packet trace?

Options:

A.

Only the UDP packet type is supported.


B.

The output format option for the packet logs is unavailable.


C.

The destination MAC address is optional if a VLAN ID value is entered.


D.

The VLAN ID and destination MAC address are optional.


Expert Solution
Questions # 17:

Network users experience issues when accessing a server on a different network segment. An engineer investigates the issue by performing packet capture on Cisco Secure Firewall Threat Defense. The engineer expects more data and suspects that not all the traffic was collected during a 15-minute can’t captured session. Which action must the engineer take to resolve the issue?

Options:

A.

Forward the captured data lo an FTP server


B.

Increase the amount of RAM allocated for the capture.


C.

Provide a file name to save the data.


D.

Ensure that the allocated memory is sufficient.


Expert Solution
Questions # 18:

An administrator configures the interfaces of a Cisco Secure Firewall Threat Defence device in an inline IPS deployment. The administrator completes these actions:

* identifies the device and the interfaces

* sets the interface mode to inline

* enables the interlaces

Which configuration step must the administrator take next to complete the implementation?

Options:

A.

Enable spanning-tree PortFast on the interfaces.


B.

Configure an inline set


C.

Set the interface to Transparent mode.


D.

Set the interface to routed mode.


Expert Solution
Questions # 19:

A hospital network needs to upgrade their Cisco FMC managed devices and needs to ensure that a disaster recovery process is in place. What must be done in order to minimize downtime on the network?

Options:

A.

Configure a second circuit to an ISP for added redundancy


B.

Keep a copy of the current configuration to use as backup


C.

Configure the Cisco FMCs for failover


D.

Configure the Cisco FMC managed devices for clustering.


Expert Solution
Questions # 20:

An engineer is troubleshooting a file that is being blocked by a Cisco FTD device on the network.

The user is reporting that the file is not malicious.

Which action does the engineer take to identify the file and validate whether or not it is malicious?

Options:

A.

identify the file in the intrusion events and submit it to Threat Grid for analysis.


B.

Use FMC file analysis to look for the file and select Analyze to determine its disposition.


C.

Use the context explorer to find the file and download it to the local machine for investigation.


D.

Right click the connection event and send the file to AMP for Endpoints to see if the hash is malicious.


Expert Solution
Viewing page 2 out of 14 pages
Viewing questions 11-20 out of questions