
Halloween Sale Special Limited Time 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: CFsave75

Pass the Cisco CCNP Security 300-710 Questions and answers with CertsForce

Viewing page 3 out of 14 pages
Viewing questions 21-30 out of questions
Questions # 21:

An engineer configures an access control rule that deploys file policy configurations to security zones or tunnel zones, and it causes the device to restart. What is the reason for the restart?

Options:

A.

Source or destination security zones in the access control rule matches the security zones that are associated with interfaces on the target devices.


B.

The source tunnel zone in the rule does not match a tunnel zone that is assigned to a tunnel rule in the destination policy.


C.

Source or destination security zones in the source tunnel zone do not match the security zones that are associated with interfaces on the target devices.


D.

The source tunnel zone in the rule does not match a tunnel zone that is assigned to a tunnel rule in the source policy.


Expert Solution
Questions # 22:

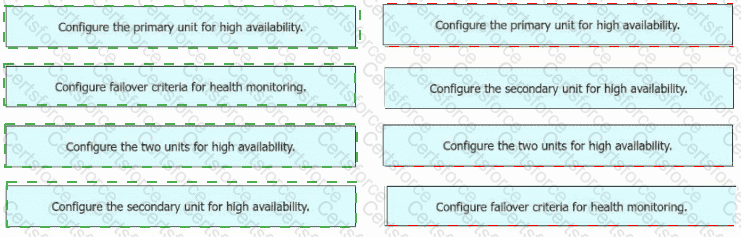
An engineer must configure high availability on two Cisco Secure Firewall Threat Defense appliances. Drag and drop the configuration steps from the left into the sequence on the right.
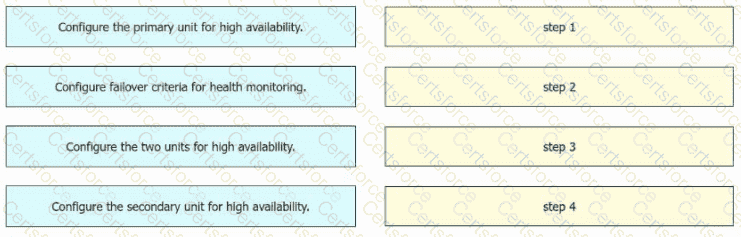
Question # 22


Expert Solution
Questions # 23:

An administrator is adding a QoS policy to a Cisco FTD deployment. When a new rule is added to the policy and QoS is applied on ' Interfaces in Destination Interface Objects " , no interface objects are available What is the problem?

Options:

A.

The FTD is out of available resources lor use. so QoS cannot be added


B.

The network segments that the interfaces are on do not have contiguous IP space


C.

QoS is available only on routed interfaces, and this device is in transparent mode.


D.

A conflict exists between the destination interface types that is preventing QoS from being added


Expert Solution
Questions # 24:

An organization recently implemented a transparent Cisco FTD in their network.

They must ensure that the device does not respond to insecure SSL/TLS protocols.

Which action accomplishes the task?

Options:

A.

Modify the device ' s settings using the device management feature within Cisco FMC to force onlysecure protocols.


B.

Use the Cisco FTD platform policy to change the minimum SSL version on the device to TLS 1.2.


C.

Enable the UCAPL/CC compliance on the device to support only the most secure protocols available.


D.

Configure a FlexConfig object to disable any insecure TLS protocols on the Cisco FTD device.


Expert Solution
Questions # 25:

Which two statements about deleting and re-adding a device to Cisco FMC are true? (Choose two.)

Options:

A.

An option to re-apply NAT and VPN policies during registration is available, so users do not need to re- apply the policies after registration is completed.


B.

Before re-adding the device in Cisco FMC, you must add the manager back in the device.


C.

No option to delete and re-add a device is available in the Cisco FMC web interface.


D.

The Cisco FMC web interface prompts users to re-apply access control policies.


E.

No option to re-apply NAT and VPN policies during registration is available, so users need to re-apply the policies after registration is completed.


Expert Solution
Questions # 26:

A network administrator reviews the file report for the last month and notices that all file types, except exe. show a disposition of unknown. What is the cause of this issue?

Options:

A.

The malware license has not been applied to the Cisco FTD.


B.

The Cisco FMC cannot reach the Internet to analyze files.


C.

A file policy has not been applied to the access policy.


D.

Only Spero file analysis is enabled.


Expert Solution
Questions # 27:

An engineer must configure the firewall to monitor traffic within a single subnet without increasing the hop count of that traffic. How would the engineer achieve this?

Options:

A.

Configure Cisco Firepower as a transparent firewall


B.

Set up Cisco Firepower as managed by Cisco FDM


C.

Configure Cisco Firepower in FXOS monitor only mode.


D.

Set up Cisco Firepower in intrusion prevention mode


Expert Solution
Questions # 28:

Which two deployment types support high availability? (Choose two.)

Options:

A.

transparent


B.

routed


C.

clustered


D.

intra-chassis multi-instance


E.

virtual appliance in public cloud


Expert Solution
Questions # 29:

A network administrator must send a daily email report to management detailing changes made during the previous 24 hours in Cisco Secure Firewall Management Center. Which system setting must be enabled to meet this requirement?

Options:

A.

Change Reconciliation


B.

Send Audit Log to HTTP Server


C.

Send Audit Log to Syslog


D.

STIG Compliance


Expert Solution
Questions # 30:

administrator is configuring SNORT inspection policies and is seeing failed deployment messages in Cisco FMC . What information should the administrator generate for Cisco TAC to help troubleshoot?

Options:

A.

A Troubleshoot " file for the device in question.


B.

A " show tech " file for the device in question


C.

A " show tech " for the Cisco FMC.


D.

A " troubleshoot " file for the Cisco FMC


Expert Solution
Viewing page 3 out of 14 pages
Viewing questions 21-30 out of questions