Halloween Sale Special Limited Time 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: CFsave75

Pass the Cisco CCNP Security 300-710 Questions and answers with CertsForce

Viewing page 1 out of 14 pages
Viewing questions 1-10 out of questions
Questions # 1:

An engineer must configure an inline set on a Cisco Secure IPS by using the Cisco Secure Firewall Management Center. The inline set must make a copy of each packet before analyzing the packet and block any connections that do not complete the three-way handshake. These configurations have been performed already:

Select and enable the interfaces that will be added to the inline set.

Configure the speed and duplex.

Configure the inline set and add the interfaces to the inline set.

Which action completes the task?

Options:

A.

Set Tap Mode to Inline.


B.

Configure Snort Fail Open.


C.

Configure Link State Propagation.


D.

Implement Strict TCP Enforcement.


Expert Solution
Questions # 2:

Which protocol establishes network redundancy in a switched Firepower device deployment?

Options:

A.

STP


B.

HSRP


C.

GLBP


D.

VRRP


Expert Solution
Questions # 3:

An engineer currently has a Cisco FTD device registered to the Cisco FMC and is assigned the address of 10 10.50.12. The organization is upgrading the addressing schemes and there is a requirement to convert the addresses to a format that provides an adequate amount of addresses on the network What should the engineer do to ensure that the new addressing takes effect and can be used for the Cisco FTD to Cisco FMC connection?
Options:

A.

Delete and reregister the device to Cisco FMC


B.

Update the IP addresses from IFV4 to IPv6 without deleting the device from Cisco FMC


C.

Format and reregister the device to Cisco FMC.


D.

Cisco FMC does not support devices that use IPv4 IP addresses.


Expert Solution
Questions # 4:

Question # 4

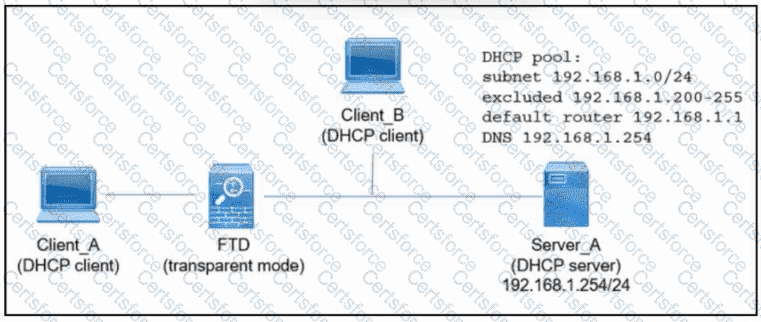
Refer to the exhibit. An engineer is deploying a new instance of Cisco Secure Firewall Threat Defense. Which action must the engineer take next so that Client_A and Client_B receive an IP address via DHCP from Server_A?

Options:

A.

Disable Option 82 in the DHCP relay configuration properties using Secure Firewall Management Center.


B.

Add access rules that allow DHCP traffic by using Cisco Secure Firewall Management Center.


C.

Add another DHCP pool on Server_A with DHCP relay on Secure Firewall Threat Defense.


D.

Disable all the DHCP Snort rules by using Secure Firewall Device Manager.


Expert Solution
Questions # 5:

Which two statements about bridge-group interfaces in Cisco FTD are true? (Choose two.)

Options:

A.

The BVI IP address must be in a separate subnet from the connected network.


B.

Bridge groups are supported in both transparent and routed firewall modes.


C.

Bridge groups are supported only in transparent firewall mode.


D.

Bidirectional Forwarding Detection echo packets are allowed through the FTD when using bridge-group members.


E.

Each directly connected network must be on the same subnet.


Expert Solution
Questions # 6:

In which two ways do access control policies operate on a Cisco Firepower system? (Choose two.)

Options:

A.

Traffic inspection can be interrupted temporarily when configuration changes are deployed.


B.

The system performs intrusion inspection followed by file inspection.


C.

They can block traffic based on Security Intelligence data.


D.

File policies use an associated variable set to perform intrusion prevention.


E.

The system performs a preliminary inspection on trusted traffic to validate that it matches the trusted parameters.


Expert Solution
Questions # 7:

Upon detecting a flagrant threat on an endpoint, which two technologies instruct Cisco Identity Services Engine to contain the infected endpoint either manually or automatically? (Choose two.)

Options:

A.

Cisco ASA 5500 Series


B.

Cisco FMC


C.

Cisco AMP


D.

Cisco Stealthwatch


E.

Cisco ASR 7200 Series


Expert Solution
Questions # 8:

An engineer is reviewing a ticket that requests to allow traffic for some devices that must connect to a server over 8699/udp. The request mentions only one IP address, 172.16.18.15, but the requestor asked for the engineer to open the port for all machines that have been trying to connect to it over the last week. Which action must the engineer take to troubleshoot this issue?

Options:

A.

Use the context explorer to see the application blocks by protocol.


B.

Use the context explorer to see the destination port blocks


C.

Filter the connection events by the source port 8699/udp.


D.

Filter the connection events by the destination port 8699/udp.


Expert Solution
Questions # 9:

Which two routing options are valid with Cisco Firepower Threat Defense? (Choose two.)

Options:

A.

BGPv6


B.

ECMP with up to three equal cost paths across multiple interfaces


C.

ECMP with up to three equal cost paths across a single interface


D.

BGPv4 in transparent firewall mode


E.

BGPv4 with nonstop forwarding


Expert Solution
Questions # 10:

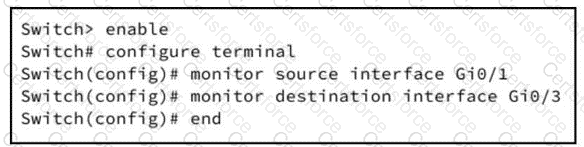
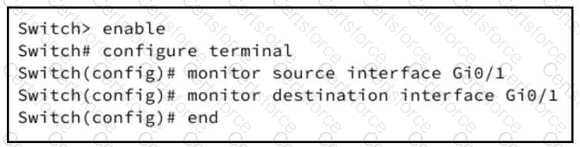
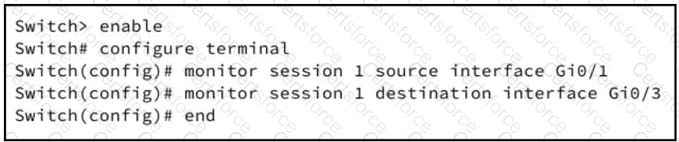
An engineer must configure a SPAN to monitor traffic by using a Cisco Secure IPS device in passive mode. The Cisco Secure IPS interface Gi0/1 is connected to Cisco Catalyst Switch interface Gi0/3. Which SPAN configuration meets the requirement?

A)
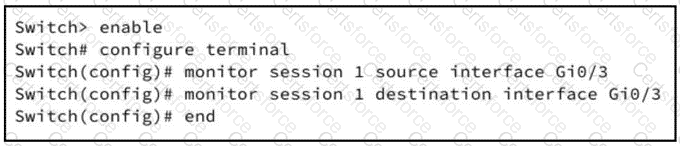
Question # 10

B)

Question # 10

C)

Question # 10

D)

Question # 10

Options:

A.

Option A


B.

Option B


C.

Option C


D.

Option D


Expert Solution
Viewing page 1 out of 14 pages
Viewing questions 1-10 out of questions