Halloween Sale Special Limited Time 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: CFsave75

Pass the Cisco CCNP Security 300-710 Questions and answers with CertsForce

Viewing page 6 out of 14 pages
Viewing questions 51-60 out of questions
Questions # 51:

A company is in the process of deploying intrusion prevention with Cisco FTDs managed by a Cisco FMC. An engineer must configure policies to detect potential intrusions but not block the suspicious traffic. Which action accomplishes this task?

Options:

A.

Configure IDS mode when creating or editing a policy rule under the Cisco FMC Intrusion tab in Access Policies section by unchecking the " Drop when inline " option.


B.

Configure IPS mode when creating or editing a policy rule under the Cisco FMC Intrusion tab in Access Policies section by checking the " Drop when inline " option.


C.

Configure IPS mode when creating or editing a policy rule under the Cisco FMC Intrusion tab in Access Policies section by unchecking the " Drop when inline " option.


D.

Configure IDS mode when creating or editing a policy rule under the Cisco FMC Intrusion tab in Access Policies section by checking the " Drop when inline " option.


Expert Solution
Questions # 52:

A network administrator is concerned about (he high number of malware files affecting users ' machines. What must be done within the access control policy in Cisco FMC to address this concern?

Options:

A.

Create an intrusion policy and set the access control policy to block.


B.

Create an intrusion policy and set the access control policy to allow.


C.

Create a file policy and set the access control policy to allow.


D.

Create a file policy and set the access control policy to block.


Expert Solution
Questions # 53:

Refer to the exhibit.

Question # 53

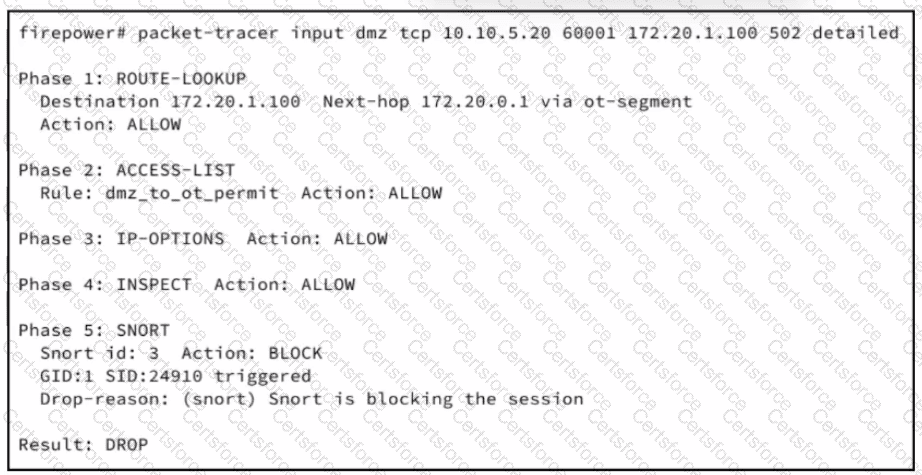
At a manufacturing facility, a historian server 10.10.5.20 in the OT DMZ is intermittently unable to reach a remote PLC at 172.20.1.100 on TCP 502 Modbus. A security engineer runs packet-tracer on Cisco Secure Firewall Threat Defence and captures the output. The access policy is verified as correct. Which action must be performed to resolve the issue?

Options:

A.

Increase the MTU on the of-segment interface to prevent Modbus payload fragmentation during deep packet inspection.


B.

Disable logging for the rule matching traffic from 10.10.5.20 to 172.20.1.100 on port TCP 502 Modbus.


C.

Associate the ACP rule " dmz_to_of_permit " with a separate intrusion policy that excludes Modbus protocol signatures.


D.

Create intrusion policy exception for SID 24910 scoped to the historian-to-PLC Modbus flow with rule action to Alert/Generate Events.


Expert Solution
Questions # 54:

A network administrator is troubleshooting access to a website hosted behind a Cisco FTD device External clients cannot access the web server via HTTPS The IP address configured on the web server is 192 168 7.46 The administrator is running the command capture CAP interface outside match ip any 192.168.7.46 255.255.255.255 but cannot see any traffic in the capture Why is this occurring?

Options:

A.

The capture must use the public IP address of the web server.


B.

The FTD has no route to the web server.


C.

Theaccess policy is blocking the traffic.


D.

The packet capture shows only blocked traffic


Expert Solution
Questions # 55:

A network engineer is configuring URL Filtering on Firepower Threat Defense. Which two port requirements on the Firepower Management Center must be validated to allow communication with the cloud service? (Choose two.)

Options:

A.

outbound port TCP/443


B.

inbound port TCP/80


C.

outbound port TCP/8080


D.

inbound port TCP/443


E.

outbound port TCP/80


Expert Solution
Questions # 56:

An engineer has been tasked with performing an audit of network projects to determine which objects are duplicated across the various firewall models (Cisco Secure Firewall Threat Defense Cisco Secure firewall ASA, and Meraki MX Series) deployed throughout the company Which tool will assist the engineer in performing that audit?

Options:

A.

Cisco Firepower Device Manager


B.

Cisco SecureX


C.

Cisco Defense Orchestrator


D.

Cisco Secure Firewall Management Center


Expert Solution
Questions # 57:

A network administrator notices that inspection has been interrupted on all non-managed interfaces of a device. What is the cause of this?

Options:

A.

The value of the highest MTU assigned to any non-management interface was changed.


B.

The value of the highest MSS assigned to any non-management interface was changed.


C.

A passive interface was associated with a security zone.


D.

Multiple inline interface pairs were added to the same inline interface.


Expert Solution
Questions # 58:

An engineer must replace a Cisco Secure Firewall high-availability device due to a failure. When the replacement device arrives, the engineer must separate the high-availability pair from Cisco Secure Firewall Management Center Which action must the engineer take first to restore high availability?

Options:

A.

Register the secondary device


B.

Force a break between the devices.


C.

Unregister the secondary device.


D.

Configure NTP time synchronization.


Expert Solution
Questions # 59:

What is the role of realms in the Cisco ISE and Cisco Secure Firewall Management Center integration?
Options:

A.

TACACS+ database


B.

AD definition


C.

Cisco Secure Firewall VDC


D.

Cisco ISE context


E.

(Option not provided – please confirm or provide)


Expert Solution
Questions # 60:

Question # 60

Question # 60

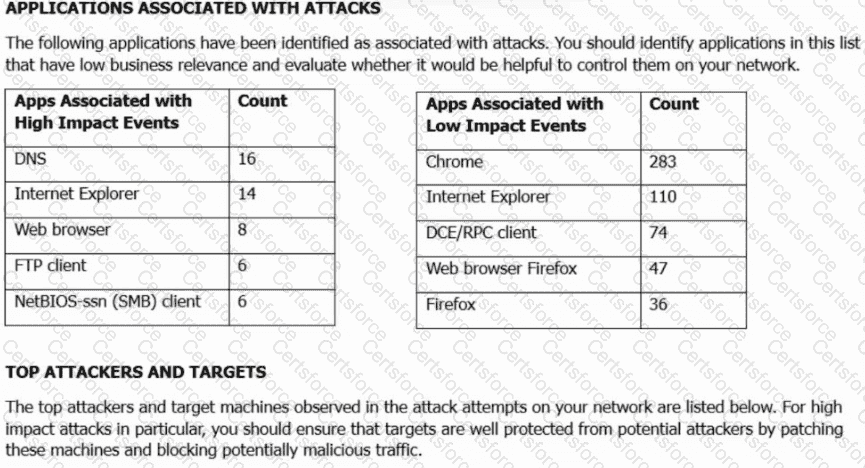
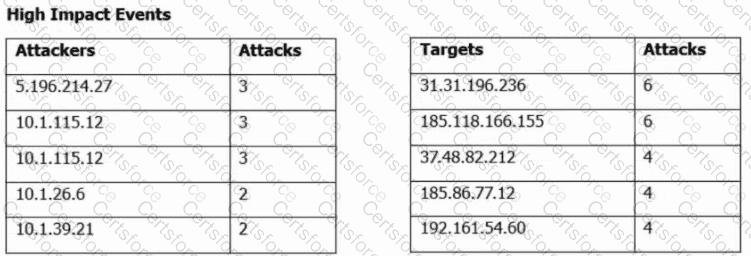
Refer to the exhibit. A security engineer must improve security in an organization and is producing a risk mitigation strategy to present to management for approval. Which action must the security engineer take based on this Attacks Risk Report?

Options:

A.

Block Internet Explorer.


B.

Block NetBIOS.


C.

Inspect TCP port 80 traffic.


D.

Inspect DNS traffic.


Expert Solution
Viewing page 6 out of 14 pages
Viewing questions 51-60 out of questions