Halloween Sale Special Limited Time 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: CFsave75

Pass the Cisco CCNP Security 300-710 Questions and answers with CertsForce

Viewing page 7 out of 14 pages
Viewing questions 61-70 out of questions
Questions # 61:

What are two application layer preprocessors? (Choose two.)

Options:

A.

CIFS


B.

IMAP


C.

SSL


D.

DNP3


E.

ICMP


Expert Solution
Questions # 62:

An engineer has been tasked with using Cisco FMC to determine if files being sent through the network are malware. Which two configuration takes must be performed to achieve this file lookup? (Choose two.)

Options:

A.

The Cisco FMC needs to include a SSL decryption policy.


B.

The Cisco FMC needs to connect to the Cisco AMP for Endpoints service.


C.

The Cisco FMC needs to connect to the Cisco ThreatGrid service directly for sandboxing.


D.

The Cisco FMC needs to connect with the FireAMP Cloud.


E.

The Cisco FMC needs to include a file inspection policy for malware lookup.


Expert Solution
Questions # 63:

A network engineer is logged into the Cisco AMP for Endpoints console and sees a malicious verdict for an identified SHA-256 hash. Which configuration is needed to mitigate this threat?

Options:

A.

Add the hash to the simple custom deletion list.


B.

Use regular expressions to block the malicious file.


C.

Enable a personal firewall in the infected endpoint.


D.

Add the hash from the infected endpoint to the network block list.


Expert Solution
Questions # 64:

Which firewall mode is Cisco Secure Firewall Threat Defense in when two physical interfaces are assigned to a named BVI?

Options:

A.

Routed


B.

Transparent


C.

In-line


D.

IPS only


Expert Solution
Questions # 65:

An organization is configuring a new Cisco Firepower High Availability deployment. Which actionmust be taken to ensure that failover is as seamless as possible to end users?

Options:

A.

Set up a virtual failover MAC address between chassis.


B.

Use a dedicated stateful link between chassis.


C.

Load the same software version on both chassis.


D.

Set the same FQDN for both chassis.


Expert Solution
Questions # 66:

Which Cisco Advanced Malware Protection for Endpoints policy is used only for monitoring endpoint actively?

Options:

A.

Windows domain controller


B.

audit


C.

triage


D.

protection


Expert Solution
Questions # 67:

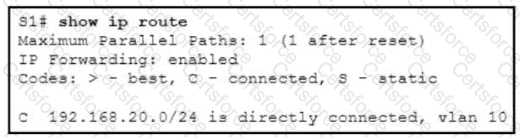
Refer to the exhibit.

Question # 67

An engineer must configure a static route on the Cisco Catalyst switch to reach 192.168.10.0/24 through the 192.168.20.1 next hop. The route must use an administrative distance of 2. Which command meets the requirements?

Options:

A.

ip route 192.168.10.0 255.255.255.0 192.168.20.1 1


B.

ip route 192.168.20.0 255.255.255.0 192.168.10.1 1


C.

ip route 192.168.10.0 255.255.255.0 192.168.20.1 2


D.

ip route 192.168.20.0 255.255.255.0 192.168.10.1 2


Expert Solution
Questions # 68:

An engineer is investigating connectivity problems on Cisco Firepower that is using service group tags. Specific devices are not being tagged correctly, which is preventing clients from using the proper policies when going through the firewall How is this issue resolved?

Options:

A.

Use traceroute with advanced options.


B.

Use Wireshark with an IP subnet filter.


C.

Use a packet capture with match criteria.


D.

Use a packet sniffer with correct filtering


Expert Solution
Questions # 69:

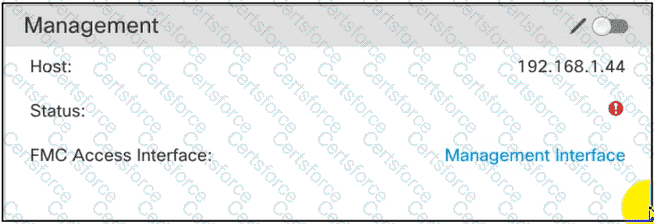
Refer to the exhibit.

Question # 69

What is the effect of the existing Cisco FMC configuration?

Options:

A.

The remote management port for communication between the Cisco FMC and the managed device changes to port 8443.


B.

The managed device is deleted from the Cisco FMC.


C.

The SSL-encrypted communication channel between the Cisco FMC and the managed device becomes plain-text communication channel.


D.

The management connection between the Cisco FMC and the Cisco FTD is disabled.


Expert Solution
Questions # 70:

An engineer must configure a correlation policy in Cisco Secure Firewall Management Center to detect when an IP address from an internal network communicates with a known malicious host. Connections made by the internal IP addresses must be tracked, and an external dynamic list must be used for the condition. Which type of event must the engineer configure on the correlation policy?

Options:

A.

Intrusion Impact Alert


B.

Connection tracker


C.

Network discovery


D.

Malware


Expert Solution
Viewing page 7 out of 14 pages
Viewing questions 61-70 out of questions