Pre-Winter Sale Special Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: force70

Pass the Cisco CCNP Security 350-701 Questions and answers with CertsForce

Viewing page 3 out of 16 pages
Viewing questions 31-45 out of questions
Questions # 31:

Which attack is preventable by Cisco ESA but not by the Cisco WSA?

Options:

A.

buffer overflow


B.

DoS


C.

SQL injection


D.

phishing


Expert Solution
Questions # 32:

What is a functional difference between Cisco Secure Endpoint and Cisco Umbrella Roaming Client?

Options:

A.

Secure Endpoint authenticates users and provides segmentation, and the Umbrella Roaming Client allows only for VPN connectivity.


B.

Secure Endpoint stops and tracks malicious activity on hosts, and the Umbrella Roaming Client tracks only URL-based threats.


C.

The Umbrella Roaming Client authenticates users and provides segmentation, and Secure Endpoint allows only for VPN connectivity.


D.

The Umbrella Roaming client stops and tracks malicious activity on hosts, and Secure Endpoint tracks only URL-based threats.


Expert Solution
Questions # 33:

Which two endpoint measures are used to minimize the chances of falling victim to phishing and social

engineering attacks? (Choose two)

Options:

A.

Patch for cross-site scripting.


B.

Perform backups to the private cloud.


C.

Protect against input validation and character escapes in the endpoint.


D.

Install a spam and virus email filter.


E.

Protect systems with an up-to-date antimalware program


Expert Solution
Questions # 34:

Which proxy mode must be used on Cisco WSA to redirect TCP traffic with WCCP?

Options:

A.

transparent


B.

redirection


C.

forward


D.

proxy gateway


Expert Solution
Questions # 35:

Which type of data does the Cisco Stealthwatch system collect and analyze from routers, switches, and firewalls?

Options:

A.

NTP


B.

syslog


C.

SNMP


D.

NetFlow


Expert Solution
Questions # 36:

An organization uses Cisco FMC to centrally manage multiple Cisco FTD devices. The default management

port conflicts with other communications on the network and must be changed. What must be done to ensure

that all devices can communicate together?

Options:

A.

Manually change the management port on Cisco FMC and all managed Cisco FTD devices


B.

Set the tunnel to go through the Cisco FTD


C.

Change the management port on Cisco FMC so that it pushes the change to all managed Cisco FTDdevices


D.

Set the tunnel port to 8305


Expert Solution
Questions # 37:

An organization has a Cisco ESA set up with policies and would like to customize the action assigned for

violations. The organization wants a copy of the message to be delivered with a message added to flag it as a

DLP violation. Which actions must be performed in order to provide this capability?

Options:

A.

deliver and send copies to other recipients


B.

quarantine and send a DLP violation notification


C.

quarantine and alter the subject header with a DLP violation


D.

deliver and add disclaimer text


Expert Solution
Questions # 38:

A large enterprise is currently managing a hybrid environment consisting of a private data center and multiple public cloud providers. The security engineering team is concerned about “Shadow IT” and the lack of visibility into unauthorized cloud services being used by various departments. The architect must select a solution that provides comprehensive discovery of cloud application usage and assesses the risk of each service based on industry certifications. Which technical solution must be used to provide cross-environment visibility?

Options:

A.

EDR


B.

CASB


C.

Secure Firewall


D.

CWPP


Expert Solution
Questions # 39:

Which VPN provides scalability for organizations with many remote sites?

Options:

A.

DMVPN


B.

site-to-site iPsec


C.

SSL VPN


D.

GRE over IPsec


Expert Solution
Questions # 40:

Which security product enables administrators to deploy Kubernetes clusters in air-gapped sites without needing Internet access?

Options:

A.

Cisco Content Platform


B.

Cisco Container Controller


C.

Cisco Container Platform


D.

Cisco Cloud Platform


Expert Solution
Questions # 41:

Which ESA implementation method segregates inbound and outbound email?

Options:

A.

one listener on a single physical Interface


B.

pair of logical listeners on a single physical interface with two unique logical IPv4 addresses and one IPv6 address


C.

pair of logical IPv4 listeners and a pair Of IPv6 listeners on two physically separate interfaces


D.

one listener on one logical IPv4 address on a single logical interface


Expert Solution
Questions # 42:

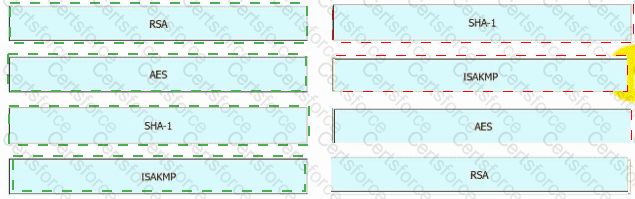
Drag and drop the VPN functions from the left onto the descriptions on the right.
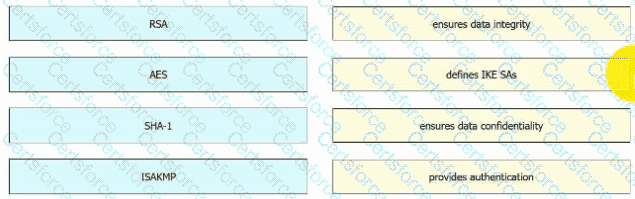
Question # 42


Expert Solution
Questions # 43:

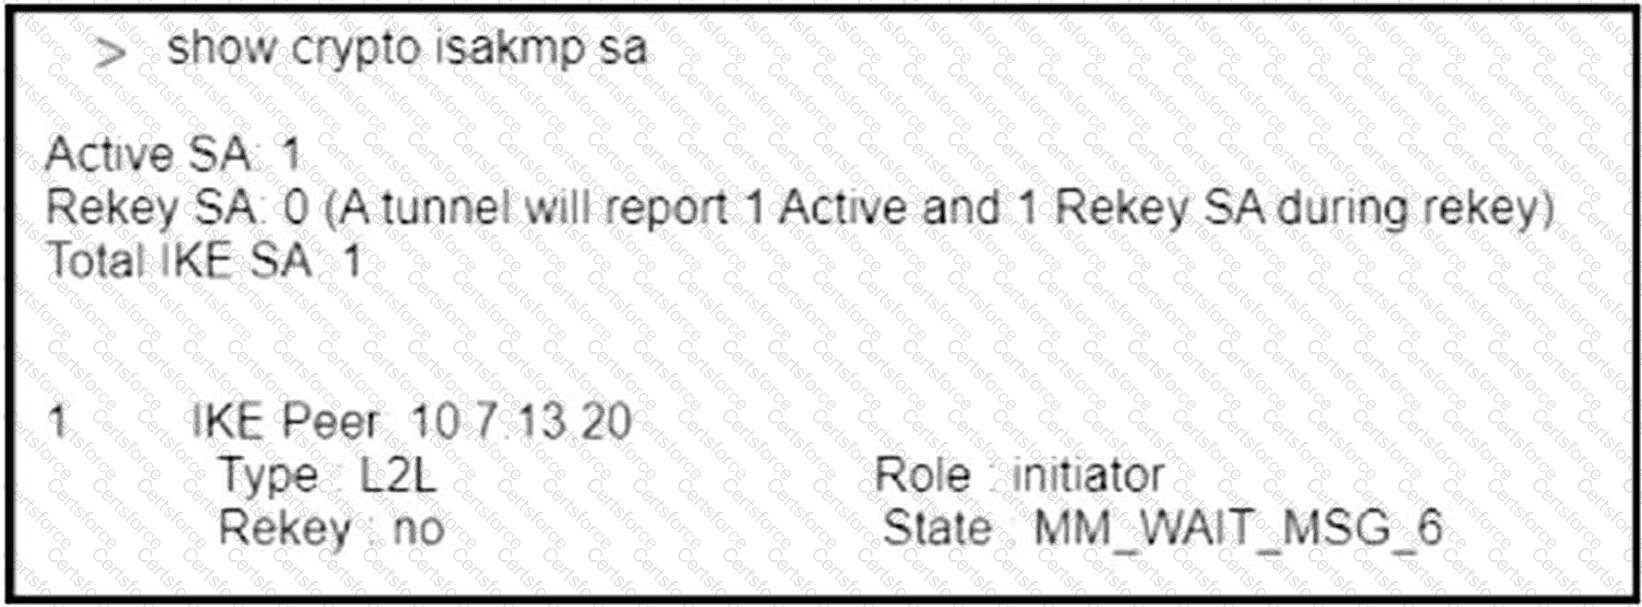
Refer to the exhibit.

Question # 43

During the rollout of a new site-to-site VPN between a headquarters Cisco Secure Firewall Threat Defense device and a partner firewall, the tunnel never completes IKEv1 Phase 1 and remains in the MM_WAIT_MSG_6 state. Reachability between the firewalls over the Internet is verified, ISAKMP UDP port 500 is permitted end-to-end, and the IKE Phase 1 policy parameters—including encryption, hashing, DH group, and lifetime—match exactly on both ends. Which configuration action must be performed to resolve the issue?

Options:

A.

Configure matching peer-identity values under each tunnel group on both endpoints.


B.

Add the same pre-shared key on both peers within their tunnel-group attributes.


C.

Implement identical Diffie-Hellman group numbers within the active IKEv1 policy.


D.

Apply equivalent transform sets and lifetimes inside the crypto-map entries.


Expert Solution
Questions # 44:

Which Cisco solution integrates industry-leading artificial intelligence and machine learning analytics and an assurance database to review the security posture and maintain visibility of an organization’s cloud environment?

Options:

A.

Cisco CSR1000v


B.

Cisco Secure Workload


C.

Cisco DNA


D.

Cisco FTD


Expert Solution
Questions # 45:

A network engineer has configured a NTP server on a Cisco ASA. The Cisco ASA has IP reachability to the

NTP server and is not filtering any traffic. The show ntp association detail command indicates that the

configured NTP server is unsynchronized and has a stratum of 16. What is the cause of this issue?

Options:

A.

Resynchronization of NTP is not forced


B.

NTP is not configured to use a working server.


C.

An access list entry for UDP port 123 on the inside interface is missing.


D.

An access list entry for UDP port 123 on the outside interface is missing.


Expert Solution
Viewing page 3 out of 16 pages
Viewing questions 31-45 out of questions