Pre-Winter Sale Special Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: force70

Pass the Cisco CCNP Security 350-701 Questions and answers with CertsForce

Viewing page 8 out of 16 pages
Viewing questions 106-120 out of questions
Questions # 106:

Which information is required when adding a device to Firepower Management Center?

Options:

A.

username and password


B.

encryption method


C.

device serial number


D.

registration key


Expert Solution
Questions # 107:

Which Cisco security solution stops exfiltration using HTTPS?

Options:

A.

Cisco FTD


B.

Cisco AnyConnect


C.

Cisco CTA


D.

Cisco ASA


Expert Solution
Questions # 108:

An organization wants to secure data in a cloud environment. Its security model requires that all users be

authenticated and authorized. Security configuration and posture must be continuously validated before access is granted or maintained to applications and data. There is also a need to allow certain application traffic and deny all other traffic by default. Which technology must be used to implement these requirements?

Options:

A.

Virtual routing and forwarding


B.

Microsegmentation


C.

Access control policy


D.

Virtual LAN


Expert Solution
Questions # 109:

What is the difference between a vulnerability and an exploit?

Options:

A.

A vulnerability is a hypothetical event for an attacker to exploit


B.

A vulnerability is a weakness that can be exploited by an attacker


C.

An exploit is a weakness that can cause a vulnerability in the network


D.

An exploit is a hypothetical event that causes a vulnerability in the network


Expert Solution
Questions # 110:

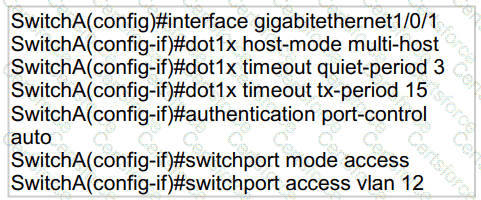
Refer to the exhibit.

Question # 110

An engineer configured wired 802.1x on the network and is unable to get a laptop to authenticate. Which port configuration is missing?

Options:

A.

authentication open


B.

dotlx reauthentication


C.

cisp enable


D.

dot1x pae authenticator


Expert Solution
Questions # 111:

Why is it important to have logical security controls on endpoints even though the users are trained to spot security threats and the network devices already help prevent them?

Options:

A.

to prevent theft of the endpoints


B.

because defense-in-depth stops at the network


C.

to expose the endpoint to more threats


D.

because human error or insider threats will still exist


Expert Solution
Questions # 112:

What is the role of an endpoint in protecting a user from a phishing attack?

Options:

A.

Use Cisco Stealthwatch and Cisco ISE Integration.


B.

Utilize 802.1X network security to ensure unauthorized access to resources.


C.

Use machine learning models to help identify anomalies and determine expected sending behavior.


D.

Ensure that antivirus and anti malware software is up to date


Expert Solution
Questions # 113:

What are two ways a network administrator transparently identifies users using Active Directory on the Cisco WSA? (Choose two.)

Options:

A.

Create an LDAP authentication realm and disable transparent user identification.


B.

Create NTLM or Kerberos authentication realm and enable transparent user identification.


C.

Deploy a separate Active Directory agent such as Cisco Context Directory Agent.


D.

The eDirectory client must be installed on each client workstation.


E.

Deploy a separate eDirectory server; the dent IP address is recorded in this server.


Expert Solution
Questions # 114:

In a federated single sign-on environment, which protocol exchanges XML-based assertions between an identity provider and a service provider for authentication?

Options:

A.

SAML


B.

OAuth 2.0


C.

LDAP


D.

RADIUS


Expert Solution
Questions # 115:

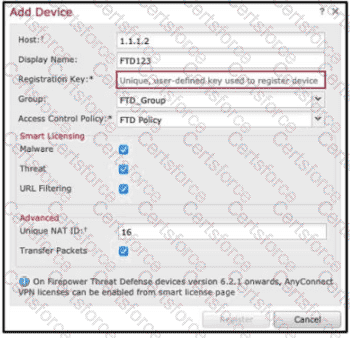
Refer to the exhibit.

Question # 115

An administrator is adding a new Cisco FTD device to their network and wants to manage it with Cisco FMC.

The Cisco FTD is not behind a NAT device. Which command is needed to enable this on the Cisco FTD?

Options:

A.

configure manager add DONTRESOLVE kregistration key >


B.

configure manager add < FMC IP address > < registration key > 16


C.

configure manager add DONTRESOLVE < registration key > FTD123


D.

configure manager add < FMC IP address > < registration key >


Expert Solution
Questions # 116:

Which service allows a user export application usage and performance statistics with Cisco Application Visibility

and control?

Options:

A.

SNORT


B.

NetFlow


C.

SNMP


D.

802.1X


Expert Solution
Questions # 117:

A network engineer has entered the snmp-server user andy myv3 auth sha cisco priv aes 256

cisc0380739941 command and needs to send SNMP information to a host at 10.255.254.1. Which command achieves this goal?

Options:

A.

snmp-server host inside 10.255.254.1 version 3 andy


B.

snmp-server host inside 10.255.254.1 version 3 myv3


C.

snmp-server host inside 10.255.254.1 snmpv3 andy


D.

snmp-server host inside 10.255.254.1 snmpv3 myv3


Expert Solution
Questions # 118:

When a next-generation endpoint security solution is selected for a company, what are two key

deliverables that help justify the implementation? (Choose two.)

Options:

A.

signature-based endpoint protection on company endpoints


B.

macro-based protection to keep connected endpoints safe


C.

continuous monitoring of all files that are located on connected endpoints


D.

email integration to protect endpoints from malicious content that is located in email


E.

real-time feeds from global threat intelligence centers


Expert Solution
Questions # 119:

An organization must add new firewalls to its infrastructure and wants to use Cisco ASA or Cisco FTD.

The chosen firewalls must provide methods of blocking traffic that include offering the user the option to bypass the block for certain sites after displaying a warning page and to reset the connection. Which solution should the organization choose?

Options:

A.

Cisco FTD because it supports system rate level traffic blocking, whereas Cisco ASA does not


B.

Cisco ASA because it allows for interactive blocking and blocking with reset to be configured via the GUI, whereas Cisco FTD does not.


C.

Cisco FTD because it enables interactive blocking and blocking with reset natively, whereas Cisco ASA does not


D.

Cisco ASA because it has an additional module that can be installed to provide multiple blocking capabilities, whereas Cisco FTD does not.


Expert Solution
Questions # 120:

Drag and drop the Cisco CWS redirection options from the left onto the capabilities on the right.
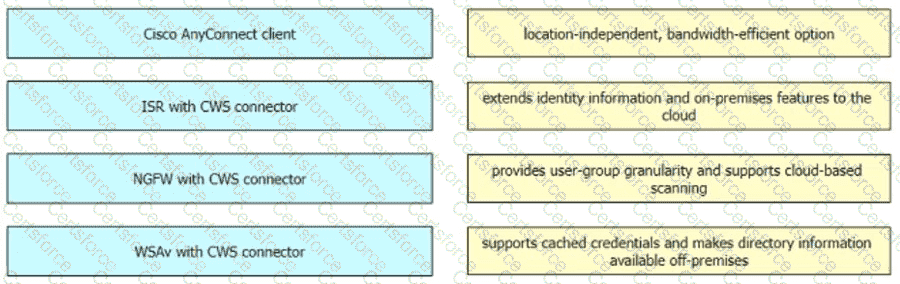
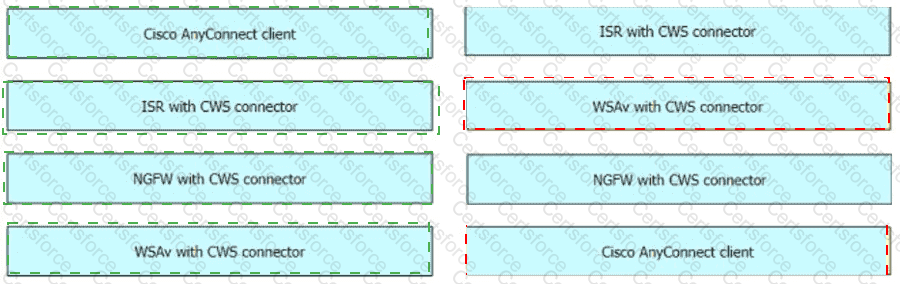
Question # 120


Expert Solution
Viewing page 8 out of 16 pages
Viewing questions 106-120 out of questions