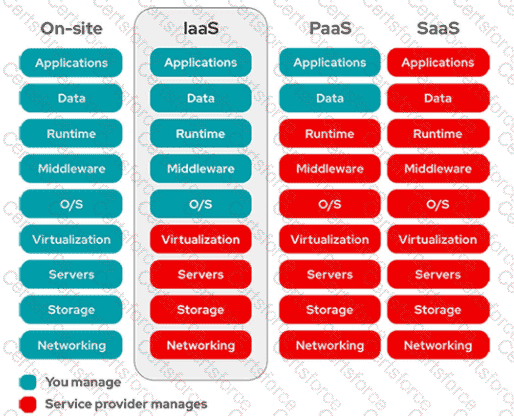
Which two aspects of the cloud PaaS model are managed by the customer but not the provider? (Choose two)
In which two ways does a system administrator send web traffic transparently to the Web Security Appliance?
(Choose two)
A networking team must harden an organization ' s network from VLAN hopping attacks. The team disables Dynamic Trunking Protocol and puts any unused ports in an unused VLAN. A trunk port is used as a trunk link. What must the team configure next to harden the network against VLAN hopping attacks?
An engineer is configuring Dropbox integration with Cisco Cloudlock. Which action must be taken before granting API access in the Dropbox admin console?
Which two configurations must be made on Cisco ISE and on Cisco TrustSec devices to force a session to be adjusted after a policy change is made? (Choose two)
What is the primary role of the Cisco Email Security Appliance?
Which CLI command is used to enable URL filtering support for shortened URLs on the Cisco ESA?
What is a required prerequisite to enable malware file scanning for the Secure Internet Gateway?
Using Cisco Firepower’s Security Intelligence policies, upon which two criteria is Firepower block based?
(Choose two)
A security engineer is deploying an IPsec site-to-site VPN between headquarters and a remote plant, protected by Cisco Secure Firewall Threat Defense managed by Cisco Secure Firewall Management Center. The following configurations have already been completed:
Matching IKEv2 proposals, preshared keys, and IPsec transform sets
Access control rules permitting the traffic
Crypto maps applied to the outside interfaces
VPN traffic exempted from inspection
During a packet capture on the firewall, the engineer observes that the traffic is translated to the public IP address, preventing tunnel establishment. Which configuration action must be performed next?
An engineer is configuring Cisco WSA and needs to enable a separated email transfer flow from the Internet and from the LAN. Which deployment mode must be used to accomplish this goal?
What must be enabled to secure SaaS-based applications?
Refer to the exhibit.
aaa new-model
aaa authentication dot1x default group ISE-SERVERS
aaa authorization network default group ISE-SERVERS
aaa accounting dot1x default start-stop group ISE-SERVERS
!
radius server RADIUS_SRV
address ipv4 172.16.10.12 auth-port 1812 acct-port 1813
key shared-secret C1sc0123
!
aaa group server radius ISE-SERVERS
server name RADIUS_SRV
radius-server vsa send authentication
radius-server vsa send accounting
radius-server attribute 6 on-for-login-auth
radius-server attribute 8 include-in-access-req
radius-server attribute 25 access-request include
ip device tracking
!
interface range GigabitEthernet1/0/1 - 48
switchport
switchport host
authentication priority dot1x mab
authentication order dot1x mab
A security engineer is integrating a new Cisco Catalyst access switch with Cisco ISE to enforce port-based network access control using 802.1X. The AAA RADIUS server group and access interfaces are configured on the Cisco Catalyst switch. Cisco ISE has authentication and authorization policies, the workstation supplicants are configured as expected, and connectivity between the switch and ISE is working. During testing, the workstations fail to trigger authentication sessions, and no RADIUS requests appear in the ISE logs or on the switch interfaces. Which two configuration commands must be added to the Cisco Catalyst switch? (Choose two.)
Which two devices support WCCP for traffic redirection? (Choose two.)
Which Cisco IOS XE command rejects packets with a source IP address that fails a reverse-path-forwarding prefix check on the ingress interface?