
Pre-Winter Sale Special Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: force70

Pass the Cisco CCNP Security 350-701 Questions and answers with CertsForce

Viewing page 9 out of 16 pages
Viewing questions 121-135 out of questions
Questions # 121:

An engineer is configuring cloud logging using a company-managed Amazon S3 bucket for Cisco Umbrella logs. What benefit does this configuration provide for accessing log data?

Options:

A.

It is included m the license cost for the multi-org console of Cisco Umbrella


B.

It can grant third-party SIEM integrations write access to the S3 bucket


C.

No other applications except Cisco Umbrella can write to the S3 bucket


D.

Data can be stored offline for 30 days.


Expert Solution
Questions # 122:

An administrator is establishing a new site-to-site VPN connection on a Cisco IOS router. The organization

needs to ensure that the ISAKMP key on the hub is used only for terminating traffic from the IP address of

172.19.20.24. Which command on the hub will allow the administrator to accomplish this?

Options:

A.

crypto ca identity 172.19.20.24


B.

crypto isakmp key Cisco0123456789 172.19.20.24


C.

crypto enrollment peer address 172.19.20.24


D.

crypto isakmp identity address 172.19.20.24


Expert Solution
Questions # 123:

What is a benefit of a Cisco Secure Email Gateway Virtual as compared to a physical Secure Email Gateway?

Options:

A.

simplifies the distribution of software updates


B.

provides faster performance


C.

provides an automated setup process


D.

enables the allocation of additional resources


Expert Solution
Questions # 124:

A network engineer must prevent endpoints from becoming infected by malicious files. The infrastructure includes Cisco Secure Endpoint, which must execute suspicious files in a cloud sandbox. Which feature must the engineer configure on Cisco Secure Endpoint to meet the requirement?

Options:

A.

Dynamic File Analysis


B.

Orbital Advanced Search


C.

Layer 4 Traffic Monitor


D.

Cisco Application Visibility and Control


Expert Solution
Questions # 125:

An engineer notices traffic interruption on the network. Upon further investigation, it is learned that broadcast

packets have been flooding the network. What must be configured, based on a predefined threshold, to

address this issue?

Options:

A.

Bridge Protocol Data Unit guard


B.

embedded event monitoring


C.

storm control


D.

access control lists


Expert Solution
Questions # 126:

Using Cisco Cognitive Threat Analytics, which platform automatically blocks risky sites, and test unknown sites for hidden advanced threats before allowing users to click them?

Options:

A.

Cisco Identity Services Engine (ISE)


B.

Cisco Enterprise Security Appliance (ESA)


C.

Cisco Web Security Appliance (WSA)


D.

Cisco Advanced Stealthwatch Appliance (ASA)


Expert Solution
Questions # 127:

What are two reasons for implementing a multifactor authentication solution such as Duo Security provide to an

organization? (Choose two)

Options:

A.

flexibility of different methods of 2FA such as phone callbacks, SMS passcodes, and push notifications


B.

single sign-on access to on-premises and cloud applications


C.

integration with 802.1x security using native Microsoft Windows supplicant


D.

secure access to on-premises and cloud applications


E.

identification and correction of application vulnerabilities before allowing access to resources


Expert Solution
Questions # 128:

In which two ways does the Cisco Advanced Phishing Protection solution protect users? (Choose two.)
Options:

A.

It prevents use of compromised accounts and social engineering.


B.

It prevents all zero-day attacks coming from the Internet.


C.

It automatically removes malicious emails from users ' inbox.


D.

It prevents trojan horse malware using sensors.


E.

It secures all passwords that are shared in video conferences.


Expert Solution
Questions # 129:

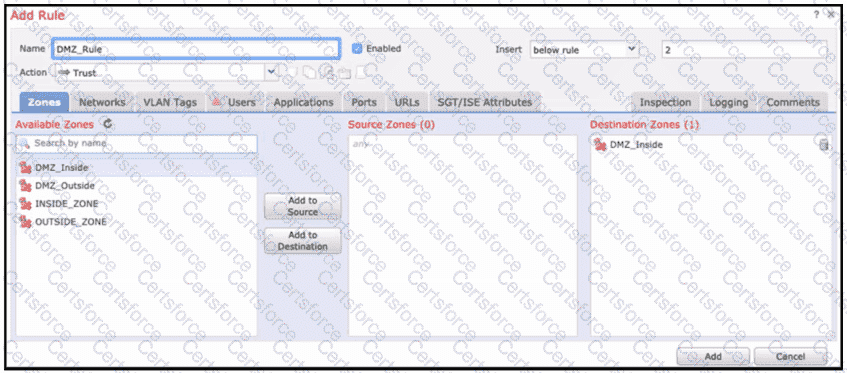
Question # 129

Refer to the exhibit. When configuring this access control rule in Cisco FMC, what happens with the traffic destined to the DMZ_inside zone once the configuration is deployed?

Options:

A.

All traffic from any zone will be allowed to the DMZ_inside zone only after inspection.


B.

No traffic will be allowed through to the DMZ_inside zone regardless of if it ' s trusted or not.


C.

No traffic will be allowed through to the DMZ_inside zone unless it ' s already trusted.


D.

All traffic from any zone to the DMZ_inside zone will be permitted with no further inspection.


Expert Solution
Questions # 130:

Which two features are used to configure Cisco ESA with a multilayer approach to fight viruses and malware?

(Choose two)

Options:

A.

Sophos engine


B.

white list


C.

RAT


D.

outbreak filters


E.

DLP


Expert Solution
Questions # 131:

What is a difference between a DoS attack and a DDoS attack?

Options:

A.

A DoS attack is where a computer is used to flood a server with TCP and UDP packets whereas a DDoS attack is where multiple systems target a single system with a DoS attack


B.

A DoS attack is where a computer is used to flood a server with TCP and UDP packets whereas a DDoS attack is where a computer is used to flood multiple servers that are distributed over a LAN


C.

A DoS attack is where a computer is used to flood a server with UDP packets whereas a DDoS attack is where a computer is used to flood a server with TCP packets


D.

A DoS attack is where a computer is used to flood a server with TCP packets whereas a DDoS attack is where a computer is used to flood a server with UDP packets


Expert Solution
Questions # 132:

With Cisco AMP for Endpoints, which option shows a list of all files that have been executed in your

environment?

Options:

A.

Prevalence


B.

File analysis


C.

Detections


D.

Vulnerable software


E.

Threat root cause


Expert Solution
Questions # 133:

An engineer needs to detect and quarantine a file named abc424400664 zip based on the MD5 signature of the file using the Outbreak Control list feature within Cisco Advanced Malware Protection (AMP) for Endpoints The configured detection method must work on files of unknown disposition Which Outbreak Control list must be configured to provide this?

Options:

A.

Blocked Application


B.

Simple Custom Detection


C.

Advanced Custom Detection


D.

Android Custom Detection


Expert Solution
Questions # 134:

An engineer must deploy a Cisco Secure Web Appliance. Antimalware scanning must use the Outbreak Heuristics antimalware category on files identified as malware before performing any other processes. What must be configured on the Secure Web Appliance to meet the requirements?

Options:

A.

Sophos scanning engine


B.

Webroot scanning engine


C.

McAfee scanning engine


D.

Adaptive Scanning


Expert Solution
Questions # 135:

Which DoS attack uses fragmented packets in an attempt to crash a target machine?

Options:

A.

teardrop


B.

smurf


C.

LAND


D.

SYN flood


Expert Solution
Viewing page 9 out of 16 pages
Viewing questions 121-135 out of questions