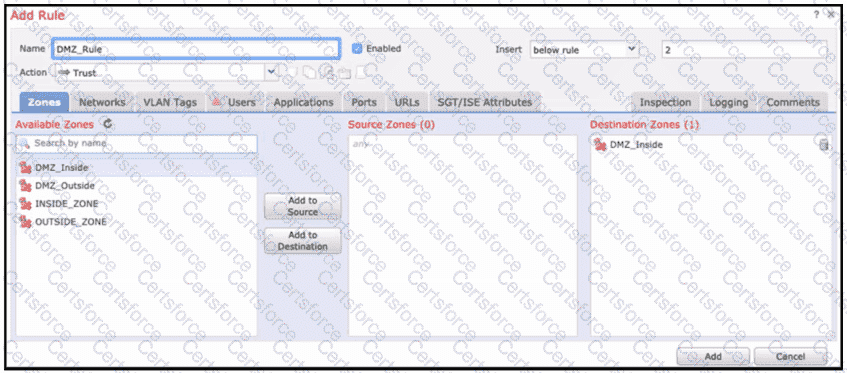
Refer to the exhibit. When configuring this access control rule in Cisco FMC, what happens with the traffic destined to the DMZ_inside zone once the configuration is deployed?
A.
All traffic from any zone will be allowed to the DMZ_inside zone only after inspection.
B.
No traffic will be allowed through to the DMZ_inside zone regardless of if it ' s trusted or not.
C.
No traffic will be allowed through to the DMZ_inside zone unless it ' s already trusted.
D.
All traffic from any zone to the DMZ_inside zone will be permitted with no further inspection.
Chosen Answer:
This is a voting comment (?). You can switch to a simple comment. It is better to Upvote an existing comment if you don't have anything to add.


Submit