Pre-Winter Sale Special Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: force70

Pass the Cisco CCNP Security 350-701 Questions and answers with CertsForce

Viewing page 4 out of 16 pages
Viewing questions 46-60 out of questions
Questions # 46:

What must be configured in Cisco ISE to enforce reauthentication of an endpoint session when an endpoint is

deleted from an identity group?

Options:

A.

posture assessment


B.

CoA


C.

external identity source


D.

SNMP probe


Expert Solution
Questions # 47:

Which function is performed by certificate authorities but is a limitation of registration authorities?

Options:

A.

accepts enrollment requests


B.

certificate re-enrollment


C.

verifying user identity


D.

CRL publishing


Expert Solution
Questions # 48:

Which solution detects threats across a private network, public clouds, and encrypted traffic?

Options:

A.

Cisco Stealthwatch


B.

Cisco CTA


C.

Cisco Encrypted Traffic Analytics


D.

Cisco Umbrella


Expert Solution
Questions # 49:

A pharmaceutical research facility has implemented a “Clean Room” network segment to protect sensitive research data and automated manufacturing equipment. Strict compliance requirements mandate that all network traffic logs from the Cisco Secure Firewall serving the segment be forwarded to Splunk for auditing. A Splunk Universal Forwarder is deployed locally on the log-collection servers to monitor syslog files. The engineer must configure the Universal Forwarder to monitor the local syslog files and assign a specific source type for proper ingestion into Splunk. Which stanza configuration must be used to meet the requirements?

Options:

A.

inputs.conf using [monitor:///var/log/syslog]


B.

server.conf using [monitor:///syslog]


C.

props.conf using [syslog]


D.

outputs.conf using [tcpout]


Expert Solution
Questions # 50:

A manufacturing company contracted an external software vendor to develop an application that dynamically creates marketing messages personalized to the business and audience. To ensure that communication between the sender and recipient email addresses does not create false positives, an exception rule must be configured in Cisco Secure Email Threat Defense. Which configuration must be performed?
Options:

A.

Implement an Exception Rule with a wildcard email address.


B.

Add a Policy Exception Rule with a Sender/Recipient pair set.


C.

Apply a sender-based Policy Exception Rule.


D.

Configure a recipient-based Policy Exception Rule.


Expert Solution
Questions # 51:

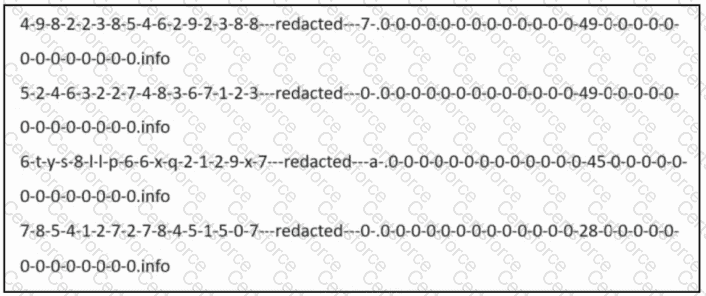
Question # 51

Refer to the exhibit. Consider that any feature of DNS requests, such as the length of the domain name and the number of subdomains, can be used to construct models of expected behavior to which observed values can be compared. Which type of malicious attack are these values associated with?

Options:

A.

W32/AutoRun worm


B.

HeartBleed SSL Bug


C.

Spectre Worm


D.

Eternal Blue Windows


Expert Solution
Questions # 52:

Which IPS engine detects ARP spoofing?

Options:

A.

Atomic ARP Engine


B.

Service Generic Engine


C.

ARP Inspection Engine


D.

AIC Engine


Expert Solution
Questions # 53:

What are two features of NetFlow flow monitoring? (Choose two)

Options:

A.

Can track ingress and egress information


B.

Include the flow record and the flow importer


C.

Copies all ingress flow information to an interface


D.

Does not required packet sampling on interfaces


E.

Can be used to track multicast, MPLS, or bridged traffic


Expert Solution
Questions # 54:

Which type of encryption uses a public key and private key?

Options:

A.

Asymmetric


B.

Symmetric


C.

Linear


D.

Nonlinear


Expert Solution
Questions # 55:

An engineer is configuring 802.1X authentication on Cisco switches in the network and is using CoA as a mechanism. Which port on the firewall must be opened to allow the CoA traffic to traverse the network?

Options:

A.

TCP 6514


B.

UDP 1700


C.

TCP 49


D.

UDP 1812


Expert Solution
Questions # 56:

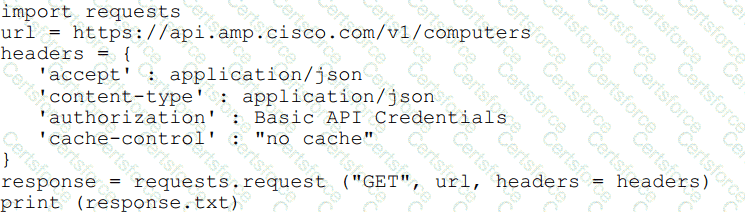
Refer to the exhibit.

Question # 56

What will happen when this Python script is run?

Options:

A.

The compromised computers and malware trajectories will be received from Cisco AMP


B.

The list of computers and their current vulnerabilities will be received from Cisco AMP


C.

The compromised computers and what compromised them will be received from Cisco AMP


D.

The list of computers, policies, and connector statuses will be received from Cisco AMP


Expert Solution
Questions # 57:

Which Cisco security solution secures public, private, hybrid, and community clouds?

Options:

A.

Cisco ISE


B.

Cisco ASAv


C.

Cisco Cloudlock


D.

Cisco pxGrid


Expert Solution
Questions # 58:

Which Talos reputation center allows for tracking the reputation of IP addresses for email and web traffic?

Options:

A.

IP and Domain Reputation Center


B.

File Reputation Center


C.

IP Slock List Center


D.

AMP Reputation Center


Expert Solution
Questions # 59:

A large organization wants to deploy a security appliance in the public cloud to form a site-to-site VPN

and link the public cloud environment to the private cloud in the headquarters data center. Which Cisco

security appliance meets these requirements?

Options:

A.

Cisco Cloud Orchestrator


B.

Cisco ASAV


C.

Cisco WSAV


D.

Cisco Stealthwatch Cloud


Expert Solution
Questions # 60:

What is a benefit of using Cisco FMC over Cisco ASDM?

Options:

A.

Cisco FMC uses Java while Cisco ASDM uses HTML5.


B.

Cisco FMC provides centralized management while Cisco ASDM does not.


C.

Cisco FMC supports pushing configurations to devices while Cisco ASDM does not.


D.

Cisco FMC supports all firewall products whereas Cisco ASDM only supports Cisco ASA devices


Expert Solution
Viewing page 4 out of 16 pages
Viewing questions 46-60 out of questions