
Refer to the exhibit.
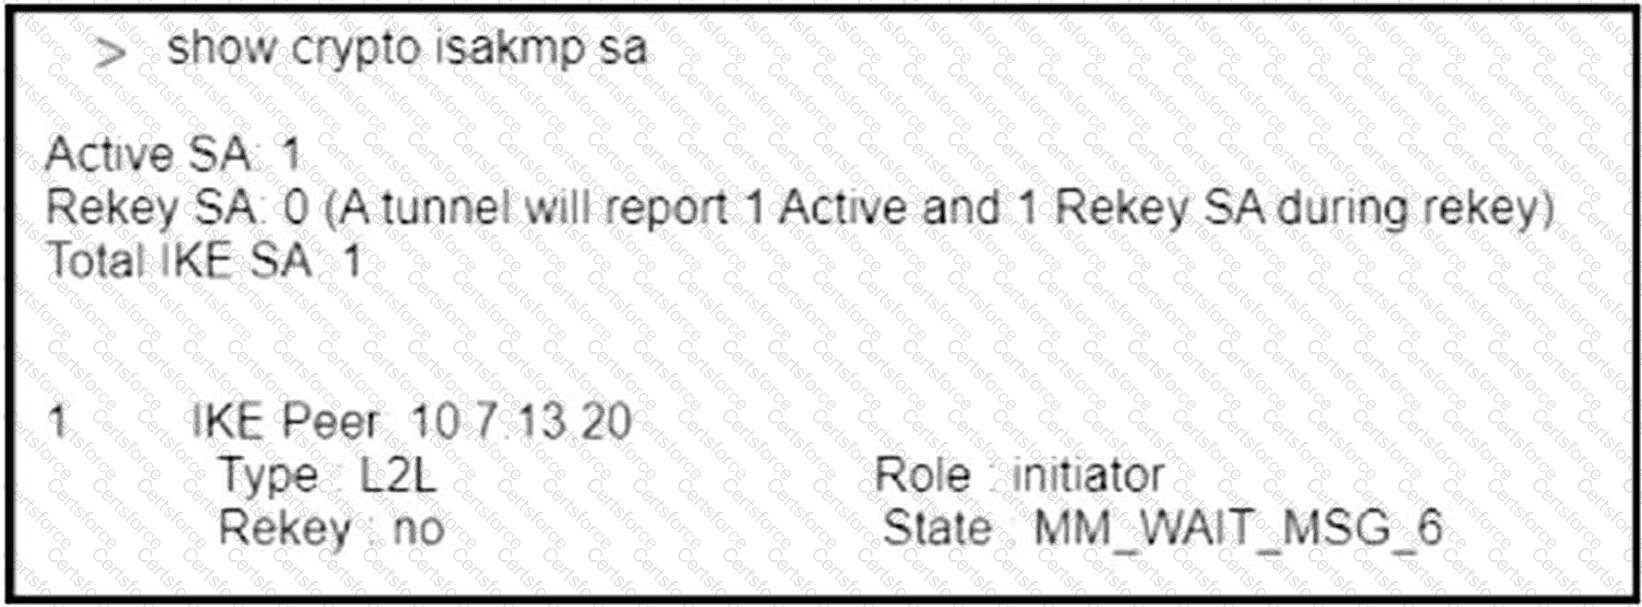
During the rollout of a new site-to-site VPN between a headquarters Cisco Secure Firewall Threat Defense device and a partner firewall, the tunnel never completes IKEv1 Phase 1 and remains in the MM_WAIT_MSG_6 state. Reachability between the firewalls over the Internet is verified, ISAKMP UDP port 500 is permitted end-to-end, and the IKE Phase 1 policy parameters—including encryption, hashing, DH group, and lifetime—match exactly on both ends. Which configuration action must be performed to resolve the issue?

Submit