
Which of the following provides the MOST useful information to trace the impact of aggregated risk across an organization ' s technical environment?
Which of the following emerging technologies is frequently used for botnet distributed denial of service (DDoS) attacks?
An organization wants to launch a campaign to advertise a new product Using data analytics, the campaign can be targeted to reach potential customers. Which of the following should be of GREATEST concern to the risk practitioner?
Which of the following is the PRIMARY consideration when determining the impact to an organization after the discovery of malware on an endpoint device?
When reporting on the performance of an organization ' s control environment including which of the following would BEST inform stakeholders risk decision-making?
An organization has implemented a policy requiring staff members to take a minimum of five consecutive days ' leave per year to mitigate the risk of malicious insider activities. Which of the following is the BEST key performance indicator (KPI) of the effectiveness of this policy?
Which of the following is the BEST control to detect an advanced persistent threat (APT)?
Who should be accountable for monitoring the control environment to ensure controls are effective?
Which of the following would BEST help identify the owner for each risk scenario in a risk register?
Which of the following provides the MOST insight regarding an organization ' s risk culture?
Which of the following is MOST likely to be impacted when a global organization is required by law to implement a new data protection regulation across its operations?
An information system for a key business operation is being moved from an in-house application to a Software as a Service (SaaS) vendor. Which of the following will have the GREATEST impact on the ability to monitor risk?
During testing, a risk practitioner finds the IT department ' s recovery time objective (RTO) for a key system does not align with the enterprise ' s business continuity plan (BCP). Which of the following should be done NEXT?
Which of the following is the BEST metric to demonstrate the effectiveness of an organization’s software testing program?
Which of the following management action will MOST likely change the likelihood rating of a risk scenario related to remote network access?
A global organization has implemented an application that does not address all privacy requirements across multiple jurisdictions. Which of the following risk responses has the organization adopted with regard to privacy requirements?
Which of the following should be the PRIMARY goal of developing information security metrics?
Which of the following is the MAIN benefit of involving stakeholders in the selection of key risk indicators (KRIs)?
The following is the snapshot of a recently approved IT risk register maintained by an organization ' s information security department.
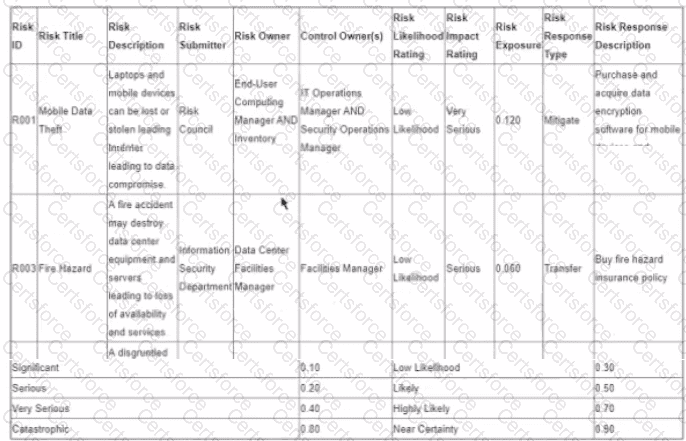
After implementing countermeasures listed in ‘’Risk Response Descriptions’’ for each of the Risk IDs, which of the following component of the register MUST change?
A monthly payment report is generated from the enterprise resource planning (ERP) software to validate data against the old and new payroll systems. What is the BEST way to mitigate the risk associated with data integrity loss in the new payroll system after data migration?
When developing a business continuity plan (BCP), it is MOST important to:
Which of the following provides the MOST up-to-date information about the effectiveness of an organization ' s overall IT control environment?
What is the PRIMARY reason an organization should include background checks on roles with elevated access to production as part of its hiring process?
Which of the following is the MOST appropriate risk owner for a payroll application that has recently been outsourced to a cloud software provider?
Which of the following is the BEST way to quantify the likelihood of risk materialization?
Which of the following BEST enables effective risk reporting to the board of directors?
During an acquisition, which of the following would provide the MOST useful input to the parent company ' s risk practitioner when developing risk scenarios for the post-acquisition phase?
Which of the following is the BEST recommendation when a key risk indicator (KRI) is generating an excessive volume of events?
An application development team has a backlog of user requirements for a new system that will process insurance claim payments for customers. Which of the following should be the MOST important consideration for a risk-based review of the user requirements?
Which of the following should be of GREATEST concern when reviewing the results of an independent control assessment to determine the effectiveness of a vendor ' s control environment?
Which of the following is the PRIMARY goal of enterprise architecture (EA)?
Which of the following is the MOST useful information for a risk practitioner when planning response activities after risk identification?
A risk practitioner has been notified that an employee sent an email in error containing customers ' personally identifiable information (Pll). Which of the following is the risk practitioner ' s BEST course of action?
Which of the following is the BEST method to identify unnecessary controls?
Which of the following is the GREATEST concern associated with redundant data in an organization ' s inventory system?
Which of the following is the BEST indication of an improved risk-aware culture following the implementation of a security awareness training program for all employees?
An organization with a large number of applications wants to establish a security risk assessment program. Which of the following would provide the MOST useful information when determining the frequency of risk assessments?
Mapping open risk issues to an enterprise risk heat map BEST facilitates:
Which of the following is the MOST important characteristic of a key risk indicator (KRI) to enable decision-making?
Which of the following is the MOST effective way to integrate business risk management with IT operations?
Which of the following is the GREATEST benefit of identifying appropriate risk owners?
A data processing center operates in a jurisdiction where new regulations have significantly increased penalties for data breaches. Which of the following elements of the risk register is MOST important to update to reflect this change?
Management has required information security awareness training to reduce the risk associated with credential compromise. What is the BEST way to assess the effectiveness of the training?
A risk practitioner is summarizing the results of a high-profile risk assessment sponsored by senior management. The BEST way to support risk-based decisions by senior management would be to:
Which of the following events is MOST likely to trigger the need to conduct a risk assessment?
An application runs a scheduled job that compiles financial data from multiple business systems and updates the financial reporting system. If this job runs too long, it can delay financial reporting. Which of the following is the risk practitioner ' s BEST recommendation?
A maturity model will BEST indicate:
Which of the following should be the MOST important consideration when performing a vendor risk assessment?
An organization is planning to move its application infrastructure from on-premises to the cloud. Which of the following is the BEST course of the actin to address the risk associated with data transfer if the relationship is terminated with the vendor?
