
Pre-Winter Sale Special Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: force70

Isaca Certified in Risk and Information Systems Control CRISC Question # 319 Topic 32 Discussion

Isaca Certified in Risk and Information Systems Control CRISC Question # 319 Topic 32 Discussion

CRISC Exam Topic 32 Question 319 Discussion:
Question #: 319
Topic #: 32

The following is the snapshot of a recently approved IT risk register maintained by an organization ' s information security department.
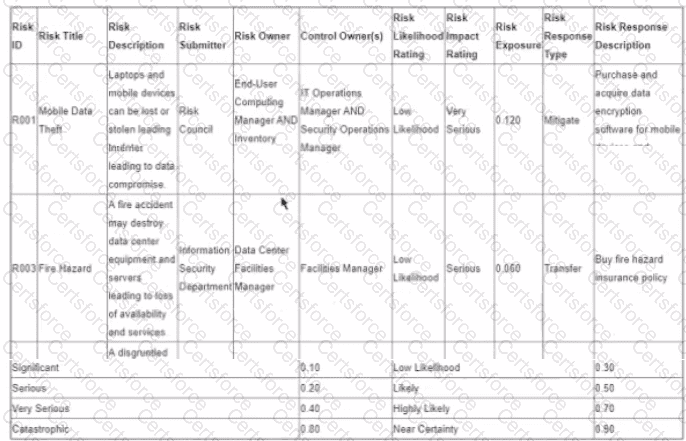
CRISC Question 319

After implementing countermeasures listed in ‘’Risk Response Descriptions’’ for each of the Risk IDs, which of the following component of the register MUST change?


A.

Risk Impact Rating


B.

Risk Owner


C.

Risk Likelihood Rating


D.

Risk Exposure


Get Premium CRISC Questions

Contribute your Thoughts:


Chosen Answer:
This is a voting comment (?). It is better to Upvote an existing comment if you don't have anything to add.