
Halloween Sale Special Limited Time 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: CFsave75

Pass the Fortinet NSE 7 Network Security Architect NSE7_SSE_AR-26 Questions and answers with CertsForce

Viewing page 3 out of 4 pages
Viewing questions 21-30 out of questions
Questions # 21:

Refer to the exhibit that shows event logs on FortiGate. Based on the output shown in the exhibit, what can you say about the tunnels on this device?
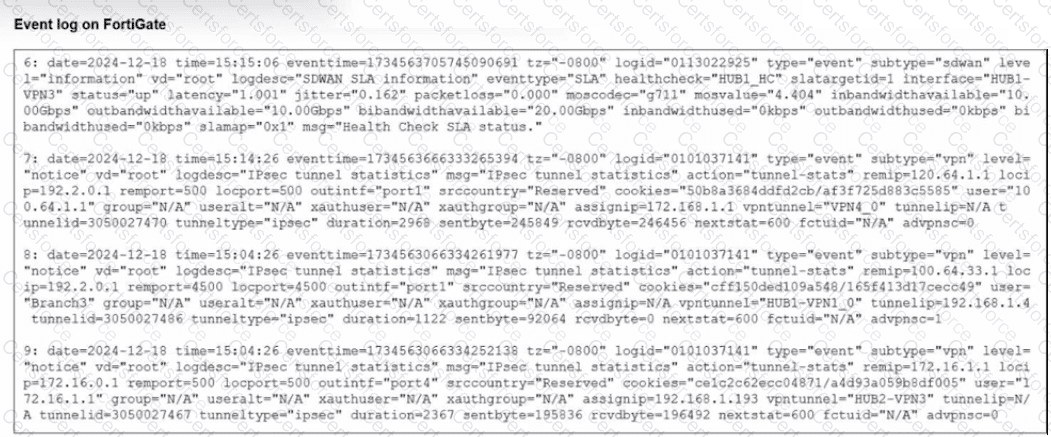
Question # 21

Exhibit 1

Options:

A.

The master tunnel HUB2-VPN3 cannot accept ADVPN shortcuts.


B.

The device steers voice traffic through the VPN tunnel HUB1-VPN3.


C.

The VPN tunnel HUB1-VPN1_0 is a shortcut tunnel.


D.

There is one shortcut tunnel built from master tunnel VPN4.


Expert Solution
Questions # 22:

You are planning a large SD-WAN deployment with approximately 1000 spokes and want to allow ADVPN between the spokes. Some remote sites use FortiSASE to connect to the company ' s SD-WAN hub. Which overlay routing configuration should you use?

Options:

A.

BGP on loopback with dynamic BGP for ADVPN shortcut routing.


B.

BGP on loopback with IPsec phase 2 selectors for ADVPN shortcut routing.


C.

BGP per overlay with dynamic BGP for ADVPN shortcut routing.


D.

BGP per overlay with BGP next-hop convergence for ADVPN shortcut routing.


Expert Solution
Questions # 23:

Refer to the exhibit.

Which SD-WAN rule and interface uses FortiGate to steer the traffic from the LAN subnet 10.0.1.0/24 to the corporate server 10.2.5.254?
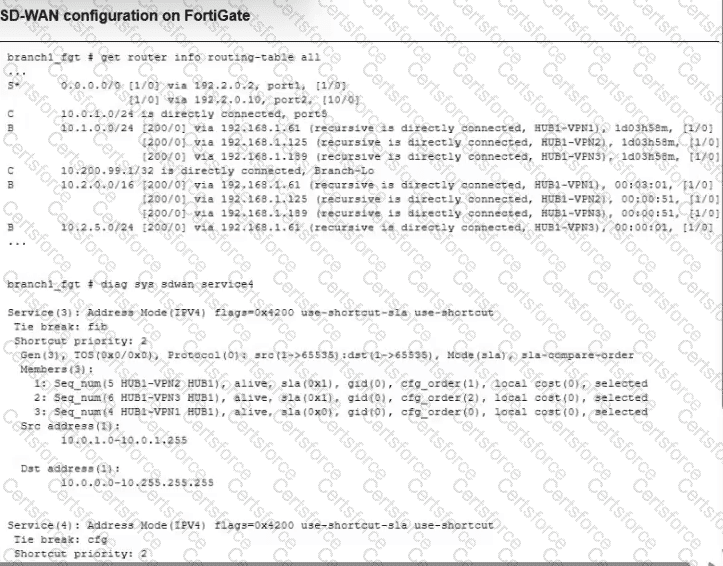
Question # 23

Exhibit — SD-WAN rule and routing outputs

Options:

A.

SD-WAN service rule 3 and interface HUB1-VPN3.


B.

SD-WAN service rule 3 and interface HUB1-VPN2.


C.

SD-WAN service rule 4 and interface port2.


D.

SD-WAN service rule 4 and port1 or port2.


Expert Solution
Questions # 24:

Refer to the exhibits.

The SD-WAN zones and members configuration of two branch devices are shown.

The two branch devices are part of the same hub-and-spoke topology and connect to the same hub. The devices are configured to allow auto-discovery VPN (ADVPN). The configuration on the hub allows the initial communication between the two spokes.

When traffic flows require it, between which interfaces can the devices establish shortcuts?
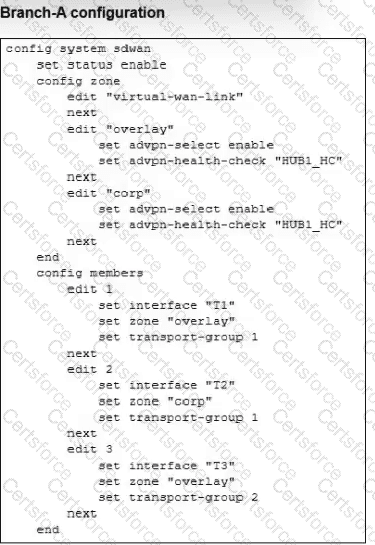
Question # 24

Exhibit — Branch-A SD-WAN zone and transport group

The visible recording shows the Branch-A configuration; the Branch-B configuration is not displayed in the captured video frame.

Options:

A.

Any interface in the overlay zones


B.

Between T2 on Branch-A and TB on Branch-B


C.

Between T1 on Branch-A and TA on Branch-B


D.

Any interface that belongs to the same zone


Expert Solution
Questions # 25:

Refer to the exhibits.

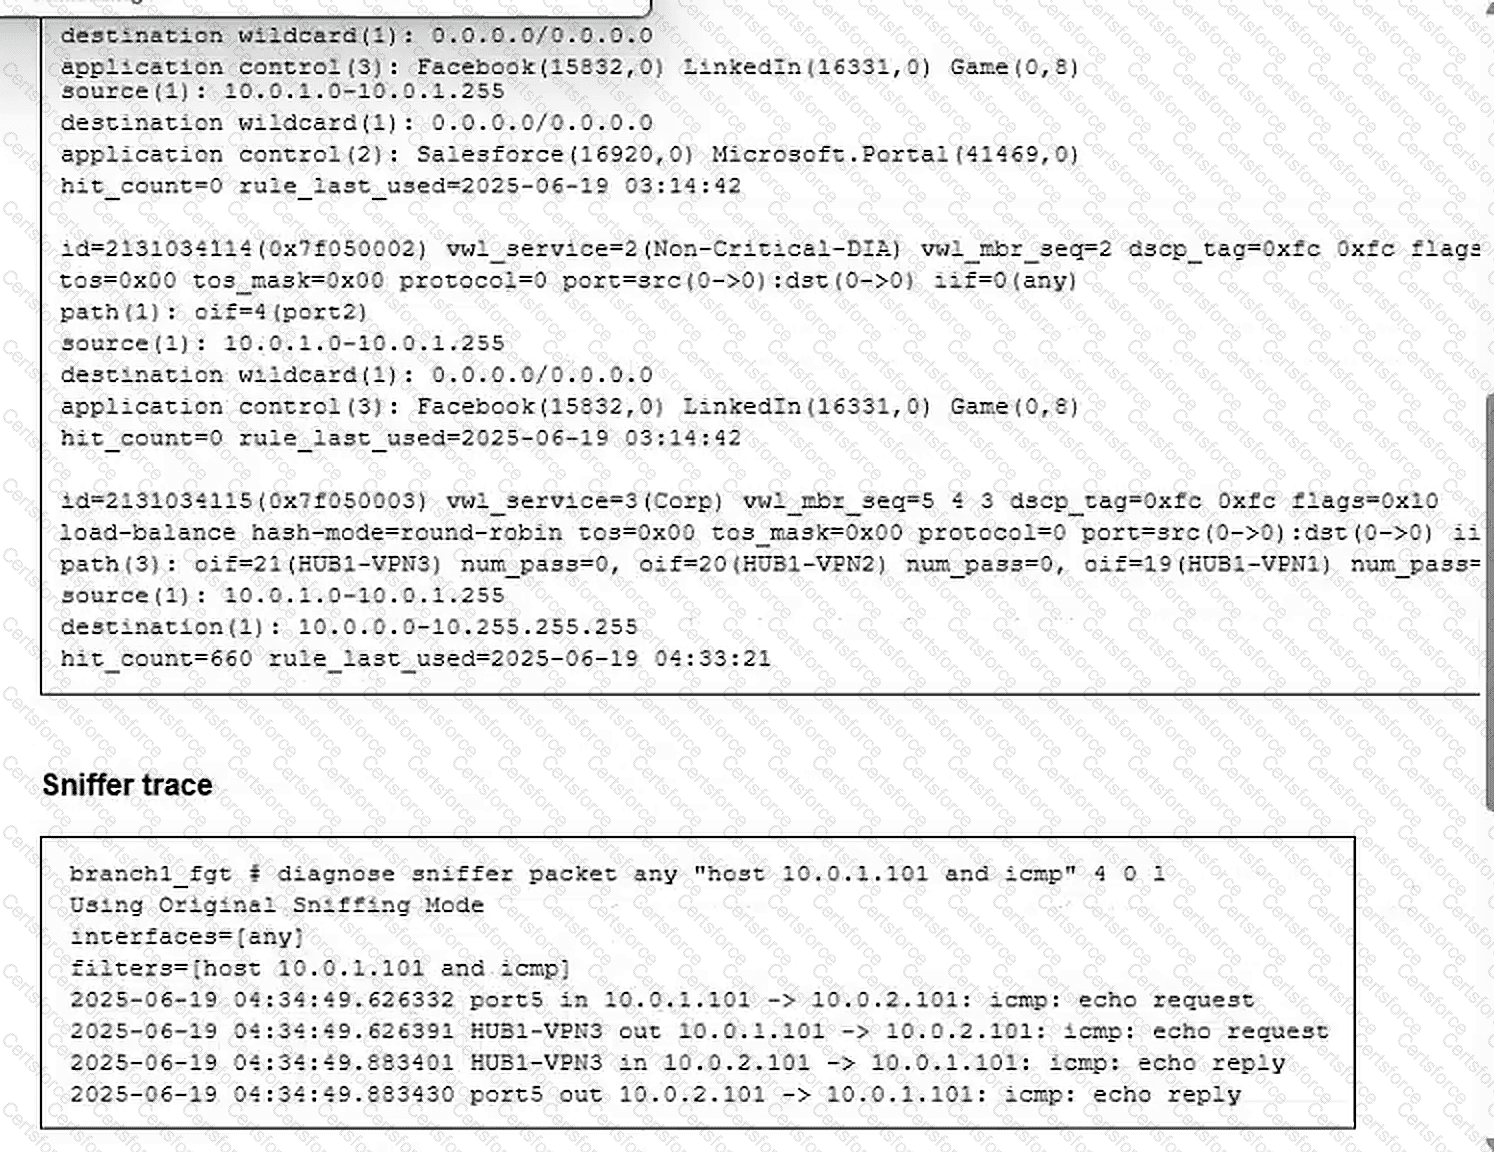
You collected the output shown in the exhibits and want to know which interface HTTP traffic will flow through from the user device 10.0.1.101 to the corporate web server 10.0.0.126.

All SD-WAN links are stable.

Which interface will use FortiGate to steer the traffic?
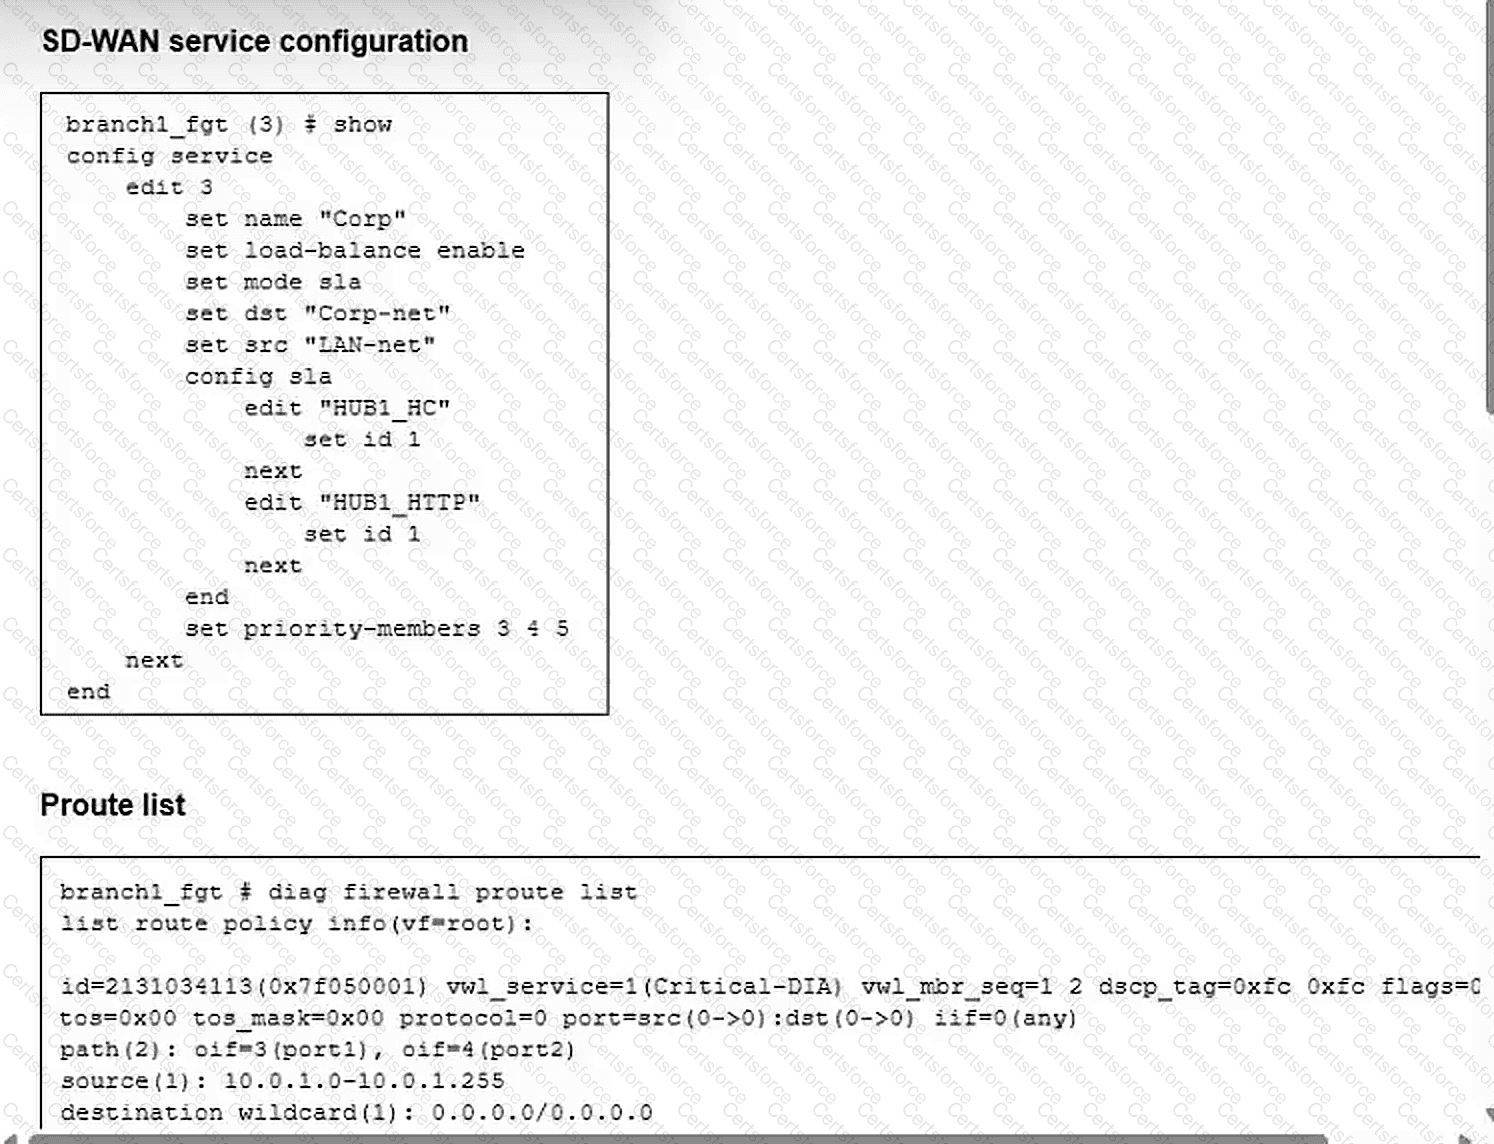
Question # 25

Exhibit 1 — SD-WAN service configuration and route list
Question # 25

Exhibit 2 — SD-WAN route selection and packet sniffer

Options:

A.

Only port2


B.

Only HUB1-VPN3


C.

Either port1 or port2


D.

Either HUB1-VPN1, HUB1-VPN2, or HUB1-VPN3


Expert Solution
Questions # 26:

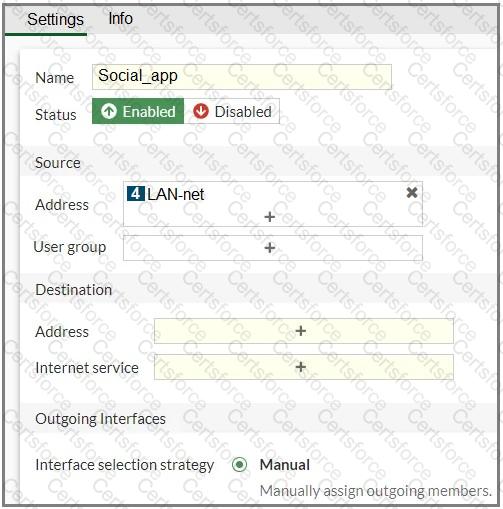
Refer to the exhibit. You configure SD-WAN on a standalone FortiGate device. You want to create an SD-WAN rule that steers Facebook and Linkedin traffic through the less costly internet link. The FortiGate GUI page appears as shown in the exhibit. What should you do to set Facebook and LinkedIn as destinations?
Question # 26

Exhibit 1

Options:

A.

Install a license to allow applications as destinations of SD-WAN rules.


B.

In the Internet service field, select Facebook and LinkedIn.


C.

Enable the applications as destinations of the SD-WAN rule feature visibility.


D.

You cannot configure applications as destinations of an SD-WAN rule on a standalone FortiGate device.


Expert Solution
Questions # 27:

A customer wants to ensure secure access for private applications for their users by replacing their VPN.

Which two SASE technologies can you use to accomplish this task? (Choose two.)

Options:

A.

SD-WAN on-ramp


B.

zero trust network access (ZTNA)


C.

secure SD-WAN


D.

secure web gateway (SWG) and cloud access security broker (CASB)


Expert Solution
Questions # 28:

What is the maximum number of Secure Private Access (SPA) service connections (SPA hubs) supported in the SPA use case?

Options:

A.

4


B.

16


C.

8


D.

12


Expert Solution
Questions # 29:

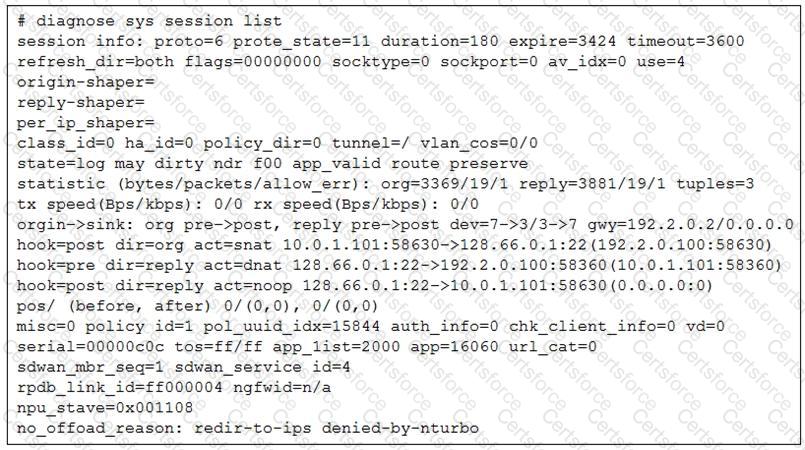
Refer to the exhibit. The administrator configured the SD-WAN rule ID 4 with two members (port1 and port2) and strategy lowest cost (SLA). What are the two characteristics of the session shown in the exhibit? (Choose two.)
Question # 29

Exhibit 1

Options:

A.

FortiGate steered this flow according to an SD-WAN rule 4.


B.

FortiGate will never re-evaluate this session.


C.

FortiGate steered this flow according to the application detected and the outgoing interface is port3.


D.

FortiGate will re-evaluate this session if the outgoing interface goes down.


Expert Solution
Questions # 30:

The SD-WAN overlay template helps to prepare SD-WAN deployments. To complete the tasks performed by the SD-WAN overlay template, the administrator must perform some post-run tasks. What are two mandatory post-run tasks that must be performed? (Choose two.)

Options:

A.

Configure routing through the overlay tunnels created by the SD-WAN overlay template.


B.

Create policy packages and assign them to the branch devices.


C.

Assign a hub id metadata variable to each hub device.


D.

Configure SD-WAN rules


E.

Assign an sdwan_id metadata variable to each device (branch and hub)


Expert Solution
Viewing page 3 out of 4 pages
Viewing questions 21-30 out of questions