
Halloween Sale Special Limited Time 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: CFsave75

Pass the Fortinet NSE 7 Network Security Architect NSE7_SSE_AR-26 Questions and answers with CertsForce

Viewing page 1 out of 4 pages
Viewing questions 1-10 out of questions
Questions # 1:

You used the HUB IPsec_Recommended and the BRANCH IPsec_Recommended templates to define the overlay topology. Then, you used the SD-WAN template to define the SD-WAN members, rules, and performance SLAs. You applied the changes to the devices and want to use the FortiManager monitors menu to get a graphical view that shows the status of each SD-WAN member. Which statement best explains how to obtain this graphical view?

Options:

A.

Use the SD-WAN monitor template view to get a map view of the branches, hub, and tunnel status, including the SLA pass or missed status.


B.

Use the SD-WAN monitor table view to get a donut view and a table view that shows the status of each SD-WAN member, including the SLA pass or missed status.


C.

Use the VPN monitor map view to get a map view of the branches, hub, and tunnel status, including the SLA pass or missed status.


D.

Use the SD-WAN monitor asset view to get a donut view and a table view that shows the status of each device and the SLA status of each SD-WAN member.


Expert Solution
Questions # 2:

An SD-WAN member is no longer used to steer SD-WAN traffic. The administrator updated the SD-WAN configuration and deleted the unused member. After the configuration update, users report that some destinations are unreachable. You confirm that the affected flow does not match an SD-WAN rule. What could be a possible cause of the traffic interruption?

Options:

A.

FortiGate, with SD-WAN enabled, cannot route traffic through interfaces that are not SD-WAN members.


B.

FortiGate can remove some static routes associated with an interface when the member is removed from SD-WAN.


C.

FortiGate removes the layer 3 settings for interfaces that are removed from the SD-WAN configuration.


D.

FortiGate administratively brings down interfaces when they are removed from the SD-WAN configuration.


Expert Solution
Questions # 3:

Which two matching traffic criteria are available to steer traffic in SD-WAN rules?

Options:

A.

Physical interface type


B.

BGP attributes


C.

Application categories


D.

Internet Service Database (ISDB)


Expert Solution
Questions # 4:

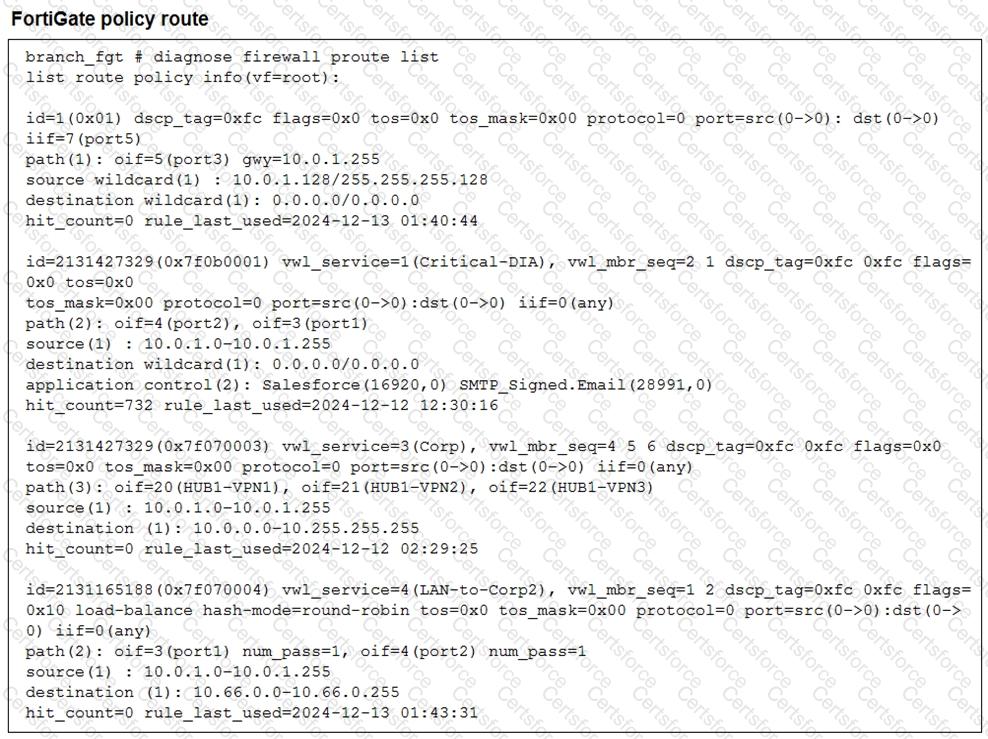
Refer to the exhibit. What conclusions can you draw about the traffic received by FortiGate originating from the source LAN device 10.0.1.133 and destined for the company’s SMTP mail server at 10.66.0.125?
Question # 4

Exhibit 1

Options:

A.

FortiGate steers the traffic from the LAN device 10.0.1.133 to the company SMTP mail server 10.66 0.125 through port3.


B.

ForliGate steers the traffic from the LAN device 10.0.1.133 to the company SMTP mail server 10.66.0.125 through port2.


C.

FortiGate steers the traffic from the LAN device 10.0.1.133 to the company SMTP mail server 10.66.0.125 through the SD-WAN member ID 4.


D.

FortiGate steers the traffic from the LAN device 10.0.1.133 to the SMTP mail server 10.66.0.125 through the SD-WAN member ID 1 or 2.


Expert Solution
Questions # 5:

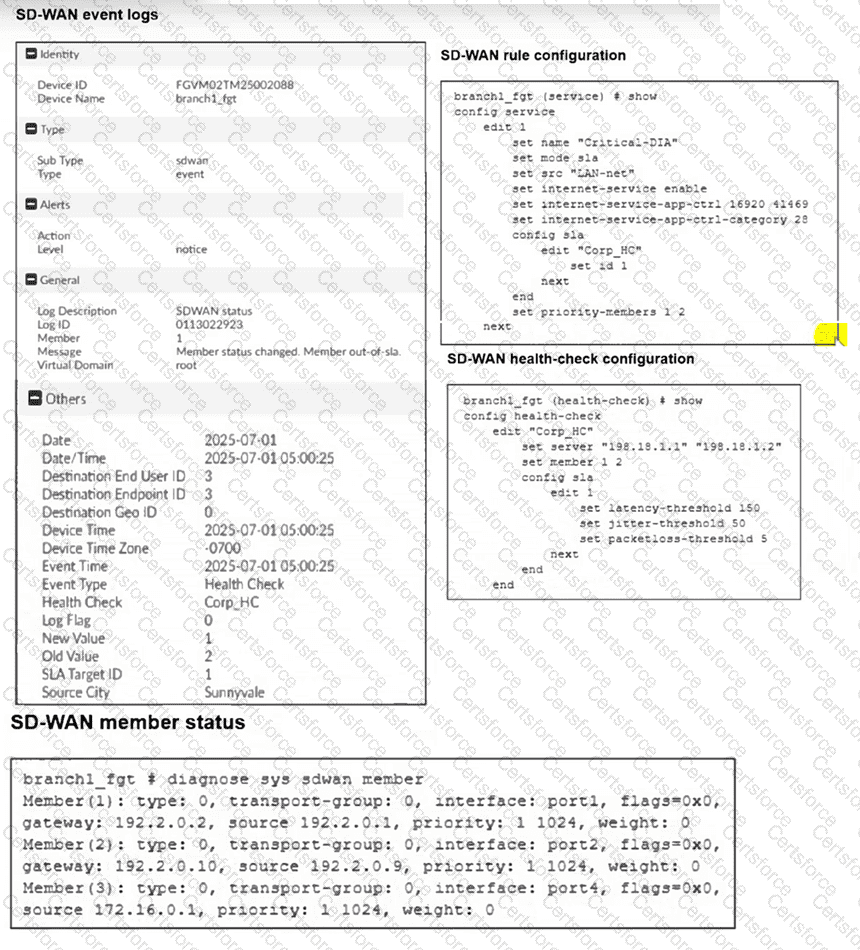
Refer to the exhibits. Two SD-WAN event logs, the member status, the SD-WAN rule configuration, and the health-check configuration for a FortiGate device are shown. Immediately after the log messages are displayed, how will the FortiGate steer the traffic based on the information shown in the exhibits? Choose one answer.
Question # 5

Exhibit 1

Options:

A.

FortiGate skips SD-WAN rule ID 1.


B.

FortiGate uses port2 to steer the traffic for SD-WAN rule ID 1.


C.

FortiGate uses port1 to steer the traffic for SD-WAN rule ID 1.


D.

FortiGate uses port1 or port2 to steer the traffic for SD-WAN rule ID 1.


Expert Solution
Questions # 6:

Refer to the exhibit.

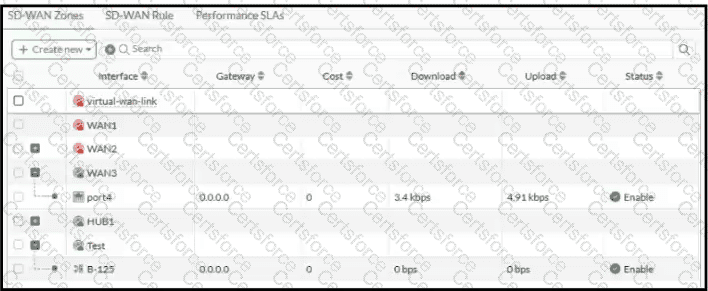
An SD-WAN zone configuration on the FortiGate GUI is shown.

What can you conclude about the zone and member configuration on this device?
Question # 6

Exhibit — FortiGate SD-WAN zones

Options:

A.

The WAN2 zone contains no member.


B.

You can delete any zone with the red icon.


C.

You can delete only the WAN1 zone.


D.

The HUB1 zone contains no member.


Expert Solution
Questions # 7:

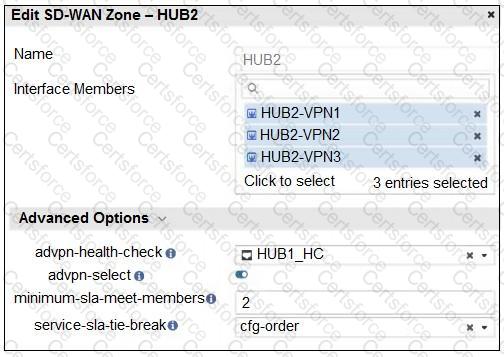
Refer to the exhibit that shows an SD-WAN zone configuration on the FortiManager GUI. Based on the exhibit, how will the FortiGate device behave after it receives this configuration?
Question # 7

Exhibit 1

Options:

A.

The configuration instructs FortiGate to choose an ADVPN shortcut based on SD-WAN information.


B.

The configuration instructs FortiGate to allow ADVPN shortcuts for the tunnels of this SD-WAN zone.


C.

The configuration instructs FortiGate to establish shortcuts only when at least two members meet the SLA target.


D.

The configuration instructs FortiGate to establish shortcuts only for overlay interfaces that meet the SLA target HUB1_HC.


Expert Solution
Questions # 8:

What are three characteristics of the provisioning templates available on FortiManager? (Choose three.)

Options:

A.

A CLI template can be of type CLI script or Perl script.


B.

Each template group can contain up to three IPsec tunnel templates.


C.

A template group can include a system template and an SD-WAN template.


D.

A CLI template group can contain CLI templates of different types.


E.

CLI templates are applied in order, from top to bottom.


Expert Solution
Questions # 9:

Refer to the exhibit. Which statement best describe the role of the ADVPN device in handling traffic?
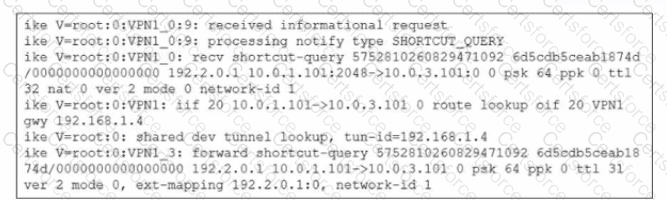
Question # 9

Exhibit 1

Options:

A.

This is a hub that has received a query from a spoke and has forwarded it to another spoke.


B.

This is a hub in a dual-region topology. The remote hub tunnel ID is 10.0.2.101.


C.

This is a spoke that has received a shortcut query from another spoke and has forwarded the response to its hub.


D.

This is a spoke. The kernel received a shortcut request and forwards the query to another spoke.


Expert Solution
Questions # 10:

SD-WAN interacts with many other FortiGate features. Some of them are required to allow SD-WAN to steer the traffic. Which three configuration elements that you must configure before FortiGate can steer traffic according to SD-WAN rules? (Choose three.)

Options:

A.

Firewall policies


B.

Interfaces


C.

Security profiles


D.

Traffic shaping


E.

Routing


Expert Solution
Viewing page 1 out of 4 pages
Viewing questions 1-10 out of questions