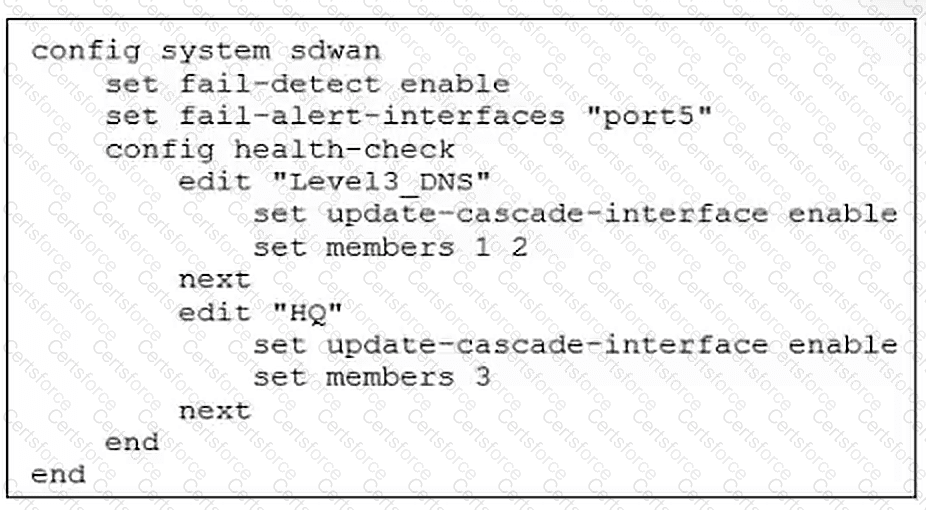
The exhibit demonstrates the SD-WAN cascade interface functionality, which propagates a failure detected on monitored WAN links to a designated physical interface.
The configuration includes:
config system sdwan
set fail-detect enable
set fail-alert-interfaces " port5 "
Both configured performance SLAs also enable update-cascade-interface , allowing the SD-WAN health-monitoring subsystem to control the state of the designated alert interface.
Option B is correct because FortiGate restores port5 when at least one monitored SD-WAN member is alive. When all monitored members fail, FortiGate administratively brings port5 down. Once an eligible member recovers, FortiGate brings the interface back up.
This behavior allows downstream network equipment to detect a loss of WAN connectivity even when the local Ethernet link would otherwise remain operational.
Option A is incorrect because the configuration does not specify sending notification messages through port5 whenever an individual member fails.
Option C reverses the expected behavior. Port5 is brought down, not up, when all monitored SD-WAN members fail.
Option D is incorrect because fail-alert-interfaces controls interface state rather than functioning as a dedicated notification transport.
The cascade interface mechanism is particularly useful when an alternative network device must assume traffic forwarding following a complete SD-WAN connectivity failure.
[References: FortiOS 7.6 Administration Guide — Link Monitoring and Cascade Interfaces; Fortinet Knowledge Base — SD-WAN Failure Detection and Administratively Down Interfaces., ==========, ]