Halloween Sale Special Limited Time 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: CFsave75

Pass the Fortinet NSE 7 Network Security Architect NSE7_SSE_AR-26 Questions and answers with CertsForce

Viewing page 2 out of 4 pages
Viewing questions 11-20 out of questions
Questions # 11:

Which component, typically categorized under network edge connectivity rather than cloud-delivered security controls, is incorporated as a foundational element within a secure access service edge (SASE) architecture but is not considered part of a security service edge (SSE) framework?

Options:

A.

Secure web gateway (SWG)


B.

Software-Defined WAN (SD-WAN)


C.

Zero trust network access (ZTNA)


D.

Cloud access security broker (CASB)


Expert Solution
Questions # 12:

Refer to the exhibit. An administrator is troubleshooting SD-WAN on FortiGate. A device behind branch1_fgt generates traffic to the 10.0.0.0/8 network. The administrator expects the traffic to match SD-WAN rule ID 1 and be routed over HUB1-VPN1. However, the traffic is routed over HUB1-VPN3. Based on the output shown in the exhibit, which two reasons, individually or together, could explain the observed behavior? (Choose two.)
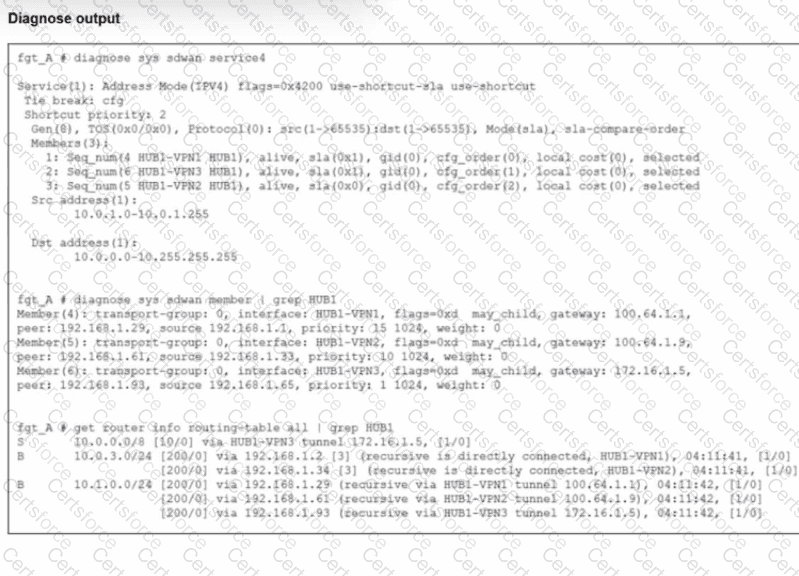
Question # 12

Exhibit 1

Options:

A.

HUB1-VPN3 has a higher member configuration priority than HUB1-VPN1.


B.

The traffic matches a regular policy route configured with HUB1-VPN3 as the outgoing device


C.

HUB1-VPN1 does not have a valid route to the destination


D.

HUB1-VPN3 has a lower route priority value (higher priority) than HUB1-VPN1.


Expert Solution
Questions # 13:

Refer to the exhibit.

Two hub-and-spoke groups are connected through redundant site-to-site IPsec VPNs between Hub 1 and Hub 2.

Which two configuration settings are required for spoke A1 to establish an auto-discovery VPN (ADVPN) shortcut with spoke B2? (Choose two.)
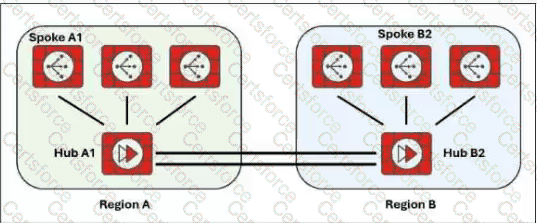
Question # 13

Exhibit — Hub-and-spoke ADVPN topology

Options:

A.

On the spokes, auto-discovery-receiver must be enabled on the IPsec VPNs to the hub.


B.

On the spokes, auto-discovery-sender must be enabled on the IPsec VPNs to hubs.


C.

On the hubs, auto-discovery-receiver must be enabled on the IPsec VPNs to spokes.


D.

On the hubs, auto-discovery-forwarder must be enabled on the IPsec VPNs to hubs.


Expert Solution
Questions # 14:

Refer to the exhibit. For your ZTP deployment, you review the CSV file shown in exhibit and note that it is missing important information. Which two elements must you change before you can import it into FortiManager? (Choose two.)
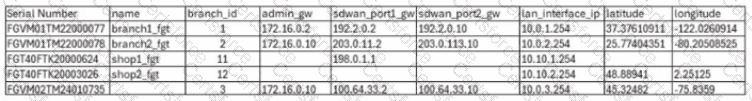
Question # 14

Exhibit 1

Options:

A.

You must associate a device blueprint with each device


B.

You must define a name for each device


C.

You must define a value for each device and each metadata variable that defines an IP address.


D.

You must define a value for each device and each user-defined metadata variable.


Expert Solution
Questions # 15:

When configuring FortiSASE BGP for SD-WAN private access with FortiSASE acting as the SD-WAN spoke, administrators must define specific settings.

What are some of the available configuration options?

Options:

A.

FortiSASE supports BGP per overlay or BGP on loopback with IBGP or EBGP peering.


B.

FortiSASE supports BGP per overlay, but not BGP on loopback with IBGP or EBGP peering.


C.

FortiSASE supports BGP per overlay or BGP on loopback with IBGP peering only.


D.

FortiSASE supports dynamic BGP, BGP per overlay, or BGP on loopback with IBGP or EBGP peering.


Expert Solution
Questions # 16:

Refer to the exhibit. The administrator analyzed the traffic between a branch FortiGate and the server located in the data center, and noticed the behavior shown in the diagram. When the LAN clients located behind FGT1 establish a session to a server behind DC-1, the administrator observes that, on DC-1, the reply traffic is routed overT2. even though T1 is the preferred member in the matching SD-WAN rule. What can the administrator do to instruct DC-1 to route the reply traffic through the member with the best performance?
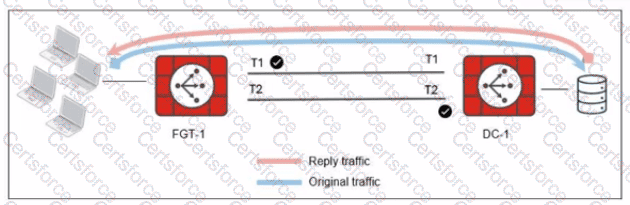
Question # 16

Exhibit 1

Options:

A.

Enable snat-route-change under config system global.


B.

Enable reply-session under config system sdwan.


C.

Enable auxiliary-session under config system settings.


D.

FortiGate route lookup for reply traffic only considers routes over the original ingress interface.


Expert Solution
Questions # 17:

An administrator is attempting to create two static routes: one for the SD-WAN zone wan-link and one pointing to a specific SD-WAN member interface that currently belongs to the wan-link zone.

Which configuration is required to make this scenario valid? (Choose one answer.)

Options:

A.

The destination subnets of the two static routes must be different.


B.

Both routes must have the same administrative distance to allow equal-cost multipath (ECMP).


C.

The destination subnet configured on the SD-WAN zone cannot be a default route.


D.

SD-WAN member must be an IPsec interface.


Expert Solution
Questions # 18:

Refer to the exhibit. The administrator configured two SD-WAN rules to load balance the traffic. Which interfaces does FortiGate use to steer the traffic from 10.0.1.124 to 10.0.0.254? Choose one answer.
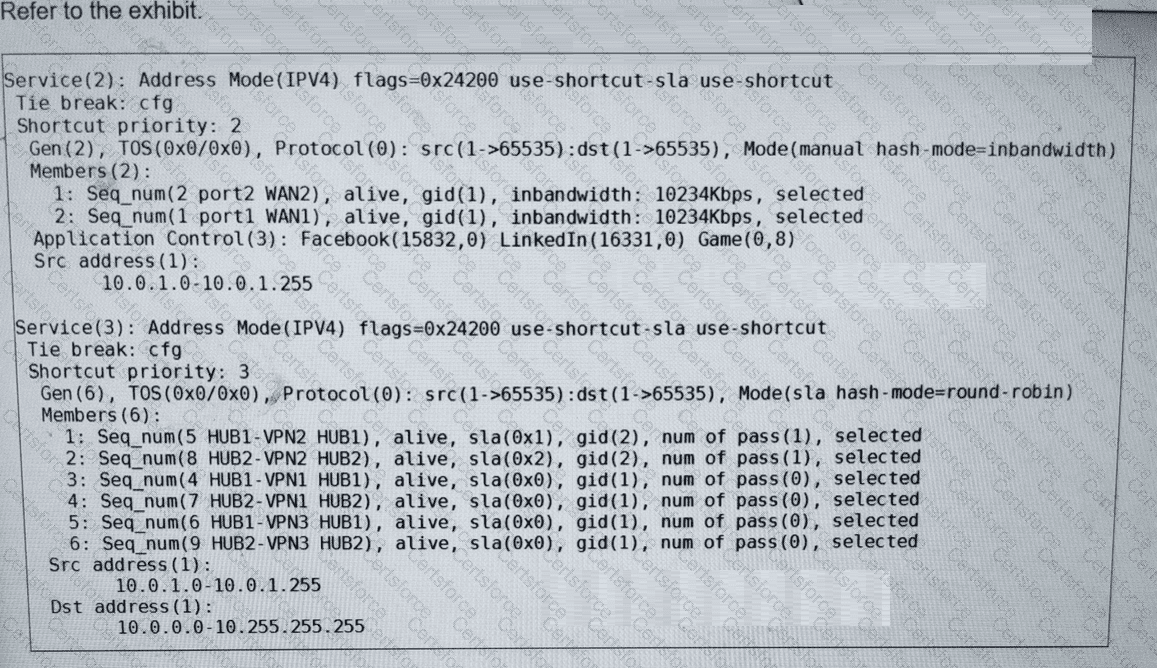
Question # 18

Exhibit 1

Options:

A.

HUB2-VPN2


B.

HUB1-VPN2 or HUB2-VPN2


C.

port1 or port2


D.

Any interface in the HUB1 or HUB2 zones


Expert Solution
Questions # 19:

Refer to the exhibit. How does FortiGate handle the traffic with the source IP 10.0.1.130 and the destination IP 128.66.0 125?
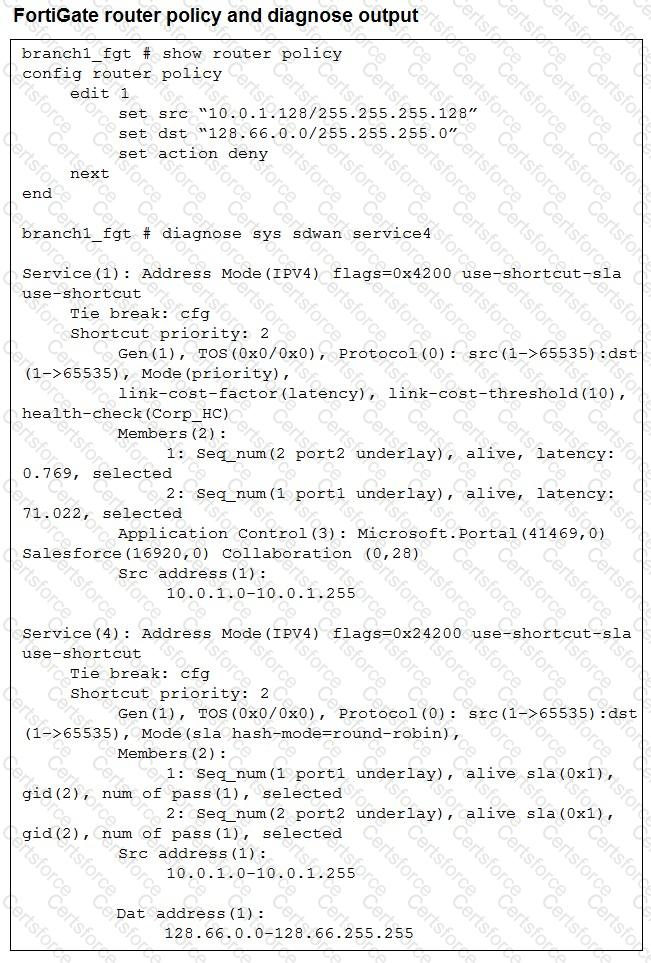
Question # 19

Exhibit 1

Options:

A.

FortiGate drops the traffic flow.


B.

FortiGate routes the traffic flow according to the forwarding information base (FIB).


C.

FortiGate load balances the traffic flow through port7 and port8.


D.

FortiGate steers the traffic flow through port7.


Expert Solution
Questions # 20:

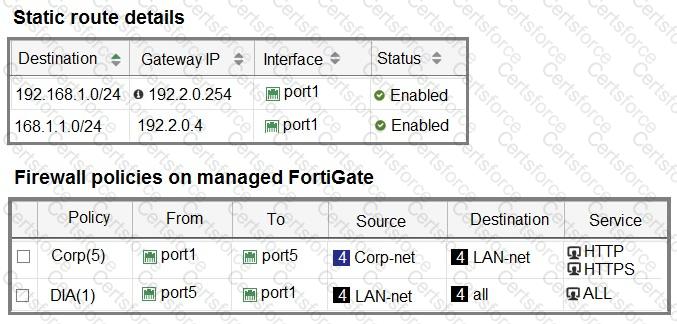
Refer to the exhibits. The interface details, static route configuration, and firewall policies on the managed FortiGate device are shown. You want to configure a new SD-WAN zone, named Underlay, that contains the interfaces port1 and port2. What must be your first action?
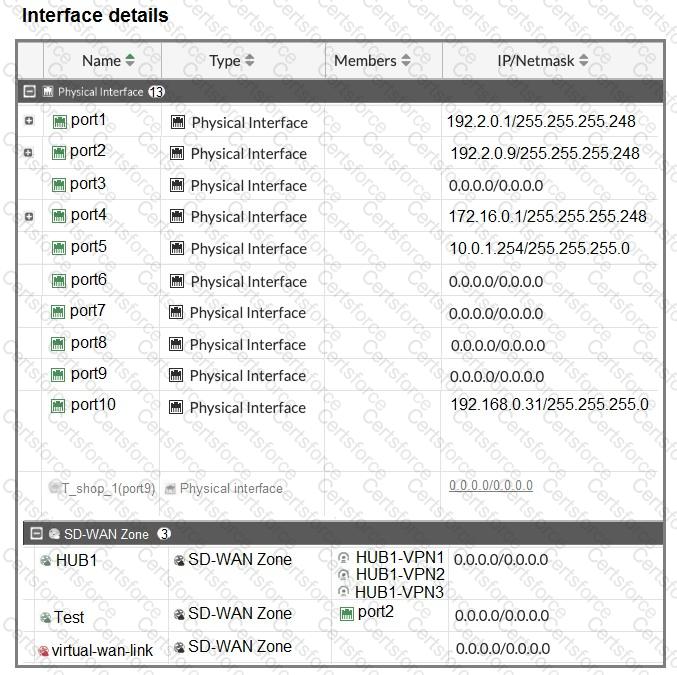
Question # 20

Exhibit 1

Question # 20

Exhibit 2

Options:

A.

Define port1 as an SD-WAN member.


B.

Delete the static routes.


C.

Delete the SD-WAN Zone Test.


D.

Delete the firewall policies.


Expert Solution
Viewing page 2 out of 4 pages
Viewing questions 11-20 out of questions