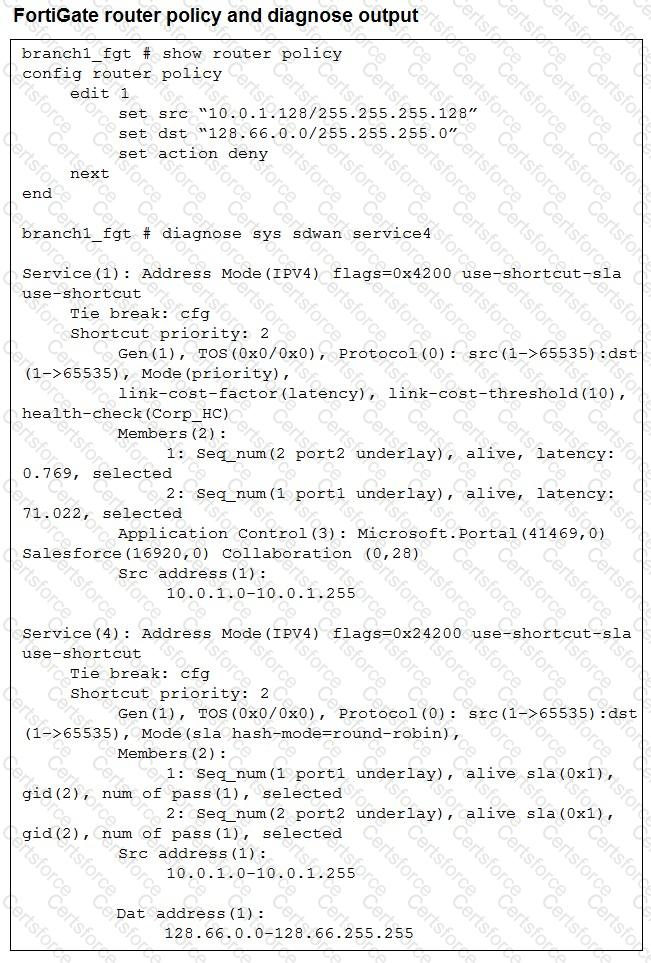
The matching router policy uses set action deny, which is not equivalent to a firewall security-policy deny. Within config router policy, the deny action stops policy-route processing and returns the packet to normal forwarding-information-base route evaluation. Both source 10.0.1.130 and destination 128.66.0.125 match the configured policy-route ranges. FortiGate therefore uses the FIB to select forwarding, subject to a valid route and an accepting firewall policy. The candidate answer key incorrectly claims SD-WAN load balancing, and its explanation incorrectly claims the traffic is dropped. Both contradict FortiOS policy-route semantics. Reference: FortiOS 7.6 CLI Reference — config router policy, action deny; Fortinet Technical Tip — Stop Policy Route. An operational review should distinguish the rule that matches the traffic from the interface that is ultimately selected. Valid forwarding also depends on destination route eligibility, current member state and the applicable SLA or quality-selection algorithm. A diagnostic showing configured members alone is not conclusive evidence that all those members will carry a particular flow.
Chosen Answer:
This is a voting comment (?). You can switch to a simple comment. It is better to Upvote an existing comment if you don't have anything to add.


Submit