Weekend Sale Special Limited Time 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: CFsave75

Pass the Fortinet Fortinet Network Security Expert NSE5_FSW_AD-7.6 Questions and answers with CertsForce

Viewing page 3 out of 4 pages
Viewing questions 21-30 out of questions
Questions # 21:

What are two ways in which automatic MAC address quarantine works on FortiSwitch? (Choose two.)

Options:

A.

FortiSwitch supports only by VLAN quarantine mode.


B.

FortiGate applies the quarantine-related configuration only on FortiGate.


C.

FortiAnalyzer with a threat detection services license is required.


D.

MAC address quarantine can be enabled through the FortiGate CLI only.


Expert Solution
Questions # 22:

Which two are valid traffic processing actions that a FortiSwitch access control list (ACL) can apply to matching traffic? (Choose two answers)

Options:

A.

Redirect frames to another port.


B.

Assign traffic to a high-priority egress queue.


C.

Encrypt frames.


D.

Drop frames.


Expert Solution
Questions # 23:

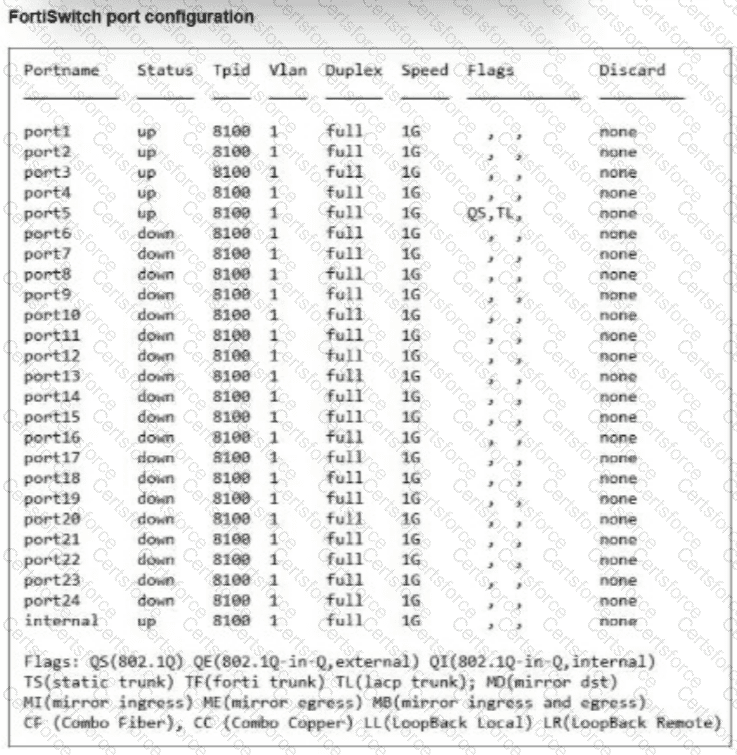
Refer to the exhibit.

Question # 23

You run the command diagnose switch physical-ports summary on FortiSwitch.

Based on exhibit, what does the output indicate to about the FortiSwitch mode? (Choose one answer)

Options:

A.

FortiSwitch is configured as access ports.


B.

FortiSwitch is configured as a layer 3 router.


C.

FortiSwitch is in standalone mode.


D.

FortiSwitch is operating in managed mode.


Expert Solution
Questions # 24:

You are configuring FortiSwitch to perform layer 3 inter-VLAN routing while managed by FortiGate over FortiLink. On supported hardware models, FortiSwitch can offload routing decisions for better performance.1How does FortiSwitch perform routing between VLANs? (Choose one answer)

Options:

A.

By using a hardware forwarding table (FIB) programmed into ASIC.


B.

By supporting only dynamic routing protocols in hardware.


C.

By disabling routing when managed by FortiGate.


D.

By relying entirely on the CPU in software.


Expert Solution
Questions # 25:

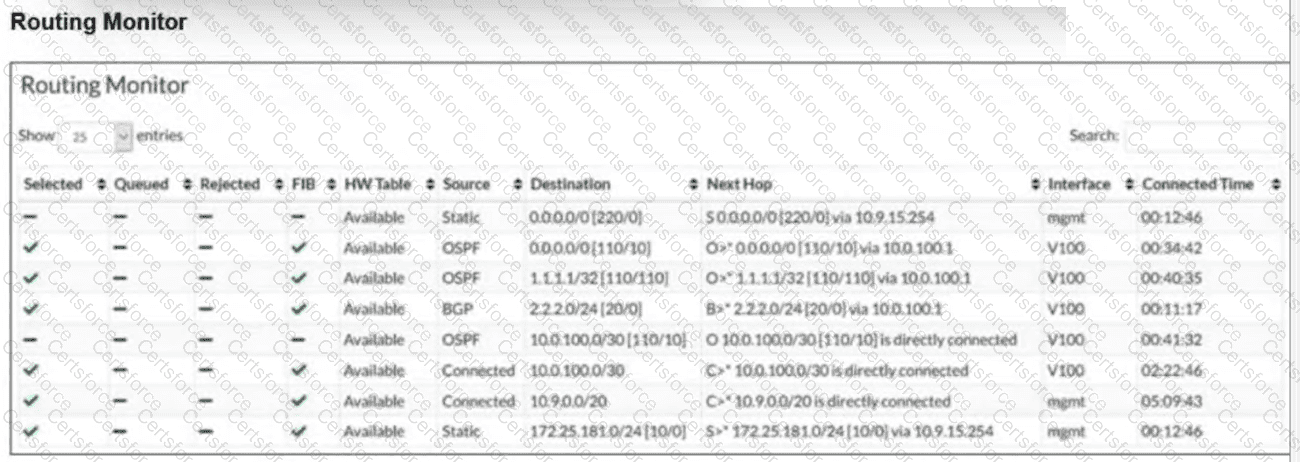
Refer to the exhibit.

Question # 25

and an OSPF route with destination 0.0.0.0/0 [110/10]. The OSPF route is marked with a checkmark in the FIB column, while the Static route has a dash.]

The routing monitor displays multiple route entries, but only some are installed in the forwarding information base (FIB). After analyzing the two route entries with the destination 0.0.0.0/0, which statement correctly describe why one of these routes is not installed in the FIB? (Choose one answer)

Options:

A.

The OSPF route has a higher metric, making it less preferred than the static route.


B.

The interface V100 for the OSPF route is down, preventing its installation.


C.

The OSPF route with a lower administrative distance is preferred over the static route.


D.

The two routes have identical destination prefixes, causing a conflict where only one is selected.


Expert Solution
Questions # 26:

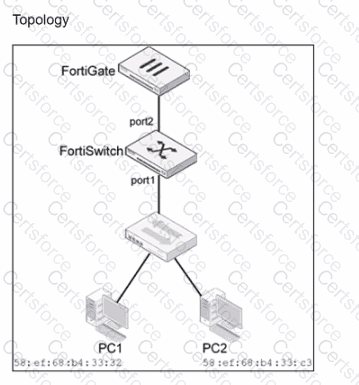
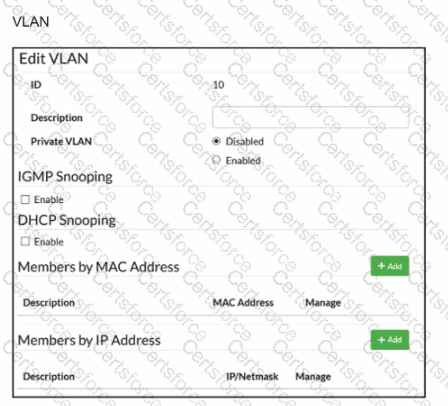
Refer to the exhibits

Question # 26

Question # 26

Traffic arriving on port2 on FortiSwitch is tagged with VLAN ID 10 and destined for PC1 connected on port1. PC1 expects to receive traffic untagged from port1 on FortiSwitch. Which two configurations can you perform on FortiSwitch to ensure PC1 receives untagged traffic on port1? (Choose two.)

Options:

A.

Add the MAC address of PC1 as a member of VLAN 10.


B.

Add VLAN ID 10 as a member of the untagged VLANs on port1.


C.

Remove VLAN 10 from the allowed VLANs and add it to untagged VLANs on port1.


D.

Enable Private VLAN on VLAN 10 and add VLAN 20 as an isolated VLAN.


Expert Solution
Questions # 27:

To enhance service in emergency situations, to which LLDP-MED Type-Length-Values does Forti-Switch advertise to IP phones?

Options:

A.

Network policy


B.

Inventory management


C.

Location


D.

Power management


Expert Solution
Questions # 28:

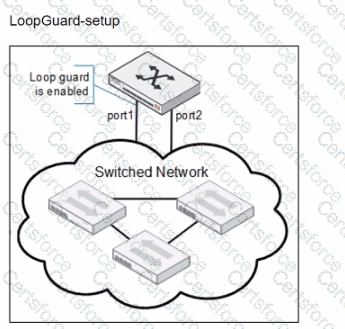
Refer to the exhibits.

Question # 28

Port1 and port2 are the only ports configured with the same native VLAN 10.

What are two reasons that can trigger port1 to shut down? (Choose two.)

Options:

A.

port1 was shut down by loop guard protection.


B.

STP triggered a loop and applied loop guard protection on port1.


C.

An endpoint sent a BPDU on port1 that it received from another interface.


D.

Loop guard frame sourced from port 1 was received on port 1.


Expert Solution
Questions # 29:

(Full question statement start from here)

How does FortiSwitch determine the route for traffic traversing its interfaces? (Choose one answer)

Options:

A.

Hardware-based routing on FortiSwitch is handled by the CPU.


B.

ASIC hardware routing can handle only dynamic routing, if supported.


C.

FortiSwitch looks up the hardware routing table and then the forwarding information base (FIB).


D.

FortiSwitch forwards all traffic to FortiGate for routing decisions.


Expert Solution
Questions # 30:

Which statement about using MAC, IP, and protocol-based VLANs on FortiSwitch is true?

Options:

A.

lt is a scalable and secure solution in comparison to other Layer 2 security measures.


B.

FortiSwitch uses only the Ethernet type to assign traffic to VLANs.


C.

It provides benefits that can be obtained when using 802.1X authentication.


D.

Endpoints are required to use the same FortiSwitch port to remain members of the VLAN.


Expert Solution
Viewing page 3 out of 4 pages
Viewing questions 21-30 out of questions