Weekend Sale Special Limited Time 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: CFsave75

Pass the Fortinet Fortinet Network Security Expert NSE5_FSW_AD-7.6 Questions and answers with CertsForce

Viewing page 2 out of 4 pages
Viewing questions 11-20 out of questions
Questions # 11:

What can an administrator do to maintain the existing standalone FortlSwltch configuration while changing the management mode to FortLink?

Options:

A.

Use a migration tool based on python script to convert the configuration


B.

Enable the Forti-link setting on FortiSwitch before the authorization process


C.

FortiGate will automatically save the existing FortiSwitch configuration during the Forti-link management process.


D.

Register FortiSwitch to For1ISwitch Cloud to save a copy before managing by Forti-Gate.


Expert Solution
Questions # 12:

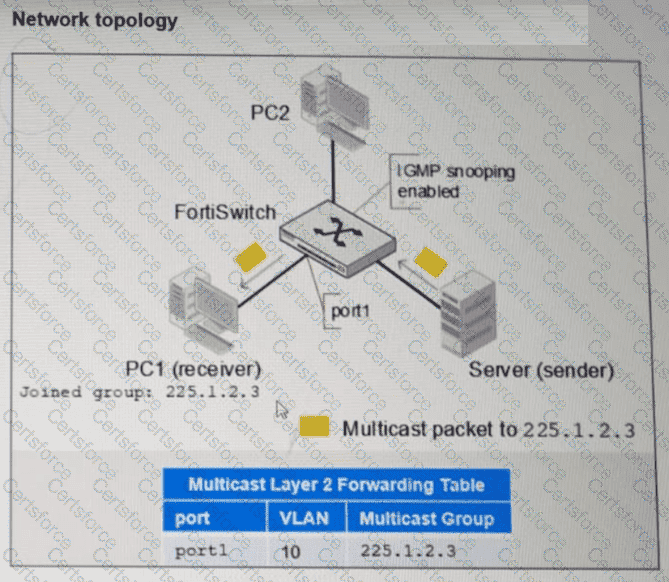
Refer to the exhibit.

Question # 12

PC1 connected to port1 has joined multicast group 225.1.2.3 on VLAN 10 with IGMP snooping enabled. What will happen if you disable IGMP snooping on FortiSwitch? (Choose one answer)

Options:

A.

PC1 will be removed from the multicast group 225.1.2.3.


B.

The FortiSwitch will stop processing IGMP report join messages.


C.

Multicast traffic for 225.1.2.3 will be flooded to all ports.


D.

Multicast traffic will stop until a multicast receiver is detected.


Expert Solution
Questions # 13:

You are deploying a multitier FortiSwitch topology with redundant links between access and aggregation switches. The team is considering Multiple Spanning Tree Protocol (MSTP) to manage spanning tree across multiple VLANs. Which two Rapid STP (RSTP) features would be useful in this deployment to ensure fast convergence and predictable port roles? (Choose two answers)

Options:

A.

The process for selecting the root bridge


B.

Recalculating paths after a topology change


C.

Automatic VLAN assignment


D.

The rules for determining port roles


Expert Solution
Questions # 14:

Which statement about the quarantine VLAN on FortiSwitch is true?

Options:

A.

Quarantine VLAN has no DHCP server


B.

Users who fail 802.1X authentication can be placed on the quarantine VLAN.


C.

It is only used for quarantined devices if global setting is set to quarantine by VLAN.


D.

FortiSwitch can block devices without configuring quarantine VLAN to be part of the allowed VLANs.


Expert Solution
Questions # 15:

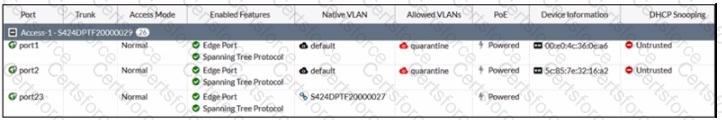
Refer to the exhibit.

Question # 15

The exhibit shows the current status of the ports on the managed FortiSwitch. Access-1.

Why would FortiGate display a serial number in the Native VLAN column associated with the port23 entry?

Options:

A.

port23 is configured as the dedicated management interface.


B.

Ports connected to adjacent FortiSwitch devices show their serial number as the native VLAN.


C.

port23 is a member of a trunk that uses the Access-1 FortiSwitch serial number as the name of the trunk.


D.

A standalone switch with the shown serial number is connected on port23.


Expert Solution
Questions # 16:

(Full question statement start from here)

A FortiGate is connected to a pair of FortiSwitch devices.

For redundancy, FortiGate must use uplinks on both switches simultaneouslywithout depending on Spanning Tree Protocol (STP).

Which configuration is required? (Choose one answer)

Options:

A.

Multi-tier topology


B.

Multichassis link aggregation group (MCLAG)


C.

Full mesh high availability (HA)


D.

Link aggregation group (LAG)


Expert Solution
Questions # 17:

Which two statements about 802.1X authentication on FortiSwitch ports are true? (Choose two.)

Options:

A.

All hosts behind an authenticated port are allowed access after a successful authentication.


B.

A security policy is used to apply 802.1 authentication on a port.


C.

A local user database must be used to authenticate devices using the 802.1X authentication protocol.


D.

All devices connecting to FortiSwitch must support 802.1X authentication.


Expert Solution
Questions # 18:

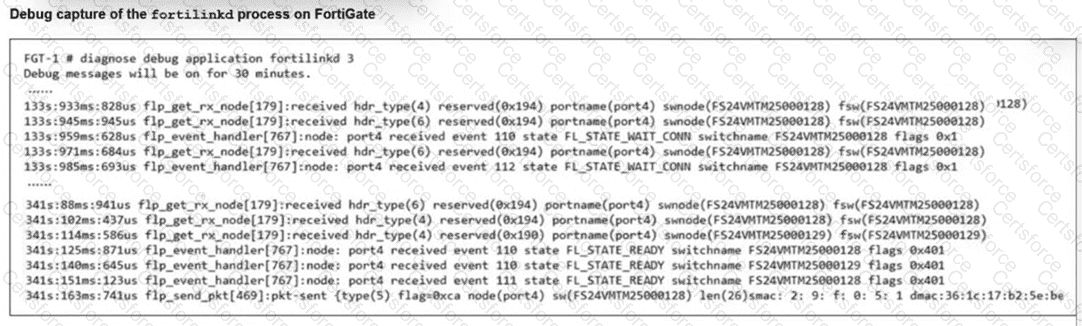
Refer to the exhibit.

Question # 18

A periodic heartbeat message sent from a managed FortiSwitch and corresponding acknowledgments from FortiGate is shown. What does this behavior indicate? (Choose one answer)

Options:

A.

The FortiLink connection between FortiGate and FortiSwitch is healthy and active.


B.

FortiGate is unable to establish a FortiLink session with FortiSwitch.


C.

FortiSwitch is expecting an authorization from FortiGate.


D.

FortiSwitch has not been authorized yet.


Expert Solution
Questions # 19:

Refer to the diagnostic output:

What makes the use of the sniffer command on the FortiSwitch CLI unreliable on__port__23?

Options:

A.

The types of packets captured is limited.


B.

Just the port egress payloads are printed on CLI.


C.

Only untagged VLAN traffic can be captured.


D.

The switch port might be used as a trunk member


Expert Solution
Questions # 20:

Which statement about the IGMP snooping querier when enabled on a VLAN is true?

Options:

A.

Active multicast receiver entries are aging on each IGMP query sent on the VLAN


B.

IGMP reports on the VLAN are forwarded to all switch ports.


C.

The setting can only be enabled using the FortiSwitch CLI.


D.

All other indirectly connected switches will be unable to get IGMP multicast traffic.


Expert Solution
Viewing page 2 out of 4 pages
Viewing questions 11-20 out of questions