Weekend Sale Special Limited Time 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: CFsave75

Pass the Fortinet Fortinet Network Security Expert NSE5_FSW_AD-7.6 Questions and answers with CertsForce

Viewing page 1 out of 4 pages
Viewing questions 1-10 out of questions
Questions # 1:

In which two ways can you assign a FortiSwitch port to a VDOM using a multi-tenancy setup? (Choose two answers)

Options:

A.

Assign the switch port to a VLAN on FortiGate and perform VDOM mapping.


B.

Create a virtual port pool on the FortiGate CLI.


C.

Assign a port to a VDOM directly on the managed FortiSwitch.


D.

Switch the FortiLink interface to the target VDOM.


Expert Solution
Questions # 2:

Exhibit.

LAG and MCLAG are used to increase the available network bandwidth and enable redundancy. How does spanning tree protocol see MCLAG and LAG if they are configured based on the physi-cal view shown in the exhibit? (Choose two)

Options:

A.

Switch 1. Switch 2, and Switch 3 are seen as one MCLAG peer group


B.

Switch 3 and Switch 4 uplinks are treated as single interfaces.


C.

Switch 3 and switch 4 are seen as one MCLAG switch client


D.

Switch 1 and Switch 2 both seen as one single switch.


Expert Solution
Questions # 3:

Which QoS mechanism maps packets with specific CoS or DSCP markings to an egress queue?

Options:

A.

Queuing for egress traffic


B.

Classification for ingress traffic


C.

Rate limiting for egress traffic


D.

Marking for ingress traffic


Expert Solution
Questions # 4:

On supported FortiSwitch models, which access control list (ACL) stage is recommended for applying actions before the switch performs any layer 2 or layer 3 processing? (Choose one answer)

Options:

A.

Ingress


B.

Forwarding


C.

Egress


D.

Prelookup


Expert Solution
Questions # 5:

In which two ways can you assign a FortiSwitch port to a VDOM using multi-tenancy setup? (Choose two.)

Options:

A.

Switch the FortiLink interface to the target VDOM.


B.

Remove the managed FortiSwitch and allocate ports directly on FortiSwitch.


C.

Create a virtual port pool on the FortiGate CLI.


D.

Assign a port to a VDOM directly on the managed FortiSwitch.


Expert Solution
Questions # 6:

(Full question statement start from here)

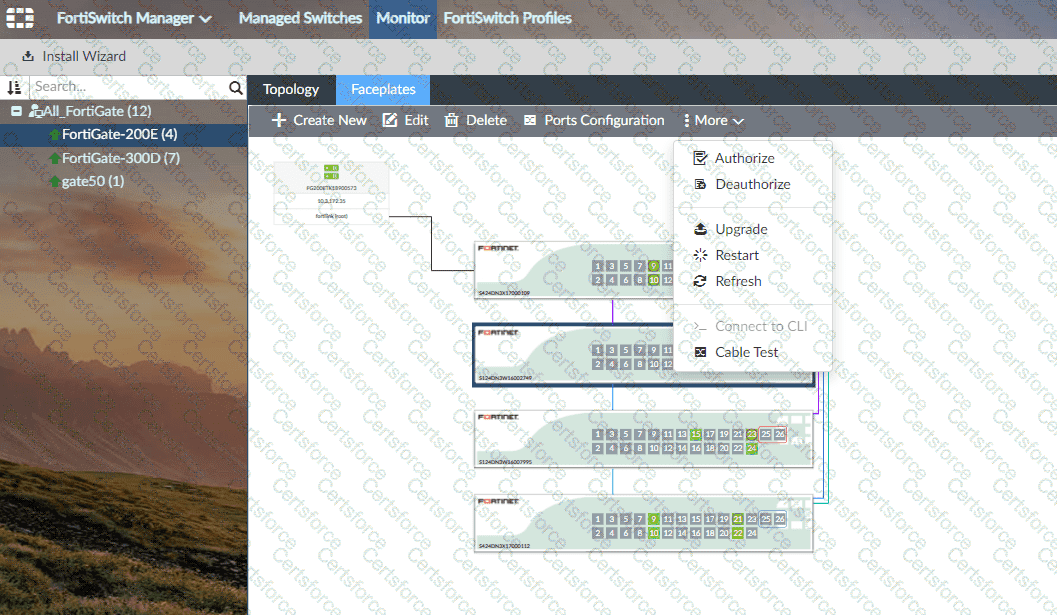
Refer to the exhibit.
Question # 6

Question # 6

Question # 6

Which information does FortiGate use to generate the port details in the FortiSwitch Faceplates view? (Choose one answer)

Options:

A.

The FortiSwitch model


B.

The Cisco Discovery Protocol (CDP) advertisements from FortiSwitch


C.

The LLDP advertisements received from the FortiSwitch


D.

The FortiLink discovery frames sent by FortiSwitch


Expert Solution
Questions # 7:

Which drop policy mode, if assigned to a congested port, will drop incoming packets until there is no congestion on the egress port?

Options:

A.

Tail-drop mode


B.

Weighted round robin mode.


C.

Random early detection mode


D.

Strict mode


Expert Solution
Questions # 8:

Which two statements about VLAN assignments on FortiSwitch ports are true? (Choose two.)

Options:

A.

Configure a native VLAN on the FortiLink


B.

Assign an IP address and subnet mask to FortiSwitch VLANs


C.

Only assign one native VLAN on a port


D.

Assign untagged VLANs using FortiGate CLI


Expert Solution
Questions # 9:

An administrator must deploy managed FortiSwitch devices in a remote location where multiple VLANs must be used to segment devices. No layer 3 switch or router is present at the site, and the only WAN connectivity is an ISP-provided router connected to the public internet. Which two components are required to enable VLAN segmentation across this remote site? (Choose two answers)

Options:

A.

FortiGate and FortiSwitch configured with VXLAN to tunnel VLANs over the WAN


B.

A layer 3 router at the remote location to handle inter-VLAN routing


C.

A FortiSwitch model that supports VXLAN hardware acceleration


D.

FortiSwitch and FortiGate devices configured with IPsec interfaces


E.

FortiGate with a layer 3 interface to terminate the VXLAN overlay


Expert Solution
Questions # 10:

Which interfaces on FortiSwitch send out FortiLink discovery frames by default in order to detect a FortiGate with an enabled FortiLink interface?

Options:

A.

All ports have auto-discovery enabled by default.


B.

No ports are enabled by default for auto-discovery. This must be configured under config switch interface.


C.

The ports with auto-discovery enabled by default are dependent upon the FortiSwitch model.


D.

The last four switch ports on FortiSwitch have auto-discovery enabled by default.


Expert Solution
Viewing page 1 out of 4 pages
Viewing questions 1-10 out of questions