
A developer is working on a project that requires encrypting all data before sending it to a backend application. To accomplish this, the developer will use PGP encryption in the Mule 4 Cryptography module.
What is required to encrypt the data before sending it to the backend application?
A Mule application includes a subflow containing a Scatter-Gather scope. Within each leg of the Scatter-Gather, an HTTP connector calls a PUT endpoint to modify records in different upstream systems. The subflow is called from inside an Until Successful scope to retry if a transient exception is raised.
A technical spike is being performed to increase reliability of the Mule application.
Which steps should be performed within the Mule flow above to ensure idempotent behavior?
A Mule application uses API autodiscovery to access and enforce policies for a RESTful implementation.
What needs to be configured for the flowRef attribute of the autodiscovery global element?
A company with MuleSoft Titanium support develops a Salesforce System API using MuleSoft's out-of-the-box Salesforce Connector and deploys the API to CloudHub.
Which steps provide the average number of requests and average response time of the Salesforce Connector?
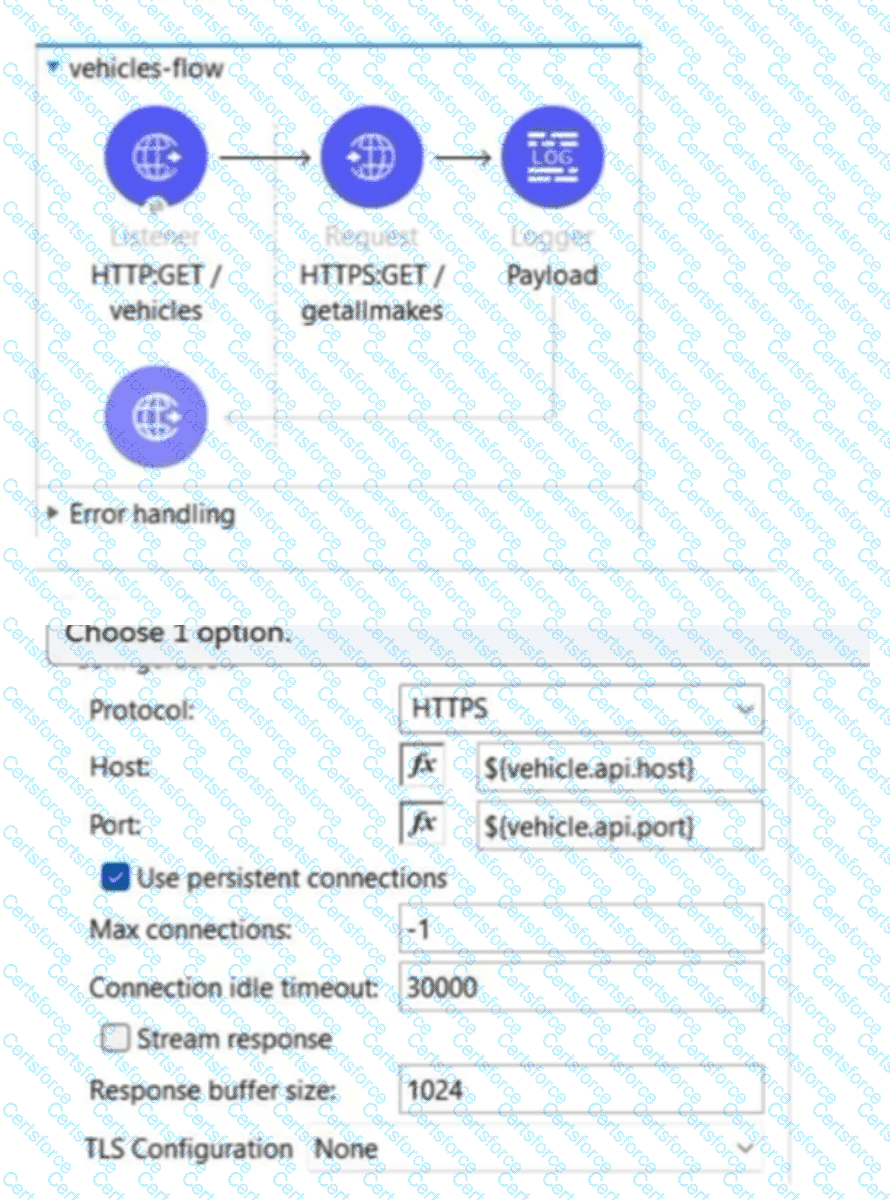
Refer to the exhibits.
The flow is invoking a target API. The API's protocol is HTTPS. The TLS configuration in the HTTP Request Configuration global element is set to None. A web client submits a request to http://localhost:8081/vehicles.
If the certificate of the target API is signed by a certificate authority (CA), what is true about the HTTP Request operation when the flow executes?
Exhibit:
A Mule application deployed to multiple CloudHub 2.0 replicas needs to temporarily persist large files over 10MB between flow executions, and routinely needs to query whether the file data exists on separate executions.
How can this be achieved?
When registering a client application with an existing API instance or API Group instance, what is required to manually approve or reject request access?
An API has been developed and deployed to CloudHub. Among the policies applied to this API is an allowlist of IP addresses. A developer wants to run a test in Anypoint Studio and does not want any policies applied because their workstation is not included in the allowlist.
What must the developer do in order to run this test locally without the policies applied?
