You need to meet the technical requirements for Server1. Which users can currently perform the required task?
You need to meet the technical requirements for the site links. Which users can perform the required task?
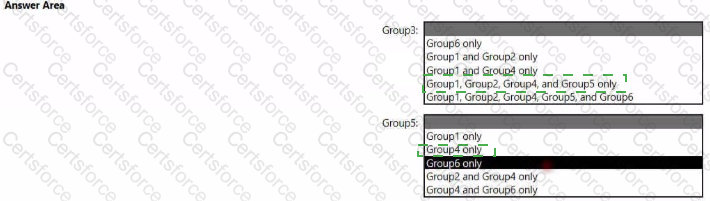
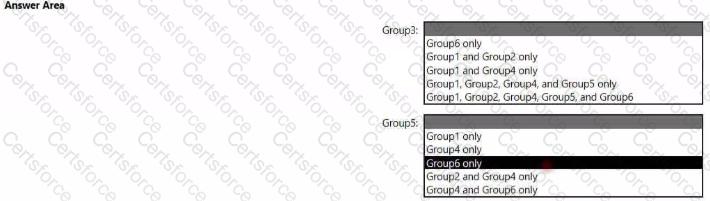
Which groups can you add to Group3, and which groups can you add to Group5? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You need to meet the technical requirements for User1. The solution must use the principle of least privilege. What should you do?
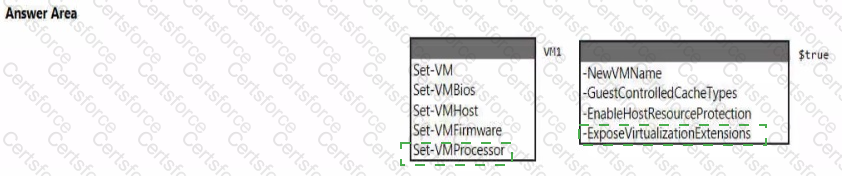
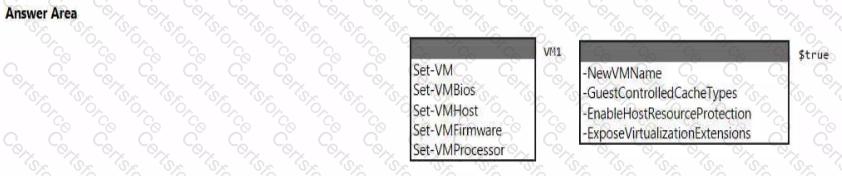
You need to meet the technical requirements for VM1. Which cmdlet should you run first? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You need to meet the technical requirements for Server3. Which users can perform the required task?
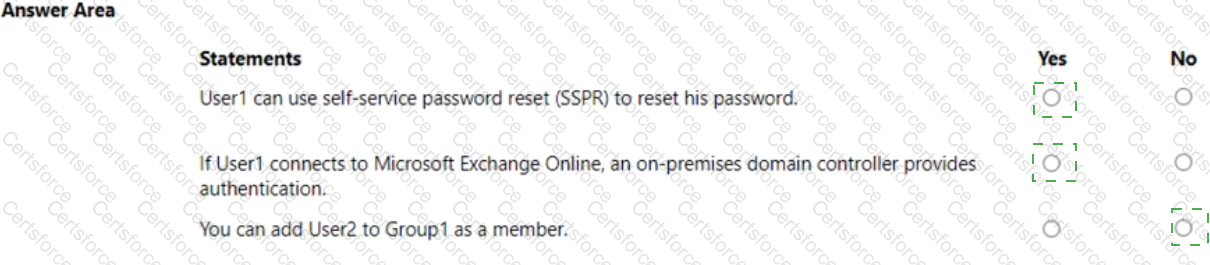
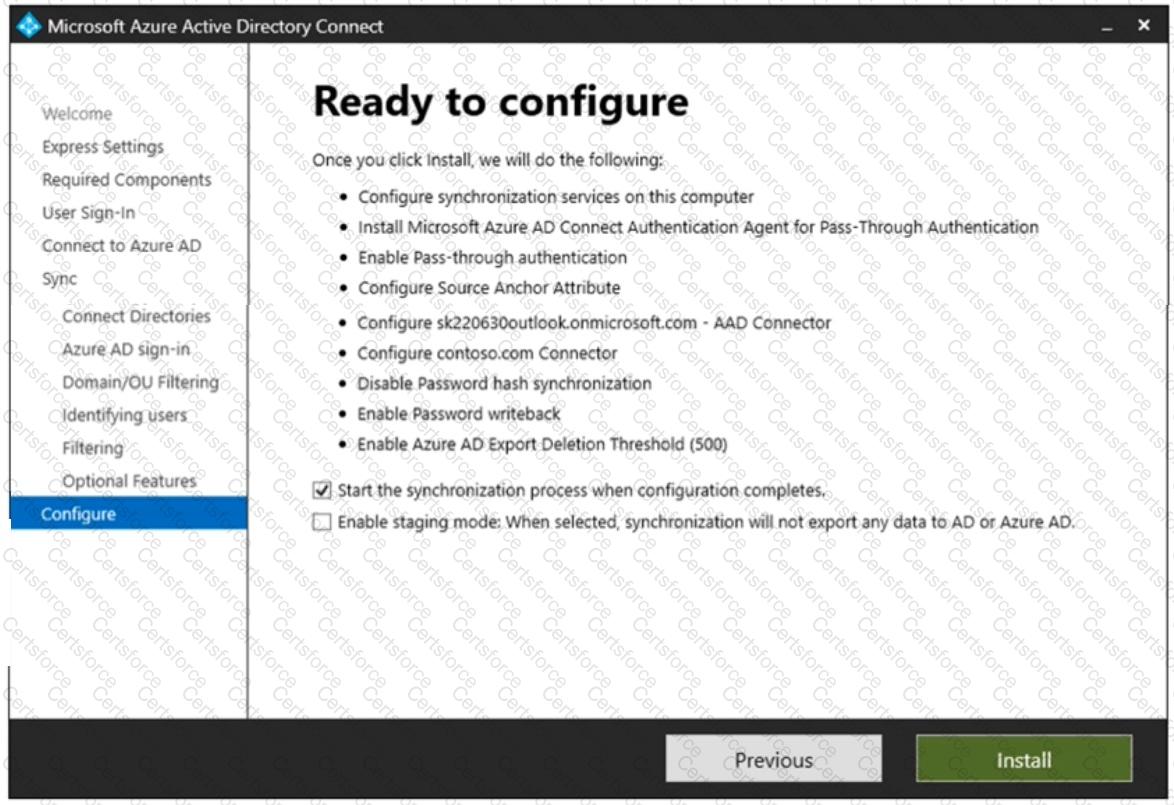
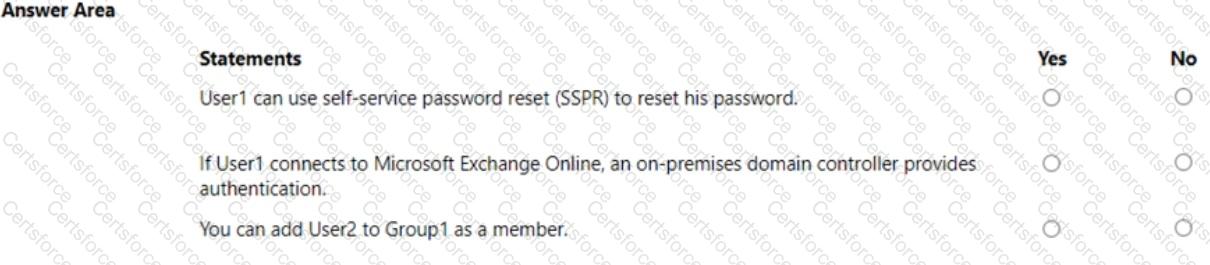
Your network contains an on-premises Active Directory Domain Services (AD DS) domain named contoso.com that syncs with a Microsoft Entra ID tenant. The tenant contains a group named Group1 and the users User1 (in OU1) and User2 (in OU2). Domain/OU filtering in Microsoft Entra Connect is configured to sync only OU1 and the Users container (OU2 is not selected). The Microsoft Entra Connect configuration shows: Pass-through authentication enabled; Password hash synchronization disabled; Password writeback enabled. For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.
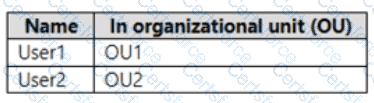
User1: OU1 (synced). User2: OU2 (not synced).
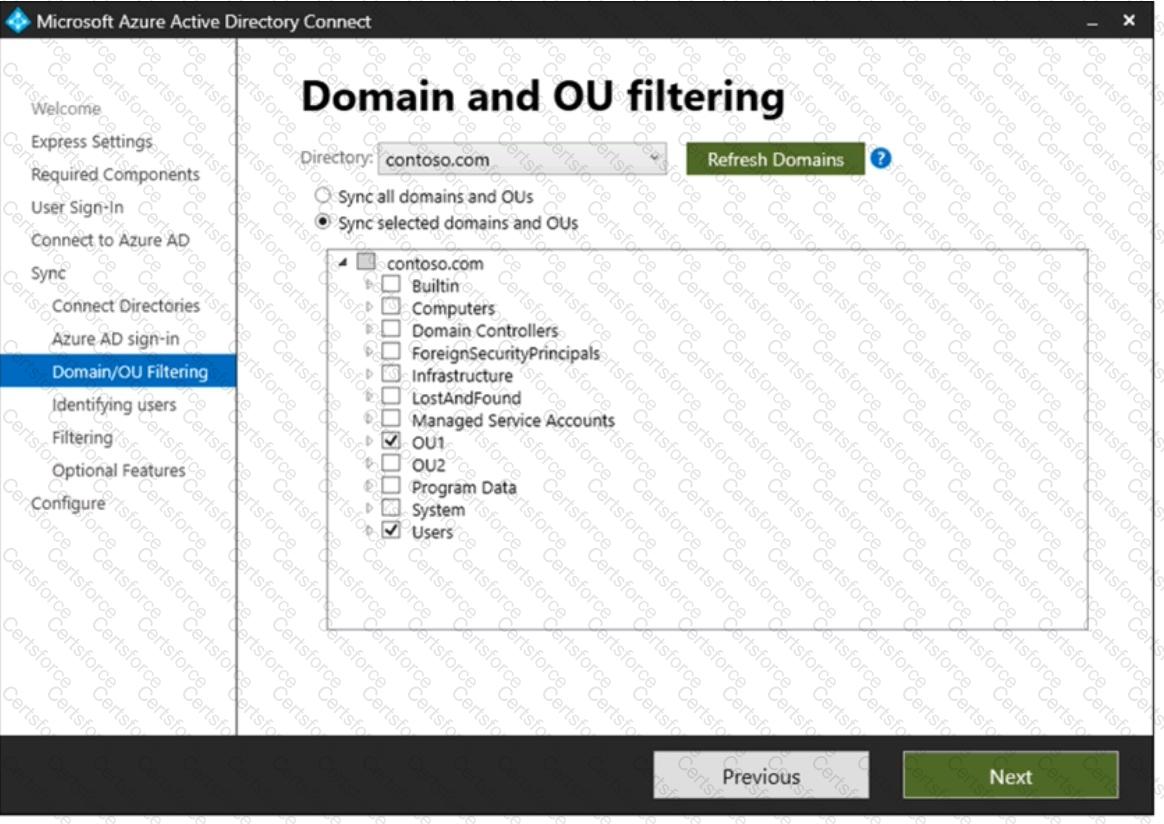
Domain/OU Filtering: ' Sync selected domains and OUs ' with OU1 and Users checked; OU2 unchecked.
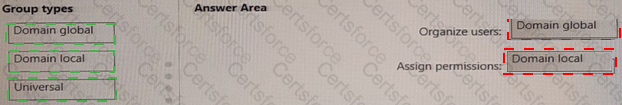
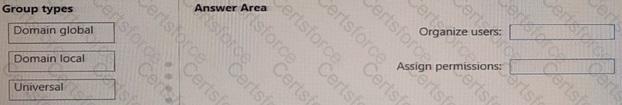
Your network contains two Active Directory Domain Services (AD DS) forests named contoso.com and fabrikam.com. Contoso.com contains three child domains named amer.contoso.com, apac.contoso.com, and emea.contoso.com. Fabrikam.com contains a child domain named apac.fabrikam.com. A bidirectional forest trust exists between contoso.com and fabrikam.com. You need to provide users in the contoso.com forest with access to the resources in the fabrikam.com forest. The solution must meet the following requirements: users in contoso.com must only be added directly to groups in the contoso.com forest; permissions to access the resources in fabrikam.com must only be granted directly to groups in the fabrikam.com forest; the number of groups must be minimized. Which type of groups should you use to organize the users and to assign permissions? To answer, drag the appropriate group types to the correct requirements. Each group type may be used once, more than once, or not at all.
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution. After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen. You have a server named Server1 that runs Windows Server. You need to ensure that only specific applications can modify the data in protected folders on Server1. Solution: From App & browser control, you configure Reputation-based protection. Does this meet the goal?
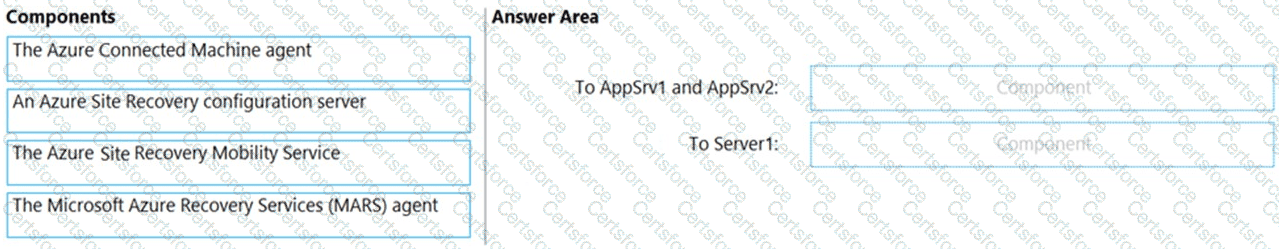
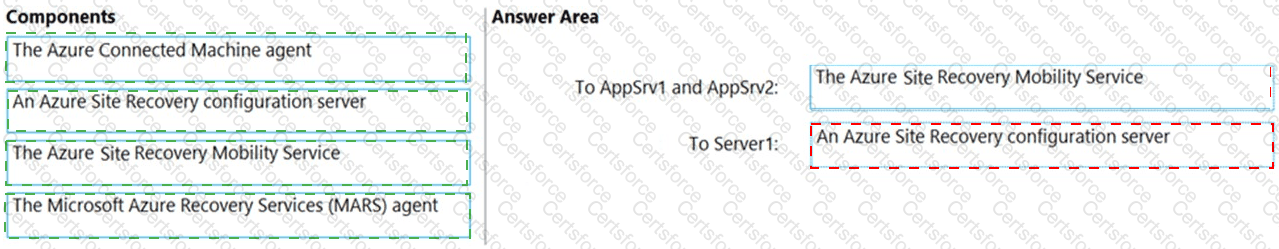
You have two physical servers named AppSrv1 and AppSrv2 and an unconfigured server named Server1. All the servers run Windows Server. Only Server1 can access the internet. You plan to use Azure Site Recovery to replicate AppSrv1 and AppSrv2 to Azure. You need to deploy the required components to AppSrv1, AppSrv2, and Server1. Which components should you deploy? To answer, drag the appropriate components to the correct servers. Each component may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content. NOTE: Each correct selection is worth one point.