Winter Sale Special Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: force70

Pass the Fortinet NSE 7 Network Security Architect NSE7_FSN_AR-7.6 Questions and answers with CertsForce

Viewing page 5 out of 6 pages
Viewing questions 41-50 out of questions
Questions # 41:

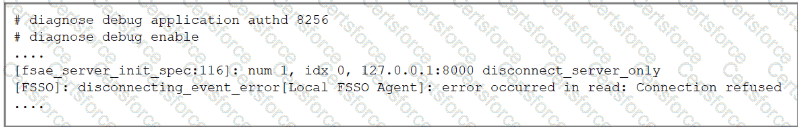
Refer to the exhibit showing a debug output.
Question # 41

An administrator deployed FSSO in DC Agent Mode but FSSO is failing on FortiGate. Pinging FortiGate from where the collector agent is deployed is successful.

The administrator then produces the debug output shown in the exhibit.

What could be causing this error message?

Options:

A.

The TCP port 445 is blocked between FortiGate and collector agent.


B.

The collector agent preshared password is mismatched.


C.

The FortiGate cannot resolve the active directory server name.


D.

The FortiGate and the collector agent are using different TCP ports.


Expert Solution
Questions # 42:

Refer to the exhibit.

Question # 42

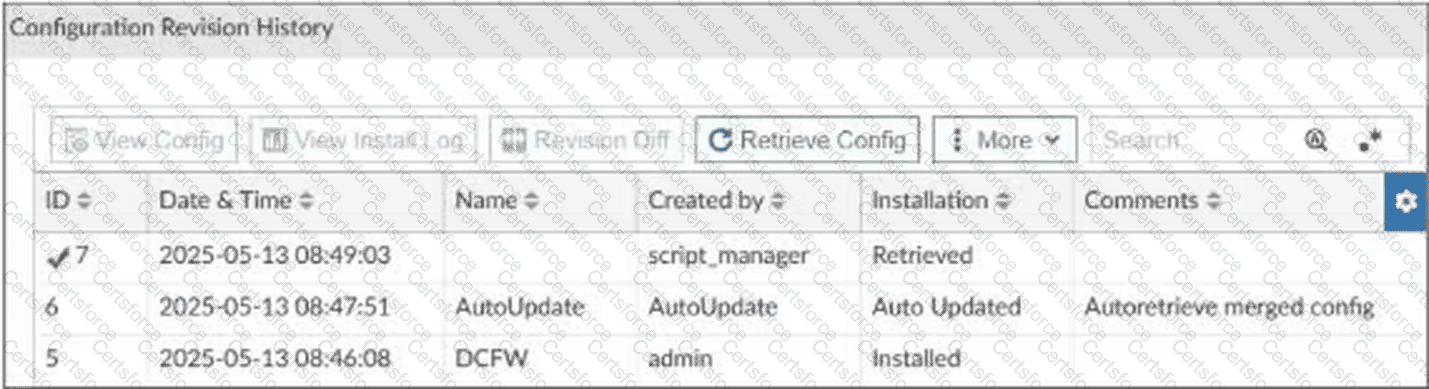
A revision history window at the FortiManager device layer is shown.

The IT team is trying to identify the administrator responsible for the most recent update to the FortiGate device database.

What can the IT team conclude?

Options:

A.

The retrieve process was automatically triggered by a Remote FortiGate Directly (via CLI) script.


B.

To identify the user who created the event, they must view it on the Configuration and Installation widget on FortiGate at the FortiManager device layer.


C.

To identify the user who created the event, in the FortiManager system logs, they must use the type=script filter in the user field.


D.

The user script_manager, an API user from the Fortinet Developer Network (FDN), is retrieving a configuration.


Expert Solution
Questions # 43:

Exhibit.

Question # 43

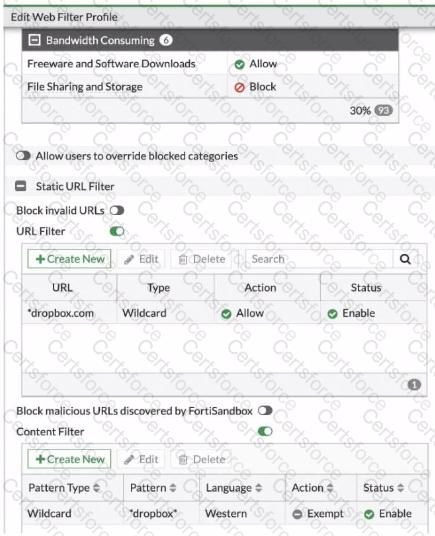
Refer to the exhibit, which shows a partial web fillet profile configuration.

Which action does FortiGate lake if a user attempts to access www. dropbox. com, which is categorized as File Sharing and Storage?

Options:

A.

FortiGate allows the connection, based on the URL Filter configuration.


B.

FortiGate blocks the connection as an invalid URL.


C.

FortiGate exempts the connection, based on the Web Content Filter configuration.


D.

FortiGate blocks the connection, based on the FortiGuard category based filter configuration.


Expert Solution
Questions # 44:

You must use FortiManager to standardize the deployment of the same FortiGate model across multiple branches with consistent interface roles and policy packages.

In this scenario, what is the recommended best practice for interface assignment?

Options:

A.

Create interfaces using CLI scripts and use those interfaces in FortiGate policy packages.


B.

Enable metadata variables to use dynamic configurations on the standard interfaces of FortiManager.


C.

Create normalized interface mappings per platform to automatically map device-level interfaces based on the FortiGate model and interface name.


D.

Use the Install On feature in the policy package to automatically assign the interfaces across branches.


Expert Solution
Questions # 45:

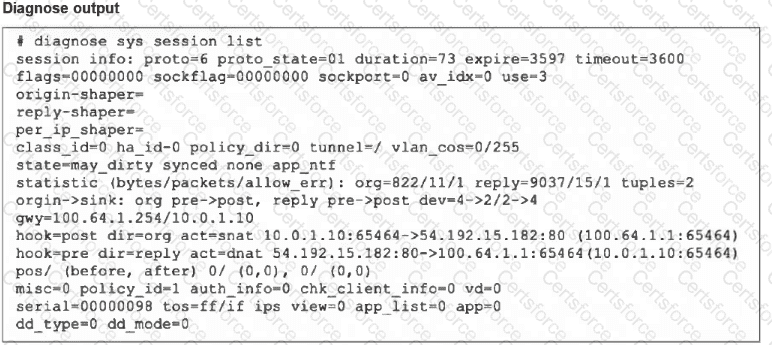
Refer to the exhibit, which shows the output of diagnose sys session list.
Question # 45

If the HA ID for the primary device is 0, what happens if the primary fails and the secondary becomes the primary?

Options:

A.

The secondary device has this session synchronized; however, because application control is applied, the session is marked dirty and has to be re-evaluated after failover.


B.

Traffic for this session continues to be permitted on the new primary device after failover, without requiring the client to restart the session with the server.


C.

The session will be removed from the session table of the secondary device because of the presence of allowed error packets, which will force the client to restart the session with the server.


D.

The session state is preserved but the kernel will need to re-evaluate the session because NAT was applied.


Expert Solution
Questions # 46:

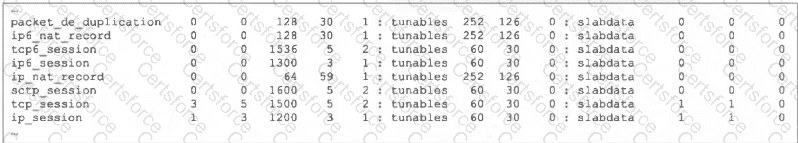
Refer to the exhibit, which shows the partial output of FortiOS kernel slabs.
Question # 46

Which statement is true?

Options:

A.

The total slab size of the sctp_session slab is 0 kB and is associated with the user space.


B.

The total slab size of the ip_session slab is 3600 kB and is associated with the user space.


C.

The total slab size of the ip6_session slab is 1300 kB and is associated with the kernel.


D.

The total slab size of the tcp_session slab is 7500 kB and is associated with the kernel.


Expert Solution
Questions # 47:

Which two statements about conserve mode are true? (Choose two.)

Options:

A.

FortiGate enters conserve mode when the system memory reaches the configured extreme threshold.


B.

FortiGate starts taking the configured action for new sessions requiring content inspection when the system memory reaches the configured red threshold.


C.

FortiGate exits conserve mode when the system memory goes below the configured green threshold.


D.

FortiGate starts dropping all new sessions when the system memory reaches the configured red threshold.


Expert Solution
Questions # 48:

Exhibit.

Question # 48

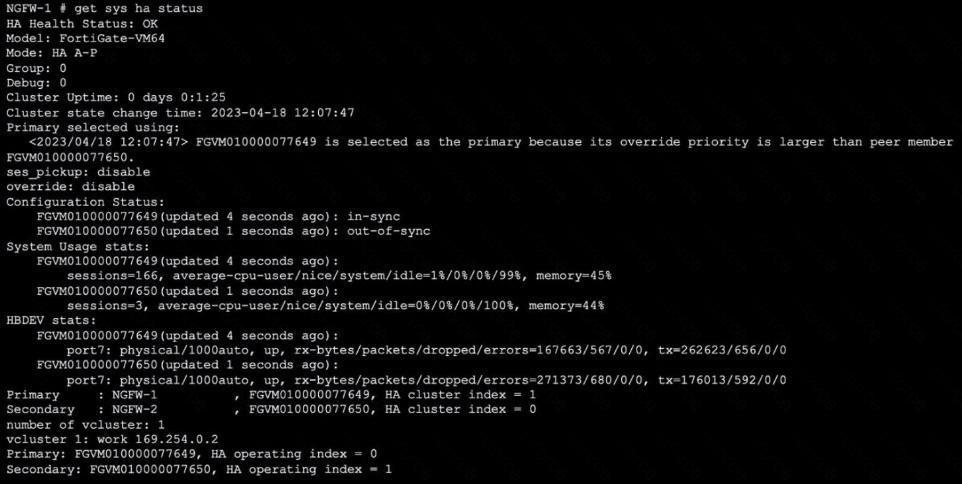
Refer to the exhibit, which shows the output of get system ha status.

NGFW-1 and NGFW-2 have been up for a week.

Which two statements about the output are true? (Choose two.)

Options:

A.

If a configuration change is made to the primary FortiGate at this time, the secondary will initiate a synchronization reset.


B.

If port 7 becomes disconnected on the secondary, both FortiGate devices will elect itself as primary.


C.

If FGVM...649 is rebooted. FGVM...650 will become the primary and retain that role, even after FGVM...649 rejoins the cluster.


D.

If no action is taken, the primary FortiGate will leave the cluster because of the current sync status.


Expert Solution
Questions # 49:

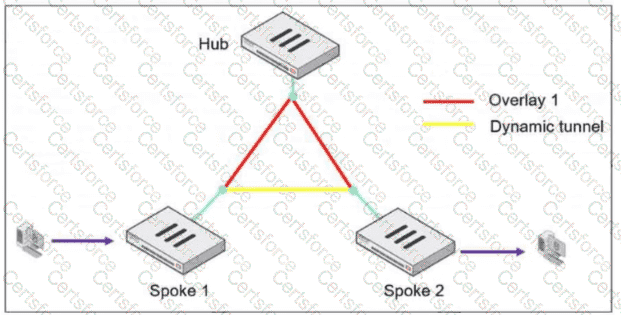
Refer to the exhibit.

Question # 49

Based on the exhibit, what is the first message with which Spoke 1 replies to the hub, instructing it to bring up the dynamic tunnel when a client generates traffic destined for Spoke 2? (Choose one answer.)

Options:

A.

Shortcut query


B.

Shortcut reply


C.

Shortcut offer


D.

Shortcut forward


Expert Solution
Questions # 50:

Exhibit 1.

Question # 50

Exhibit 2.

Question # 50

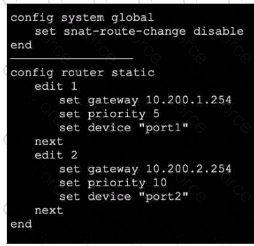
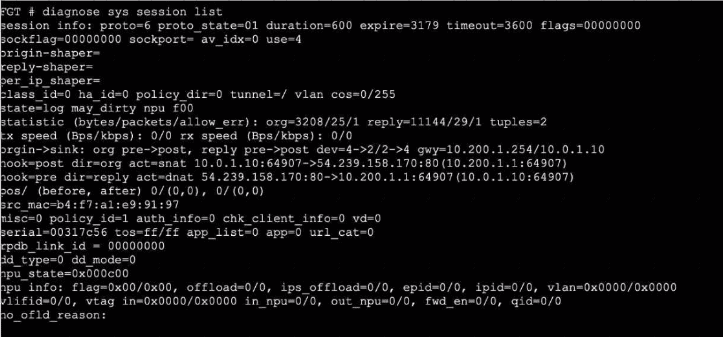
Refer to the exhibits, which show the configuration on FortiGate and partial internet session information from a user on the internal network.

An administrator would like to lest session failover between the two service provider connections.

Which two changes must the administrator make to force this existing session to immediately start using the other interface? (Choose two.)

Options:

A.

Change the priority of the port1 static route to 11.


B.

Change the priority of the port2 static route to 5.


C.

Configure unset snat-route-change to return it to the default setting.


D.

Configure set snat-route-change enable.


Expert Solution
Viewing page 5 out of 6 pages
Viewing questions 41-50 out of questions