Pre-Winter Sale Special Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: force70

Pass the Cisco CCNP Security 300-715 Questions and answers with CertsForce

Viewing page 7 out of 10 pages
Viewing questions 61-70 out of questions
Questions # 61:

What must match between Cisco ISE and the network access device to successfully authenticate endpoints?

Options:

A.

SNMP version


B.

shared secret


C.

certificate


D.

profile


Expert Solution
Questions # 62:

An engineer is implementing Cisco ISE and needs to configure 802.1X. The port settings are configured for port-based authentication. Which command should be used to complete this configuration?

Options:

A.

dot1x pae authenticator


B.

dot1x system-auth-control


C.

authentication port-control auto


D.

aaa authentication dot1x default group radius


Expert Solution
Questions # 63:

What is the Microsoft security policy recommendation (or fast user switching in Cisco ISE?

Options:

A.

Disable BYOD posture agent.


B.

Enable fast user switching.


C.

Disable fast user switching.


D.

Enable Cisco Secure Client posture agent.


Expert Solution
Questions # 64:

What is the default port used by Cisco ISE for NetFlow version 9 probe?

Options:

A.

UDP 9996


B.

UDP 9997


C.

UDP 9998


D.

UDP 9999


Expert Solution
Questions # 65:

Which configuration is required in the Cisco ISE authentication policy to allow Central Web Authentication?

Options:

A.

MAB and if user not found, continue


B.

MAB and if authentication failed, continue


C.

Dot1x and if user not found, continue


D.

Dot1x and if authentication failed, continue


Expert Solution
Questions # 66:

An enterprise uses a separate PSN for each of its four remote sites. Recently, a user reported receiving an " EAP-TLS authentication failed " message when moving between remote sites. Which configuration must be applied on Cisco ISE?

Options:

A.

Use a third-party certificate on the network device.


B.

Add the device to all PSN nodes in the deployment.


C.

Renew the expired certificate on one of the PSN.


D.

Configure an authorization profile for the end users.


Expert Solution
Questions # 67:

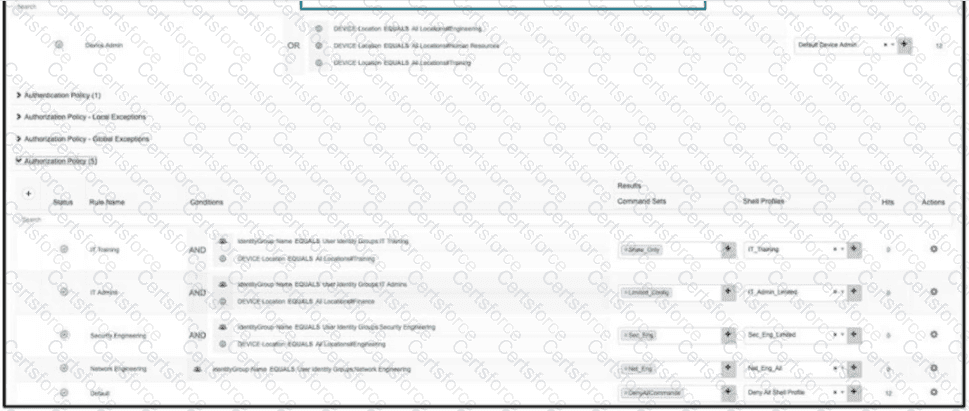
Refer to the exhibit.

Question # 67

An organization recently implemented network device administration using Cisco ISE. Upon testing the ability to access all of the required devices, a user in the Cisco ISE group IT Admins is attempting to login to a device in their organization ' s finance department but is unable to. What is the problem?

Options:

A.

The IT training rule is taking precedence over the IT Admins rule.


B.

The authorization conditions wrongly allow IT Admins group no access to finance devices.


C.

The finance location is not a condition in the policy set.


D.

The authorization policy doesn ' t correctly grant them access to the finance devices.


Expert Solution
Questions # 68:

During BYOD flow, from where does a Microsoft Windows PC download the Network Setup Assistant?

Options:

A.

Cisco App Store


B.

Microsoft App Store


C.

Cisco ISE directly


D.

Native OTA functionality


Expert Solution
Questions # 69:

A user is attempting to register a BYOD device to the Cisco ISE deployment, but needs to use the onboarding policy to request a digital certificate and provision the endpoint. What must be configured to accomplish this task?

Options:

A.

A native supplicant provisioning policy to redirect them to the BYOD portal for onboarding


B.

The Cisco AnyConnect provisioning policy to provision the endpoint for onboarding


C.

The BYOD flow to ensure that the endpoint will be provisioned prior to registering


D.

The posture provisioning policy to give the endpoint all necessary components prior to registering


Expert Solution
Questions # 70:

An engineer must use Cisco ISE to provide network access to endpoints that cannot support 802.1X. The endpoint MAC addresses must be allowlisted by configuring an endpoint identity group. These configurations were performed:

Configured an identity group named allowlist

Configured the endpoints to use the MAC address of incompatible 802.1X devices

Added the endpoints to the allowlist identity group

Configured an authentication policy for MAB users

What must be configured?

Options:

A.

Authorization profile that has the PermitAccess permission and matches the allowlist identity group


B.

Authentication profile that has the PermitAccess permission and matches the allowlist identity group


C.

Authorization policy that has the PermitAccess permission and matches the allowlist identity group


D.

Logical profile that matches the allowlist identity group based on the configured policy


Expert Solution
Viewing page 7 out of 10 pages
Viewing questions 61-70 out of questions