Pre-Winter Sale Special Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: force70

Pass the Cisco CCNP Security 300-715 Questions and answers with CertsForce

Viewing page 8 out of 10 pages
Viewing questions 71-80 out of questions
Questions # 71:

An administrator replaced a PSN in the distributed Cisco ISE environment. When endpoints authenticate to it, the devices are not getting the right profiles or attributes and as a result, are not hitting the correct policies. This was working correctly on the previous PSN. Which action must be taken to ensure the endpoints get identified?

Options:

A.

Verify that the MnT node is tracking the session.


B.

Verify the shared secret used between the switch and the PSN.


C.

Verify that the profiling service is running on the new PSN.


D.

Verify that the authentication request the PSN is receiving is not malformed.


Expert Solution
Questions # 72:

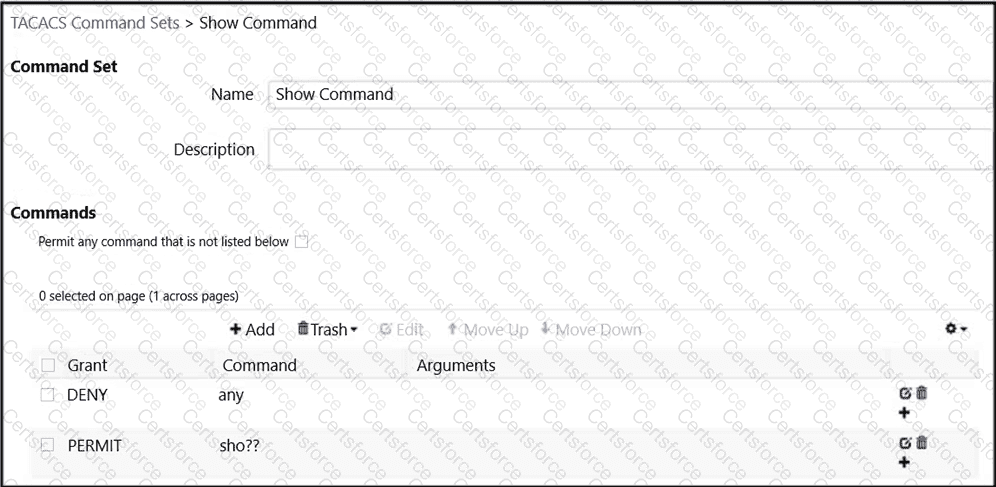
Refer to the exhibit.

Question # 72

An engineer is creating a new TACACS* command set and cannot use any show commands after togging into the device with this command set authorization Which configuration is causing this issue?

Options:

A.

Question marks are not allowed as wildcards for command sets.


B.

The command set is allowing all commands that are not in the command list


C.

The wildcard command listed is in the wrong format


D.

The command set is working like an ACL and denying every command.


Expert Solution
Questions # 73:

An administrator enables the profiling service for Cisco ISE to use for authorization policies while in closed mode. When the endpoints connect, they receive limited access so that the profiling probes can gather information and Cisco ISE can assign the correct profiles. They are using the default values within Cisco ISE. but the devices do not change their access due to the new profile. What is the problem ' ?

Options:

A.

In closed mode, profiling does not work unless CDP is enabled.


B.

The profiling probes are not able to collect enough information to change the device profile


C.

The profiler feed is not downloading new information so the profiler is inactive


D.

The default profiler configuration is set to No CoA for the reauthentication setting


Expert Solution
Questions # 74:

A network engineer must configure BYOD using Cisco ISE. In the deployment, the users must be able to submit CSR through the end devices. Which two features must be enabled to meet the requirement?

(Choose two.)

Options:

A.

Define a certificate group tag.


B.

A new BYOD portal must be created.


C.

A certificate provisioning portal must be configured.


D.

Cisco ISE Internal CA service must be enabled.


E.

Add SuperAdmin account into portal admin group.


Expert Solution
Questions # 75:

An organization has a fully distributed Cisco ISE deployment When implementing probes, an administrator must scan for unknown endpoints to learn the IP-to-MAC address bindings. The scan is complete on one FPSN. but the information is not available on the others. What must be done to make the information available?

Options:

A.

Scanning must be initiated from the PSN that last authenticated the endpoint


B.

Cisco ISE must learn the IP-MAC binding of unknown endpoints via DHCP profiling, not via scanning


C.

Scanning must be initiated from the MnT node to centrally gather the information


D.

Cisco ISE must be configured to learn the IP-MAC binding of unknown endpoints via RADIUS authentication, not via scanning


Expert Solution
Questions # 76:

An engineer is configuring a posture policy for Windows 10 endpoints and wants to ensure that users in each AD group have different conditions to meet to be compliant. What must be done to accomplish this task?

Options:

A.

identify The users groups needed for different policies and create service conditions to map each one to its posture requirement


B.

Configure a simple condition for each AD group and use it in the posture policy for each use case


C.

Use the authorization policy within the policy set to group each AD group with their respective posture policy


D.

Change the posture requirements to use an AD group lor each use case then use those requirements in the posture policy


Expert Solution
Questions # 77:

What is the difference between how RADIUS and TACACS+ handle encryption?

Options:

A.

RADIUS encrypts only the username and password fields, whereas TACACS+ encrypts the entire packet.


B.

RADIUS encrypts the entire packet, whereas TACACS+ only encrypts the password field.


C.

RADIUS only encrypts the password field, whereas TACACS+ encrypts the payload of packet.


D.

RADIUS encrypts the entire packet, whereas TACACS+ encrypts only the username and password fields.


Expert Solution
Questions # 78:

What occurs when a Cisco ISE distributed deployment has two nodes and the secondary node is deregistered?

Options:

A.

The primary node restarts


B.

The secondary node restarts.


C.

The primary node becomes standalone


D.

Both nodes restart.


Expert Solution
Questions # 79:

A network administrator is configuring a secondary cisco ISE node from the backup configuration of the primary cisco ISE node to create a high availability pair The Cisco ISE CA certificates and keys must be manually backed up from the primary Cisco ISE and copied into the secondary Cisco ISE Which command most be issued for this to work?

Options:

A.

copy certificate Ise


B.

application configure Ise


C.

certificate configure Ise


D.

Import certificate Ise


Expert Solution
Questions # 80:

An engineer is testing Cisco ISE policies in a lab environment with no support for a deployment server. In order to push supplicant profiles to the workstations for testing, firewall ports will need to be opened. From which Cisco ISE persona should this traffic be originating?

Options:

A.

monitoring


B.

policy service


C.

administration


D.

authentication


Expert Solution
Viewing page 8 out of 10 pages
Viewing questions 71-80 out of questions