
Halloween Sale Special Limited Time 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: CFsave75

Pass the WatchGuard Locally-Managed Fireboxes Network-Security-Essentials Questions and answers with CertsForce

Viewing page 1 out of 2 pages
Viewing questions 1-10 out of questions
Questions # 1:

The Audit Trail report shows information about Firebox configuration changes. How can you make sure the Audit Trail report includes the names of the specific person that made each change? (Select one.)

Options:

A.

Enable the Logging > AuditTrack feature


B.

Create unique device administrator accounts for each Firebox administrative user


C.

Configure all Firebox administrators to use the Authentication Portal to log in to the Firebox


D.

Install the SSO Client on each computer used by Firebox administrators


E.

Configure your RADIUS server to send accounting messages to the Firebox


Expert Solution
Questions # 2:

If policies are automatically ordered, which of these policies has the highest precedence? (Select one.)

Options:

A.

HTTPS policy - From: Any-Trusted, Any-Optional To: Any-External


B.

HTTPS policy - From: Trusted To: Any-External


C.

Outgoing policy - From: Any-Trusted, Any-Optional To: Any-External


D.

HTTPS policy - From: User1@Firebox-DB To: Any-External


Expert Solution
Questions # 3:

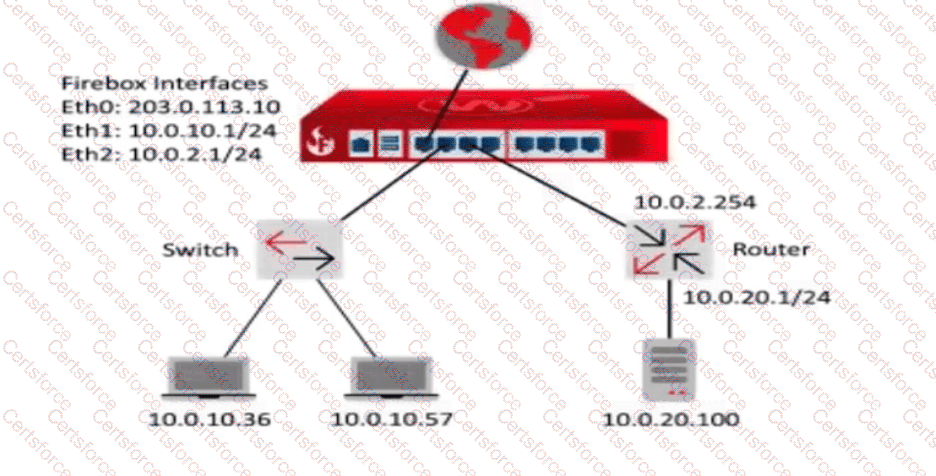
Clients on the 10.0.10.0/24 network must connect to the server at 10.0.20.100. Based on this image, what static route must you add to the Firebox for traffic to reach the server? (Select one.)
Question # 3

Options:

A.

Route to 10.0.10.0/24, Gateway 10.0.0.1


B.

Route to 10.0.20.0/24, Gateway 10.0.2.254


C.

Route to 10.0.20.0/24, Gateway 10.0.2.1


D.

Route to 10.0.2.0/24, Gateway 10.0.2.1


E.

Route to 10.0.20.0/24, Gateway 10.0.2.254


Expert Solution
Questions # 4:

What are some advantages of BOVPN virtual interfaces (route-based VPN) over classic policy-based BOVPNs? (Select two.)

Options:

A.

Supports VPN connectivity to cloud services


B.

Additional keep-alive options


C.

More flexible routing options


D.

Increased BOVPN throughput


E.

Additional encryption options


Expert Solution
Questions # 5:

Which of these options are private IPv4 address spaces described in RFC 1918 Address Allocation for Private Internets? (Select three.)

Options:

A.

192.168.0.0/16


B.

172.16.0.0/12


C.

102.0.2.0/24


D.

172.0.0.0/16


E.

10.0.0.0/8


Expert Solution
Questions # 6:

You have five public IP addresses available from your ISP. When you create a Static NAT action, you want to specify one of the public IP addresses for inbound traffic but do not see it in the IP address drop-down list. How can you change the Firebox configuration to see additional public IP addresses in the Static NAT action? (Select one.)

Options:

A.

Add secondary IP addresses to the external interface


B.

Configure 1-to-1 NAT for your entire subnet


C.

Add the public IP addresses to the From field of the policy that uses the Static NAT action


D.

Enable the Set Source IP option in the policy


E.

Add the IP addresses to the Dynamic NAT configuration


Expert Solution
Questions # 7:

Which WatchGuard tools can you use to review the traffic log messages generated by your Firebox? (Select three.)

Options:

A.

FireWatch


B.

Policy Manager


C.

Traffic Monitor


D.

Dimension


E.

Status Report


F.

WatchGuard Cloud


Expert Solution
Questions # 8:

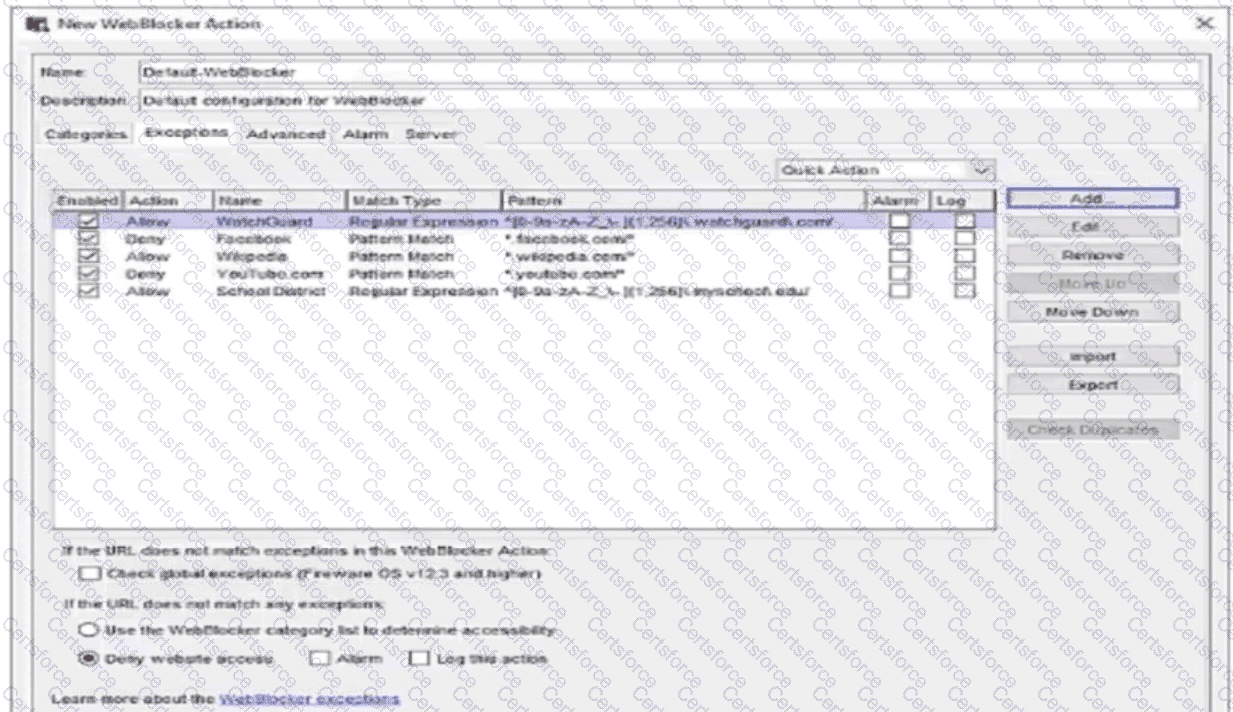
Which of these sites are denied by the WebBlocker action shown in this image? (Select three.)
Question # 8

Options:

A.

www.wikipedia.com/firewall


B.

www.youtube.com


C.

www.google.com


D.

schedule.myschool.edu


E.

www.watchguard.com/wgrd-blog


F.

login.facebook.com


Expert Solution
Questions # 9:

With the policies configured as shown in this image, HTTP traffic can be sent and received through Branch Office VPN tunnel 1 and tunnel 2.

Options:

A.

True


B.

False


Expert Solution
Questions # 10:

You configured your Firebox as a DHCP server and want to verify the status of the leased addresses. You found this information in Firebox System Manager > Status Report. What is true about DHCP leases in this deployment? (Select two.)

DHCP Leases Log Extract:

lease 10.20.1.100 {

interface vlan20;

starts 4 2023/03/09 21:42:25;

ends 4 2023/03/09 22:42:25;

binding state active;

hardware ethernet 00:50:56:9a:75:d0;

client-hostname "Laptop1";

}

Summary for 10.20.1.0/24: 1 out of 51 IPs are leased

lease 10.0.1.2 {

interface eth1;

starts 4 2023/03/09 21:42:33;

ends 5 2023/03/10 05:42:33;

binding state active;

hardware ethernet 00:50:56:b6:22:9f;

client-hostname "Server1";

}

Summary for 10.0.1.0/24: 1 out of 253 IPs are leased

Summary for all: 2 out of 304 IPs are leased

Options:

A.

The MAC address for the host using 10.0.1.2 is 00:50:56:9a:75


B.

DHCP leases for the 10.0.1.0/24 network are valid for 8 hours


C.

DHCP leases for the 10.20.1.0/24 network are valid for 24 hours


D.

252 IP addresses are currently available in the address pool for the 10.0.1.0/24 network


E.

The hostname Server1 is associated with the IP address 10.20.1.100


Expert Solution
Viewing page 1 out of 2 pages
Viewing questions 1-10 out of questions