
A customer wants FortiAnalyzer to run an automation stitch that executes a CLI command on FortiGate to block a predefined list of URLs, if a botnet command-and-control (C & C) server IP is detected.
Which FortiAnalyzer feature must you use to start this automation process?
Review the incident report. A fake HR login page was sent to several employees through email. The page copied the company’s branding and captured usernames and passwords. The attacker later used the stolen credentials to sign in through the company’s web VPN. Which two MITRE ATT & CK tactics best characterize this report? Choose two answers.
You configured a queue called L1 Analysts and generated shifts to cover morning, evening, and overnight shifts, with two members covering each shift.
However, you noticed that all members of the queue are assigned ingested alerts in a round-robin fashion, instead of only users who are currently on shift.
What is the problem?
You configured a new module named Users. Next, you want to configure a playbook that creates users from ingested data. When new records are created, you want to ensure that duplicate users do not overwrite existing user records and their fields. However, you also want the playbook to continue running even if duplicates are encountered so that any non-duplicate records are still created. Which two actions fulfill the requirements? Choose two answers.
When you use a manual trigger to save user input as a variable, what is the correct Jinja expression to reference the variable? (Choose one answer)
Refer to the exhibit.
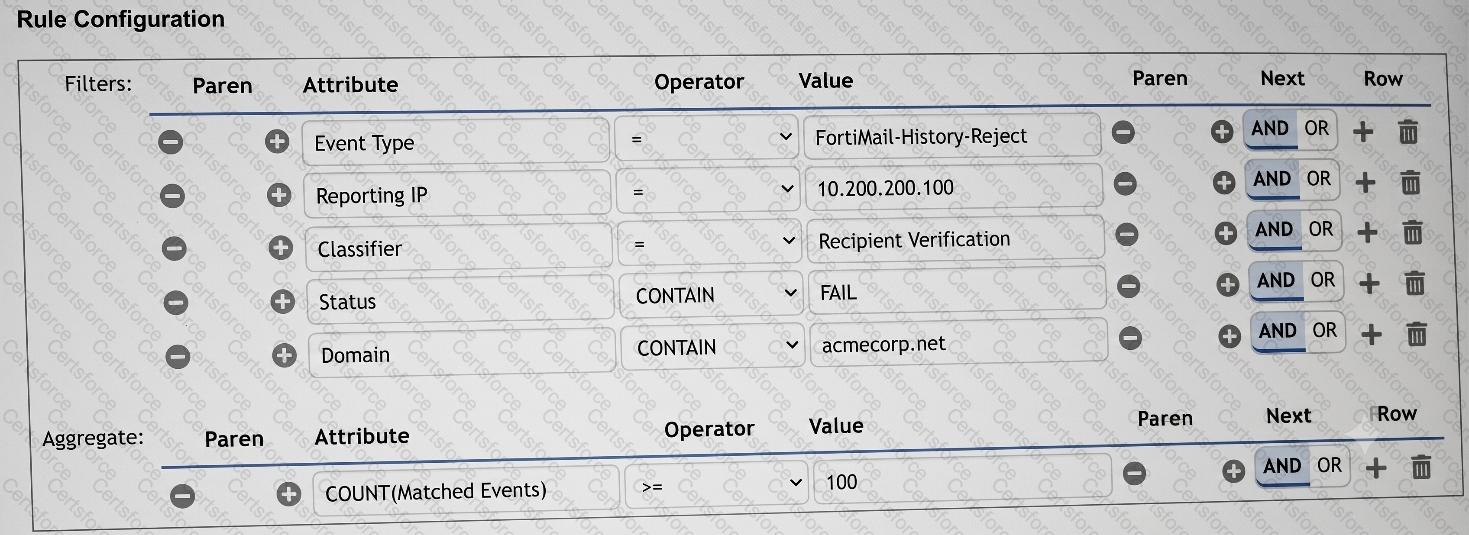
You want to configure a FortiSIEM rule that triggers when a FortiMail device reports at least 100 recipient verification failures for different email accounts in the domain acmecorp.net. What would you add or modify to accomplish this task? Choose one answer.
Which two statements accurately describe the Custom API Endpoint playbook trigger? Choose two answers.
Refer to the exhibit.
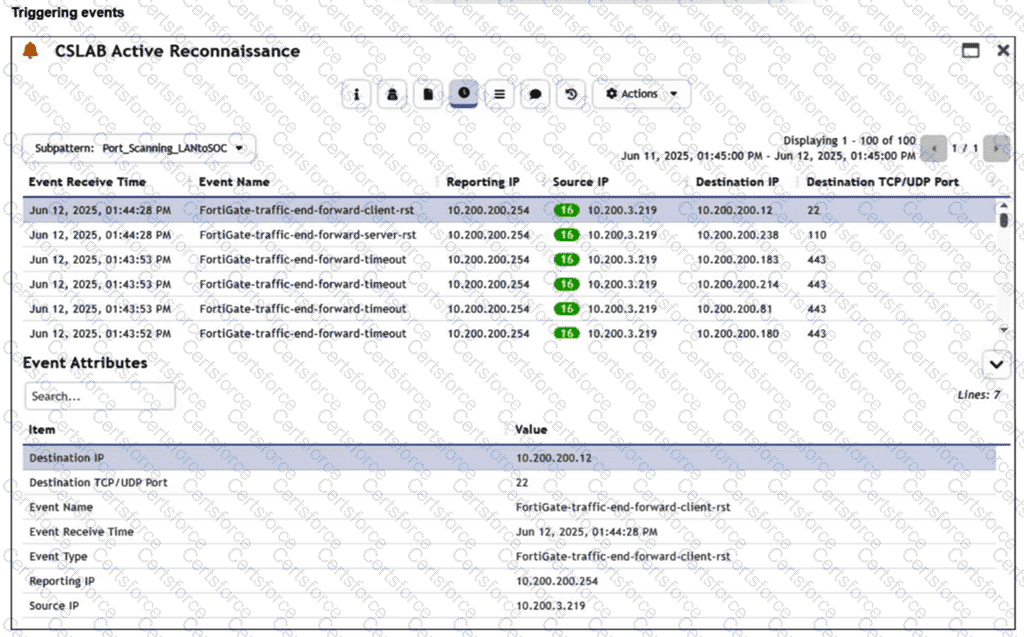
You are reviewing the Triggering Events page for a FortiSIEM incident. You want to remove the Reporting IP column because you have only one firewall in the topology. How do you accomplish this? (Choose one answer)
