For which of the following situations would a human-in-the-loop be most recommended?
Which of the following corporate policies would a security architect most likely reference when configuring an AI system to conduct input filtering?
A company deploys an internet-facing chatbot using RAG. Logs show that an administrator can retrieve employee names and usernames while an employee receives ' information not available. ' Which of the following is reducing the risk of sensitive data exposure in this scenario?
A penetration tester is assessing the controls of a deployed AI system that is designed to search and return the contents of files.
The tester runs the following:
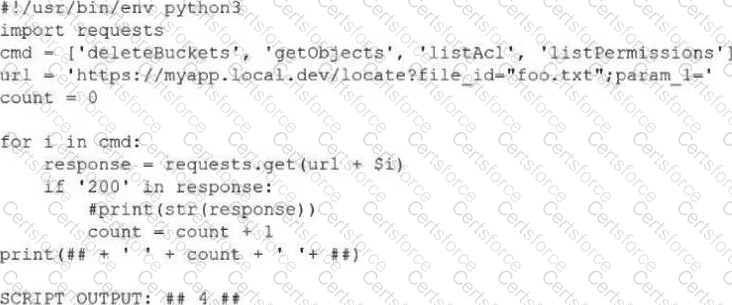
Which of the following is the best control to prevent abuse of the system?
After the deployment of an AI system, an organization is unable to identify who approved the system and the method of validation. Which of the following governance failures occurred?
A cyberthreat intelligence (CTI) analyst conducts research about a threat during a recent attack. The analyst uses an AI threat-modeling resource to find the relevant risks and utilizes causal and domain taxonomies. Which of the following best describes which resource the analyst is using?
Which of the following attacks is most enabled by AI-generated content?
A company uses human review for software development validation and wants to add another validation layer.
Which of the following should a security administrator use to accomplish this task?
A cybersecurity analyst must use pattern recognition on a data set containing unstructured data.
Which of the following models is the best for this task?
A group of security engineers is developing a SIEM system that will be able to ingest data from multiple structured and unstructured sources, have a chatbot integrated with an LLM that the security analyst can interact with, and provide insights from the SIEM alert data.
Which of the following techniques should the security engineers consider before collecting the data from the respective sources?