You need to implement the function apps to meet the technical requirements.
Which apps should you include in the implementation?
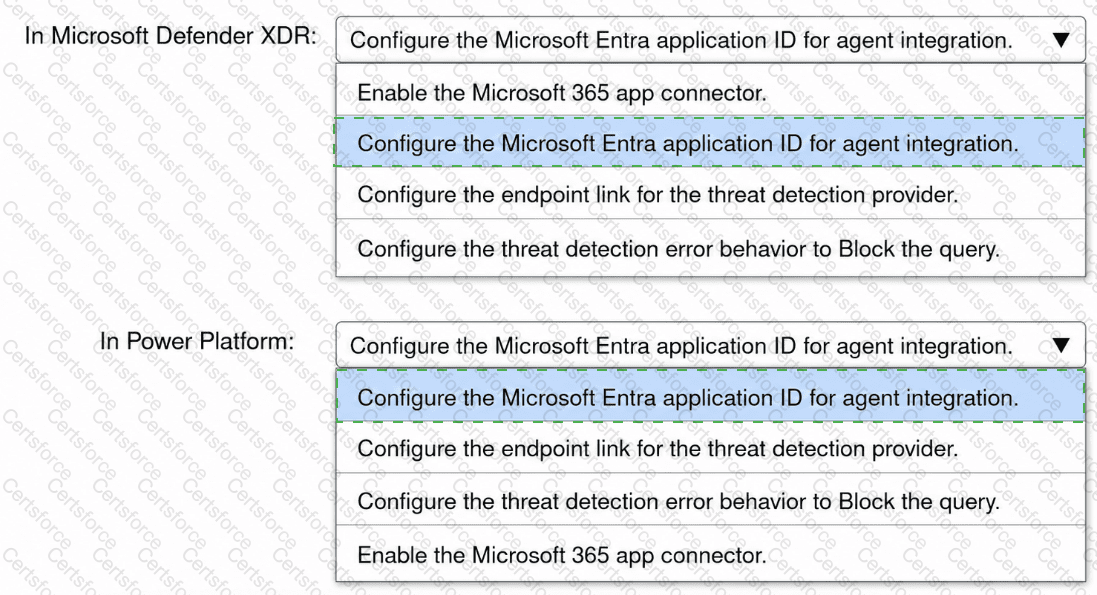
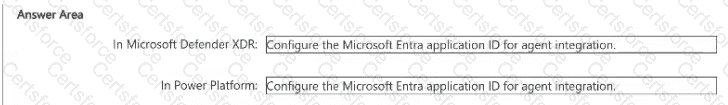
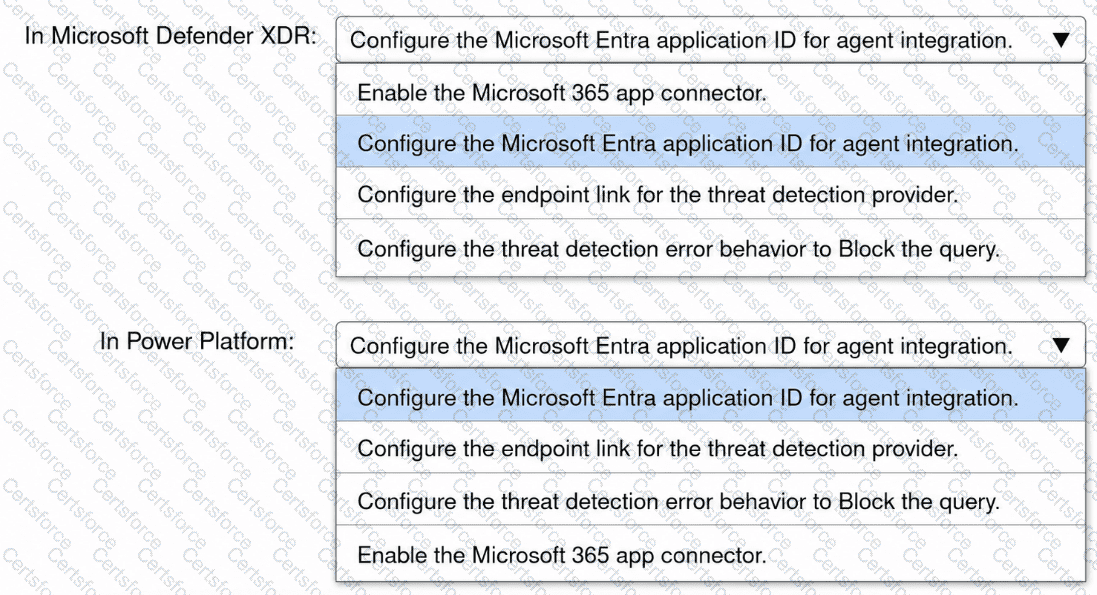
You have a Microsoft Defender XDR environment.
You have a Microsoft Power Platform environment where makers publish custom Microsoft Copilot Studio agents.
You need to enable real-time protection so that suspicious tool invocations are blocked before an agent runs actions, and related alerts appear in the Microsoft Defender portal.
What should you do? To answer, drag the appropriate actions to the correct services. Each action may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
You need to implement the planned change for WAF1. The solution must minimize administrative effort.
What should you do?
You create a new Microsoft Sentinel workspace named Workspace1.
Workspace1 ingests Azure Firewall logs that are used only occasionally during investigations.
You need to retain the logs for seven years at the lowest cost. The solution must ensure that investigators ran search the retained data when needed.
What should you do?
You have an Azure subscription named Sub1 that contains multiple virtual machines and an Azure key vault named KV1.
Each virtual machine has a system-assigned managed identity. Sub1 has Microsoft Defender for Servers enabled. Defender for Servers has agentless scanning enabled.
Some virtual machines use managed disks that are encrypted by using customer-managed keys stored in KV1.
You discover that the affected virtual machines fail to return agentless scanning results in Microsoft Defender for Cloud.
You need to ensure that agentless scanning can analyze the virtual machines.
What should you do?
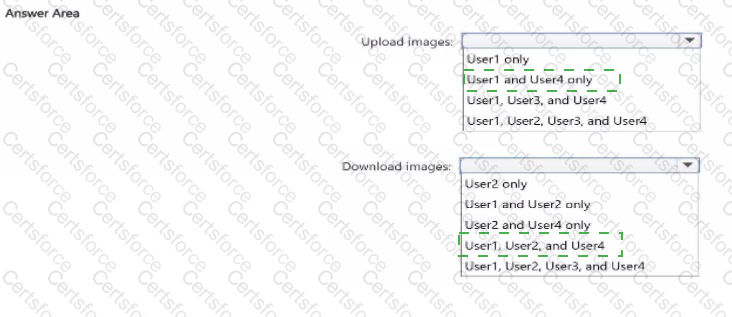
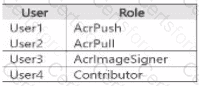
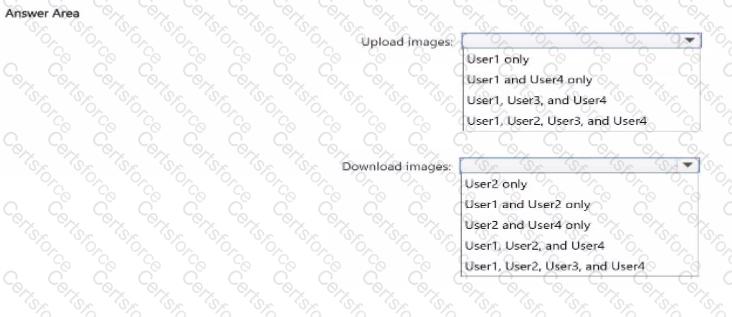
You have an Azure Container Registry named Registry1-
You add role assignments for Registry1 as shown in the following table.
You have an Azure subscription that contains a virtual network named VNet1.
VNet1 contains an Azure VPN gateway named Gateway1 that is configured for Point-to-Site (P2S) connections.
You have a Microsoft 365 E5 subscription.
You need to configure a VPN authentication method for Gateway1. The solution must enforce Conditional Access policies during VPN sign-ins.
Which authentication method should you configure?
You have an Azure virtual network named VNet1 that contains a subnet named Subnet1.
You create a storage account named storage1.
You need to ensure that access to storage1 can be managed only by a network security group (NSG) linked to Subnet1.
What should you use?
You use Azure Virtual Network Manager to manage multiple virtual networks in a network group named Group1
You discover that the virtual machines in Group1 are accessible from the internet by using TCP port 3389.
You need to block inbound TCP 3389 from the internet across all the virtual networks in Group1 The solution must minimize administrative effort.
What should you use?
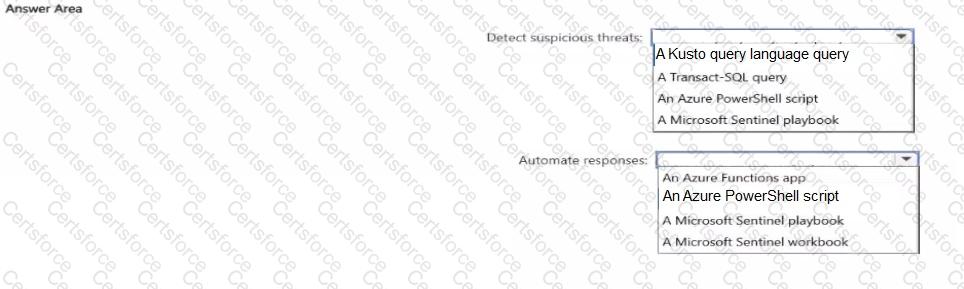
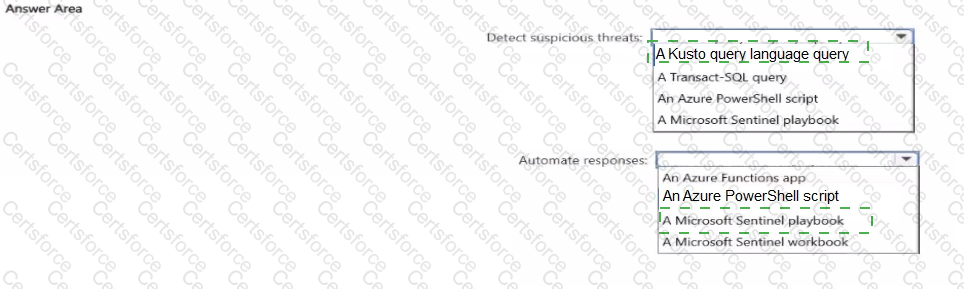
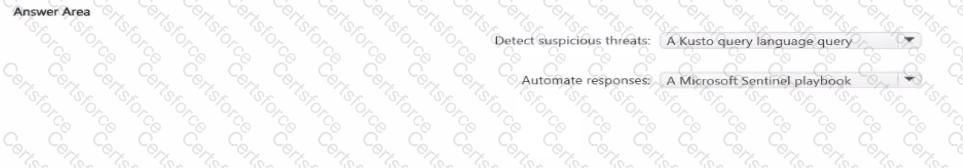
You plan to use Microsoft Sentinel to create an analytic rule that will detect suspicious threats and automate responses. Which components are required for the rule ' lo answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.