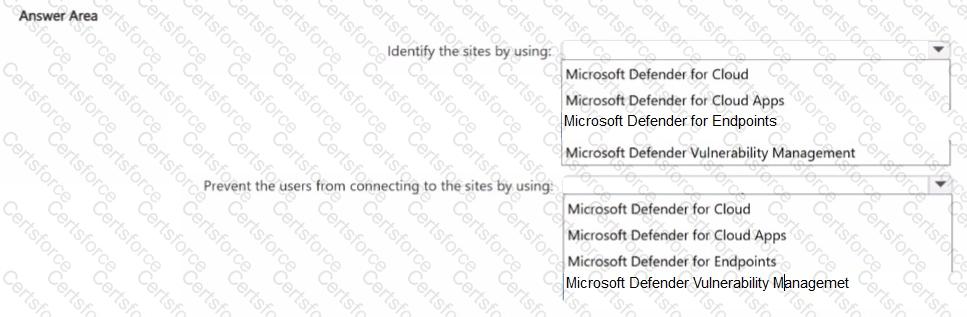
You have a Microsoft 365 subscription. The subscription contains Windows 11 devices that are protected by using Microsoft Defender XDR You need to block access to file sharing sites from the devices. The solution must meet the following requirements:
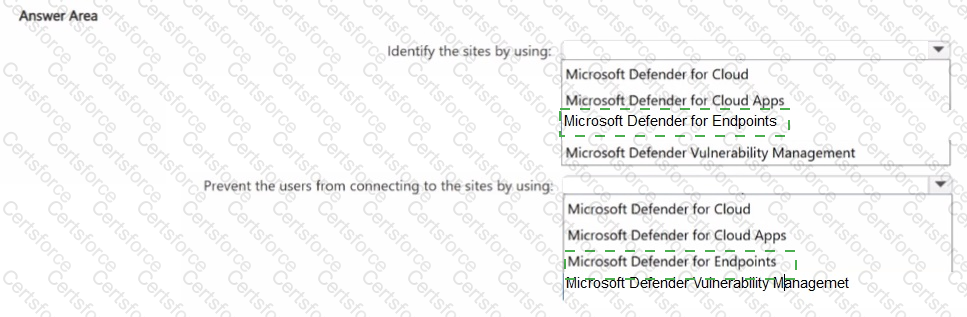
• Identify file sharing sites to which users have connected during the last 90 days.
• Prevent the users from connecting to the identified file sharing sites.
• Minimize administrative effort.
What should you use to identify the file sharing sites, and which Microsoft Defender service should you use to prevent the users from connecting to the sites? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Your company develops several applications that are accessed as custom enterprise applications in Microsoft Entra ID. You need to recommend a solution to prevent users on a specific list of countries from connecting to the applications. What should you include in the recommendation?
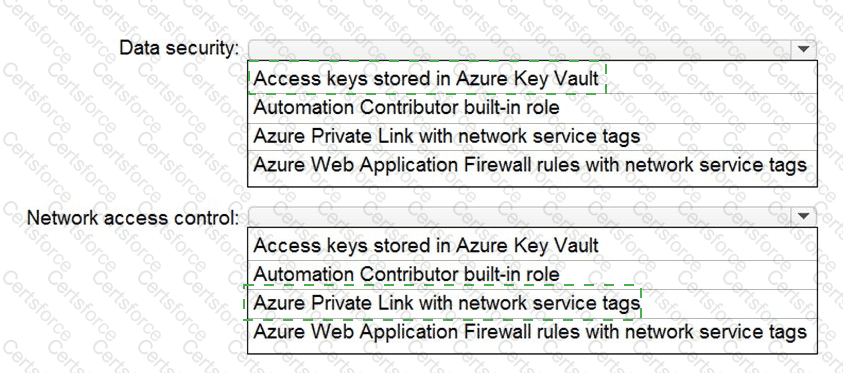
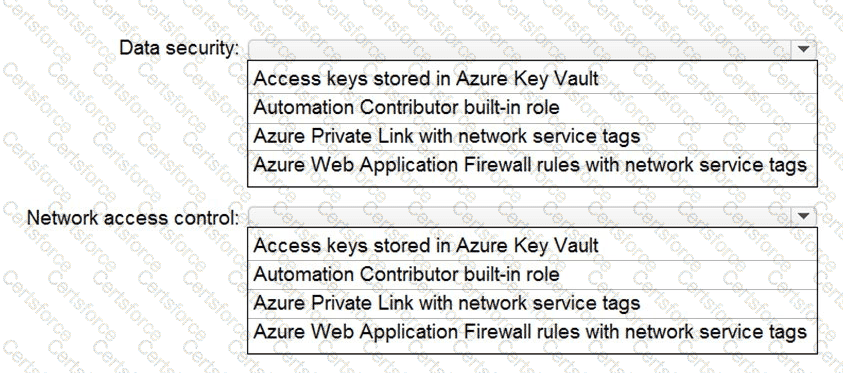
You are designing security for a runbook in an Azure Automation account. The runbook will copy data to Azure Data Lake Storage Gen2.
You need to recommend a solution to secure the components of the copy process.
What should you include in the recommendation for each component? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You have an Azure subscription.
Your company has a governance requirement that resources must be created in the West Europe or North Europe Azure regions.
What should you recommend using to enforce the governance requirement?
You have an Azure AD tenant that syncs with an Active Directory Domain Services (AD DS) domain.
You are designing an Azure DevOps solution to deploy applications to an Azure subscription by using continuous integration and continuous deployment (CI/CD) pipelines.
You need to recommend which types of identities to use for the deployment credentials of the service connection. The solution must follow DevSecOps best practices from the Microsoft Cloud Adoption Framework for Azure.
What should you recommend?
Your company has a hybrid cloud infrastructure.
Data and applications are moved regularly between cloud environments.
The company ' s on-premises network is managed as shown in the following exhibit.
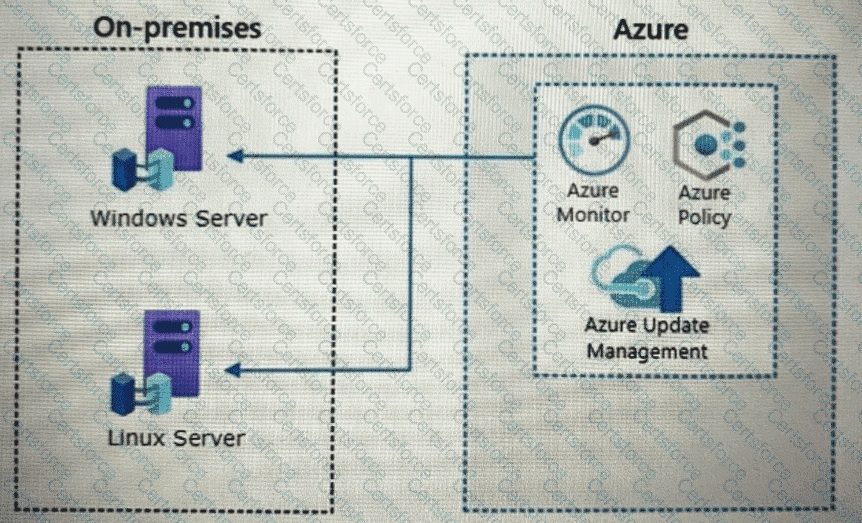
You are designing security operations to support the hybrid cloud infrastructure. The solution must meet the following requirements:
Govern virtual machines and servers across multiple environments.
Enforce standards for all the resources across all the environment across the Azure policy.
Which two components should you recommend for the on-premises network? Each correct answer presents part of the solution.
NOTE Each correct selection is worth one point.
You have an Azure AD tenant that syncs with an Active Directory Domain Services (AD DS) domain.
You have an on-premises datacenter that contains 100 servers. The servers run Windows Server and are backed up by using Microsoft Azure Backup Server (MABS).
You are designing a recovery solution for ransomware attacks. The solution follows Microsoft Security Best Practices.
You need to ensure that a compromised administrator account cannot be used to delete the backups
What should you do?
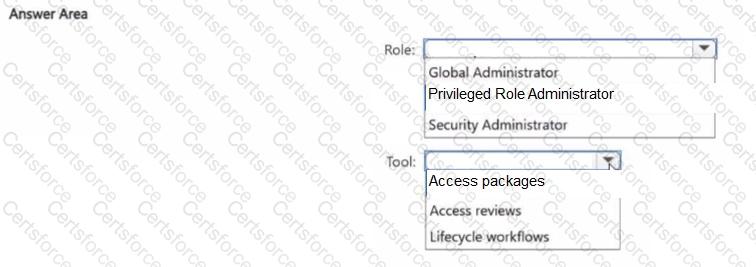
You have a Microsoft Entra tenant that contains two users named User! and User2.
A recent audit reveals that User1 has a permanent assignment to the User Administrator role, even though the user account belongs to a former contractor
The security team at your company has the following requirements:
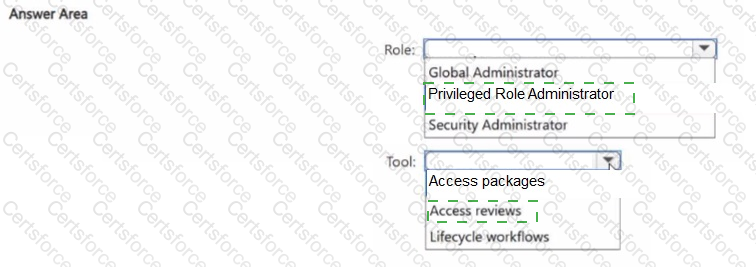
• Ensure that all privileged role assignments are periodically validated.
• Use Privileged Identity Management (PIM) to automate and enforce the validation process
You need to ensure that User2 can meet the security requirements. The solution must follow the principle of least privilege. Which role should you assign to User2, and what should User2 use? To answer, select the appropriate options in the answer area.
You have a Microsoft Sentinel deployment.
You are developing a solution to ensure that compliance with the MITRE ATT & CK framework is maintained as the framework
evolves.
You need to recommend a solution to identify which MITRE ATT & CK techniques are NOT addressed by the current Microsoft Sentinel deployment
What should you include in the recommendation?
You have a Microsoft 365 E5 subscription.
You need to recommend a security solution that meets the following requirements:
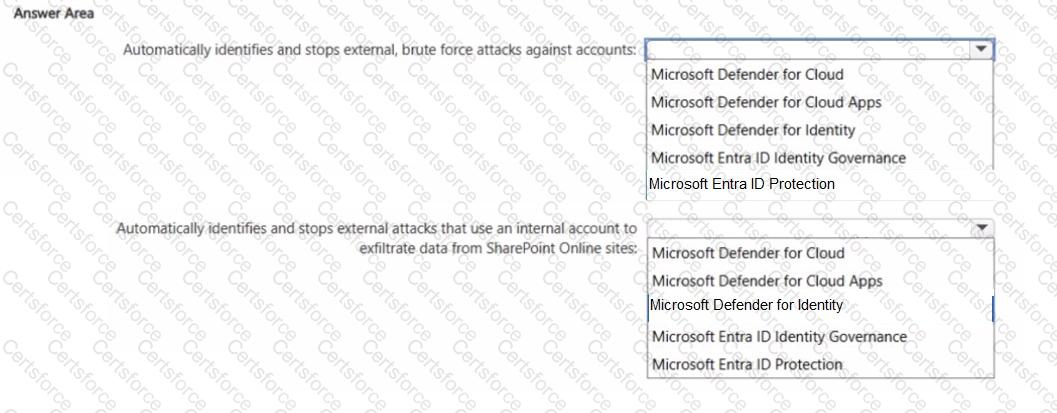
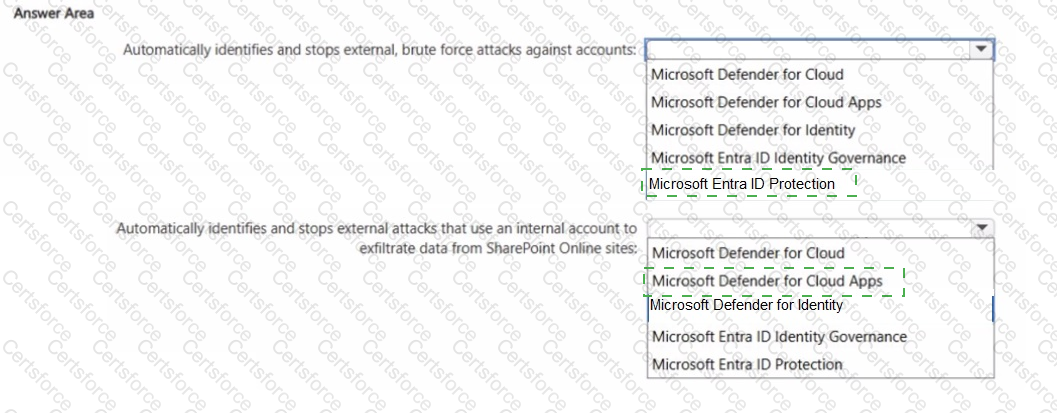
• Automatically identifies and stops external, brute force attacks against accounts in the subscription
• Automatically identifies and stops external attacks that use an internal account to exfiltrate data from Microsoft SharePoint Online sites in the subscription
What should you include in the recommendation for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.