Comprehensive Technical Explanation:
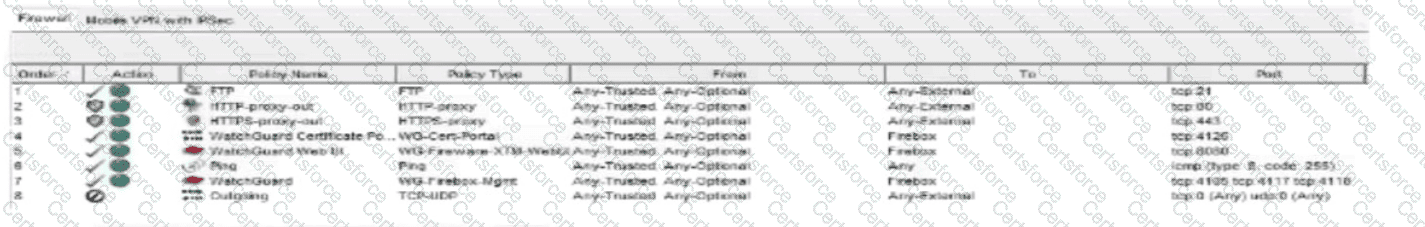
Although policy rule 3 (HTTPS-proxy-out) explicitly allows outbound HTTPS traffic (TCP port 443) from Any-Trusted and Any-Optional to Any-External, establishing an HTTPS connection to an external fully qualified domain name like https://www.watchguard.com inherently requires Domain Name System (DNS) resolution. Client workstations must query a DNS server over UDP or TCP port 53 to resolve www.watchguard.com to a routable IP address before initiating the TCP three-way handshake on port 443.
Evaluating the ordered policy table reveals that there is no active policy permitting DNS traffic (port 53) outbound from Any-Trusted or Any-Optional to Any-External or to the Firebox. Furthermore, rule 8 is an explicit Deny policy for Outgoing (TCP-UDP) that blocks all remaining unhandled TCP and UDP traffic traversing from internal interfaces to Any-External. Because client DNS requests are dropped by the firewall, internal clients cannot resolve domain names, preventing them from establishing the outbound session to www.watchguard.com. Therefore, the statement is False.
[Reference: WatchGuard Network Security Essentials — Networking, Policies, and NAT: Rule Base Evaluation, DNS Dependencies, and Outbound Policy Requirements., ――――――――――――――――――――――――――――――――――――――――――――――――――――――――――]


Submit