
A customer operates an HPE Aruba Networking ClearPass cluster. The customer has AOS-CX switches that use 802.1X authentication with HPE Aruba Networking ClearPass Policy Manager (CPPM).
The switches use local port-access policies. The customer wants to begin tunneling only wired clients that successfully pass user authentication to an HPE Aruba Networking gateway cluster. The gateway cluster must place these clients in the eth-internet role. The gateway must also assign clients to VLAN 20.
The planned enforcement policy and profiles are shown below:
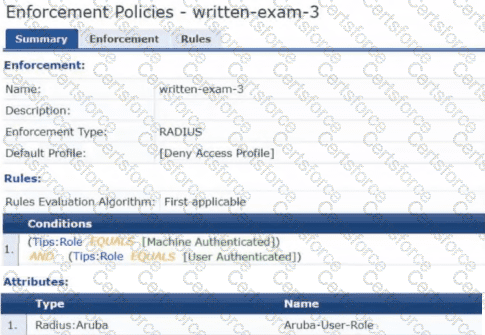
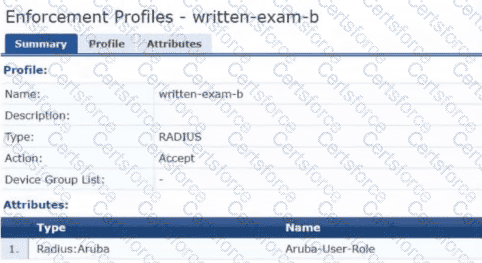
* Policy: `written-exam-3`
* Conditions: `(Tips:Role EQUALS [Machine Authenticated]) AND (Tips:Role EQUALS [User Authenticated] )`
* Profile: `written-exam-b` (Attributes: `Radius:Aruba-User-Role = Aruba-User-Role`)
The gateway cluster includes two gateways with the following IP addresses:
Gateway 1: VLAN 4085 (system IP) = 10.20.4.21 | VLAN 20 (users) = 10.20.20.1 | VLAN 4094 (WAN) = 198.51.100.14
Gateway 2: VLAN 4085 (system IP) = 10.20.4.22 | VLAN 20 (users) = 10.20.20.2 | VLAN 4094 (WAN) = 198.51.100.12 | VRRP on VLAN 20 = 10.20.20.254
Refer to the scenario. Assume the correct UBT zone and port-access role settings have been configured. However, the solution does not work.
What else must you ensure you do?

Submit