
Black Friday Reward - Upto 75% off - Ends in 0d 00h 00m 00s - Coupon code: CFsave75

Pass the CyberArk Guardian GUARD Questions and answers with CertsForce

Viewing page 1 out of 2 pages
Viewing questions 1-10 out of questions
Questions # 1:

A new Vault is to be deployed in a highly regulated environment. Regulations require that every operating system on the network be updated regularly.

How does CyberArk recommend automatically updating hardened Vaults?

Options:

A.

Using a dedicated WSUS server and install patches monthly.


B.

Vaults do not require OS updates.


C.

Manually install updates whenever CyberArk notifies you.


D.

Integrate the Vault with the domain for monthly updates.


Expert Solution
Questions # 2:

A customer has a policy that denies all direct RDP access from their workstation network security zone to the server network security zone. Only HTTPS is permitted into the server network security zone.

What recommendation would you give the customer?

Options:

A.

Do not use the PSM. Allow end users to use the Show/Copy feature.


B.

Request an exception to allow RDP access from the workstation network zone to the network security zone.


C.

Provide to virtual desktop to each user. Users will access the PSM from the virtual desktop that sits within the server network security zone.


D.

Deploy an HTML5 gateway in the server network security zone.


Expert Solution
Questions # 3:

What does a SCIM Server refer to?

Options:

A.

Secure for CyberArk Identity Manager.


B.

System for Cross Identity Management.


C.

System for CyberArk Identity Management.


D.

Secure Compute Information Manager.


Expert Solution
Questions # 4:

The Active Directory manager asks you to temporarily enable Object Level Access Control (OLAC) on a Safe they own so they can control which users may use a particular Domain Admin account.

What OLAC limitation should you explain to them?

Options:

A.

OLAC does not enable granular control of which users can use a specific object.


B.

Once enabled, object level access control cannot be disabled.


C.

With object level access control enabled, PSM operations on the managed accounts are not supported.


D.

New accounts cannot be added to the safe, once OLAC is enabled.


Expert Solution
Questions # 5:

What level of support is a customer entitled to with 24x7 support?

Options:

A.

Enables customers to call the after hours Support hotline for all issues.


B.

Enables customers to call the after hours Support hotline for all Critical issues where no work can be completed in a Production environment.


C.

Enables customers to call the after hours Support hotline for all Critical or Serious issues where no work can be completed in a Production environment.


D.

Enables customers to call the after hours Support hotline for all Critical or Serious issues where no work can be completed in any environment.


Expert Solution
Questions # 6:

What should be the focus of Stage 1 of the CyberArk Blueprint?

Options:

A.

Primarily identities, accounts and systems that have the ability to control an entire environment, both in the cloud or on-prem.


B.

Universal technology platforms such as *NIX and Windows local accounts.


C.

High Risk/High Reward value use cases that are most critical to the operation of the business.


D.

Building integrations to CyberArk PAM such as automation, onboarding and dual control workflows.


Expert Solution
Questions # 7:

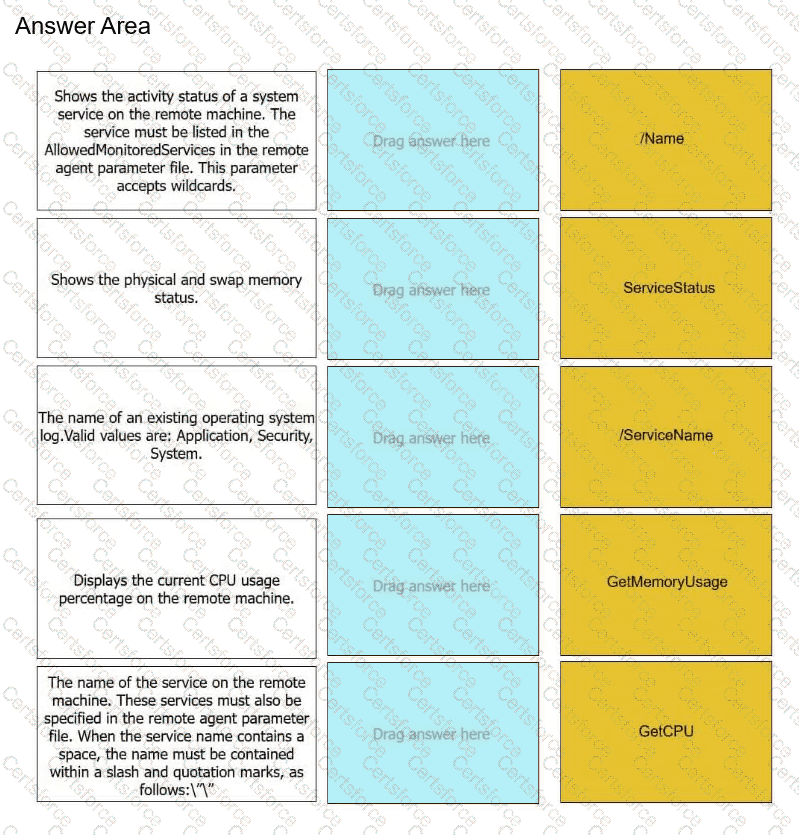
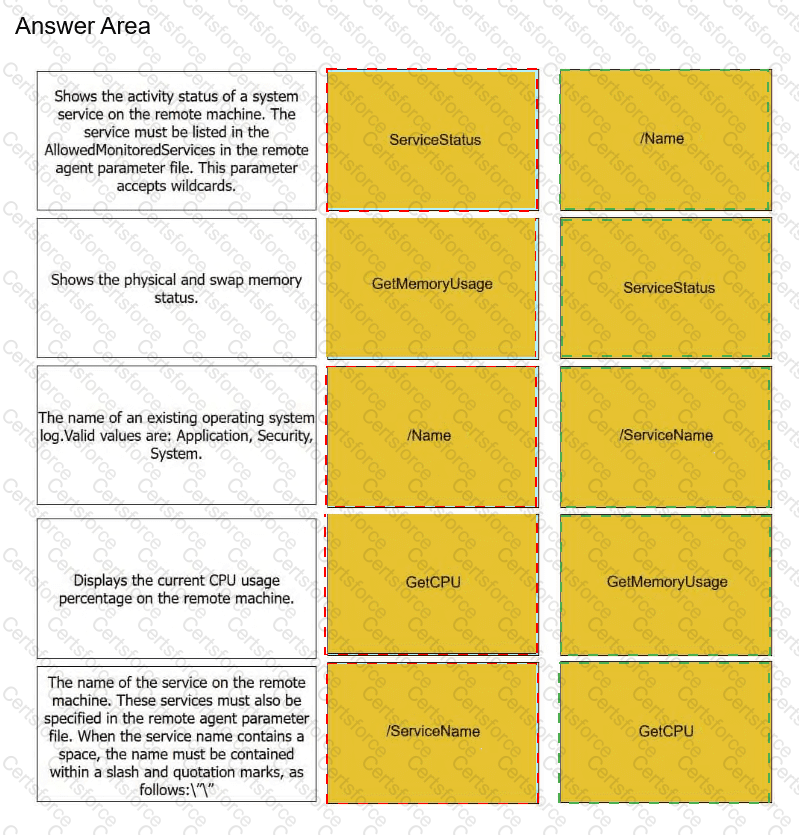
Remote Monitoring lets you receive various information from the EPV and the DR Vault on a remote machine.

Match each parameter to its description:
Question # 7


Expert Solution
Questions # 8:

A customer needs to implement CyberArk with the lowest possible recovery time objective for a Vault server failure in both the primary and secondary datacenters.

Which architecture is most suitable for this?

Options:

A.

Deploy a multi cloud, multi region Architecture with 4 vaults. 2 vaults per public cloud across different regions.


B.

Deploy both Primary and DR vault clusters in primary and secondary datacenters.


C.

Deploy Distributed vaults. 1 Primary vault and 1 satellite vault in the primary datacenter and 2 satellite vaults in the secondary datacenter.


D.

Deploy Primary and DR standalone vaults in a single public cloud environment within the same region across different availability zones.


Expert Solution
Questions # 9:

A financial institution uses CyberArk Privileged Session Manager (PSM) to monitor privileged access to production servers.

The security team requires authorized auditors to terminate suspicious privileged sessions immediately when potentially malicious administrative activity is detected.

An auditor can view active sessions in PVWA but cannot terminate them. The administrator confirms that session monitoring is enabled and the PSM infrastructure is functioning correctly.

What configuration should be implemented to allow the auditor to terminate active privileged sessions?

Options:

A.

Add the auditor to the Vault Administrators group and grant full administrative access to all Recording Safes.


B.

Enable the Require Dual Control Password Access Approval rule in the Master Policy and assign the auditor as an approver.


C.

Add the auditor to the PSMLiveSessionTerminators group and ensure that this group has the required membership in the Safes containing the managed accounts.


D.

Assign the auditor the Retrieve Accounts permission on the relevant Safes and enable automatic password reconciliation.


Expert Solution
Questions # 10:

In most cases, why should a failed CPM verification followed by a reconciliation action be considered a security incident?

Options:

A.

The secret may have been changed outside of CyberArk and is compromised.


B.

The secret is not configured for automatic reconciliation.


C.

The CPM should not be performing automatic reconciliation actions.


D.

The secret was rotated outside of an approved change-control window.


Expert Solution
Viewing page 1 out of 2 pages
Viewing questions 1-10 out of questions