You need to meet the technical requirements for the project documents.
What should you create in Microsoft Purview?
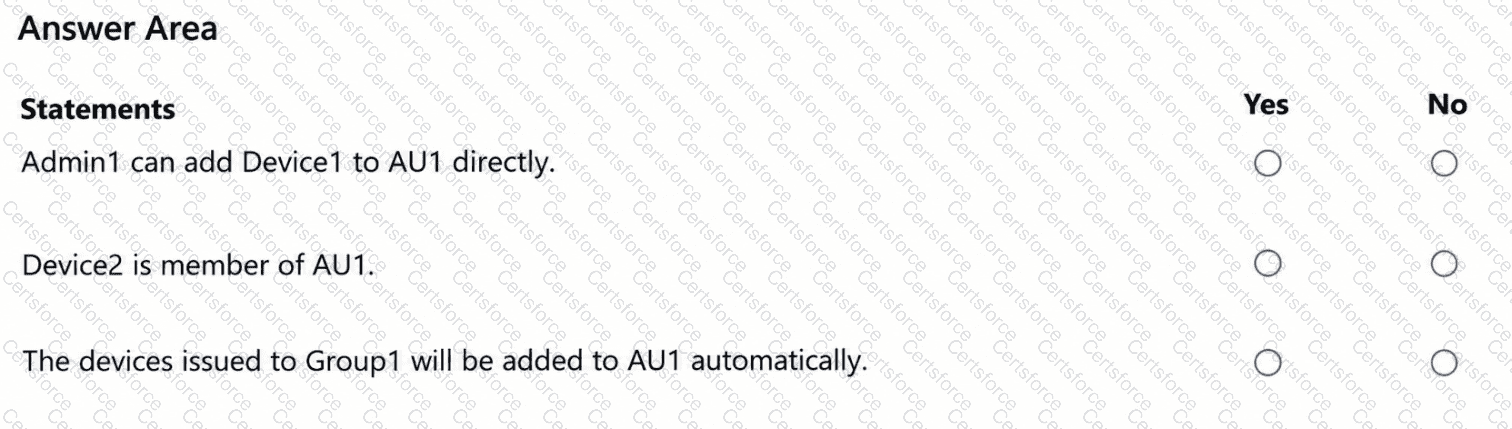
You need to evaluate the configuration of AU1.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
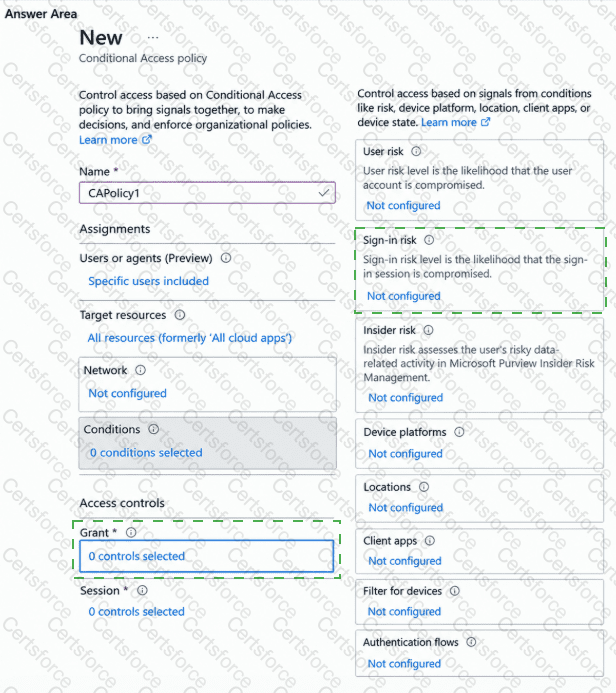
You need to implement the planned change for web search.
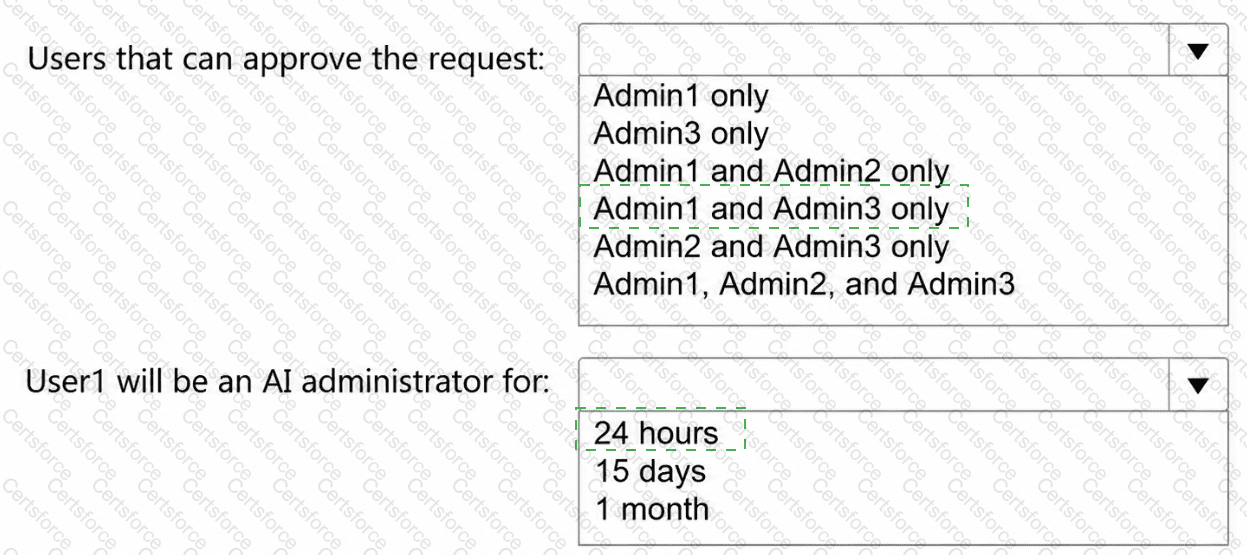
Which users can perform the configuration, and which portal should the user use? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
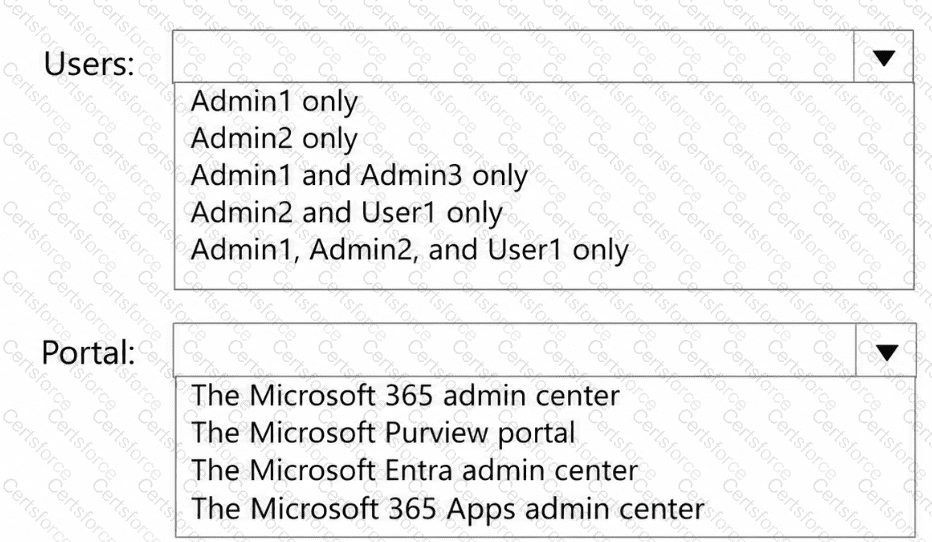
You need to implement the planned change for Group4.
Which cmdlet should you run?
You have a Microsoft 365 E5 subscription that uses Microsoft Defender for Office 365.
The subscription has the default inbound anti-spam policy and a custom Safe Attachments policy.
You need to identify the following information:
The number of email messages quarantined by zero-hour auto purge (ZAP)
The number of times users clicked a malicious link in an email message
Which Email & collaboration report should you use? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Your company has an office in London.
You have a Microsoft 365 subscription.
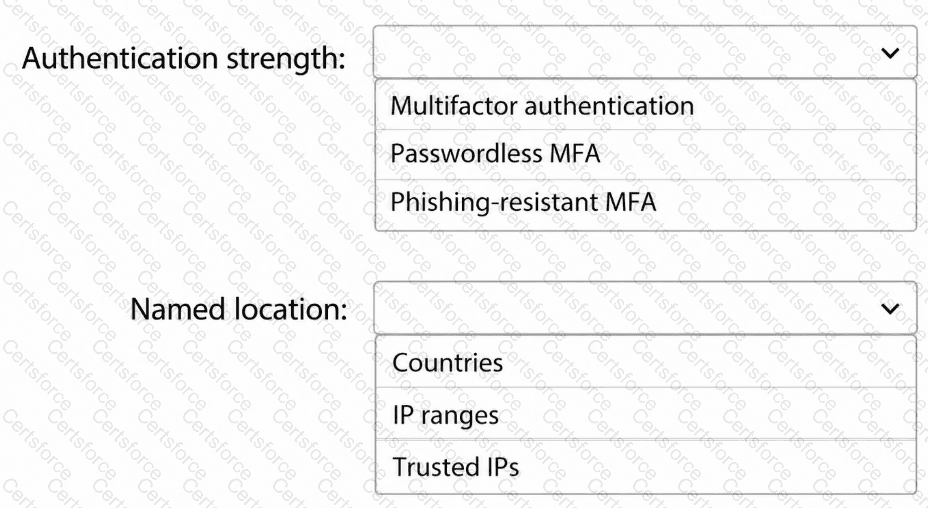
You need to create a Conditional Access policy named Policy1 that meets the following requirements:
Only FIDO2 passkeys, Windows Hello for Business, and certificates must be supported for authentication.
The London office must be marked as a trusted location and excluded from Policy1.
How should you configure Authentication strength in Policy1 and what should you use to define named location for the London office? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You have a Microsoft 365 subscription.
Your company has a customer ID associated to each customer. The customer IDs contain 10 numbers followed by 10 characters.
The following is a sample customer ID: 123-456-7890-abc-de-fghij.
You plan to create a data loss prevention (DLP) policy that will detect messages containing customer IDs.
What should you create to ensure that the DLP policy can detect the customer IDs?
You have a Microsoft 365 subscription that contains the resources shown in the following table.
Name
Description
Group1
Microsoft 365 group
User1
User that is assigned a Microsoft 365 Copilot license and is outside of Group1
User2
User that has access to Microsoft 365 Copilot Chat only and is in Group1
Microsoft SharePoint contains the folders shown in the following table.
Name
Description
Forecast
Has access set to Everyone except external users. Has a sensitivity label applied that encrypts files and grants usage rights to only Group1
Vendor Contracts
Has access set to Everyone except external users. Contains unlabeled files
For each of the following statements, select Yes if the statement is true. Otherwise, select No.

You have a Microsoft 365 E5 subscription that contains two groups named Group1 and Group2.
You need to create simulation automations for Attack simulation training as shown in the following table.
Target group
Requirement
Group1
Send an email that contains an attached HTML file. The file must direct users to a sign-in page.
Group2
Send an email that directs users to a document on a file sharing site. When the document is opened, code will run in the simulation.
Which technique should you use for each simulation? To answer, drag the appropriate techniques to the correct simulations. Each technique may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.

You have a Microsoft 365 E5 subscription.
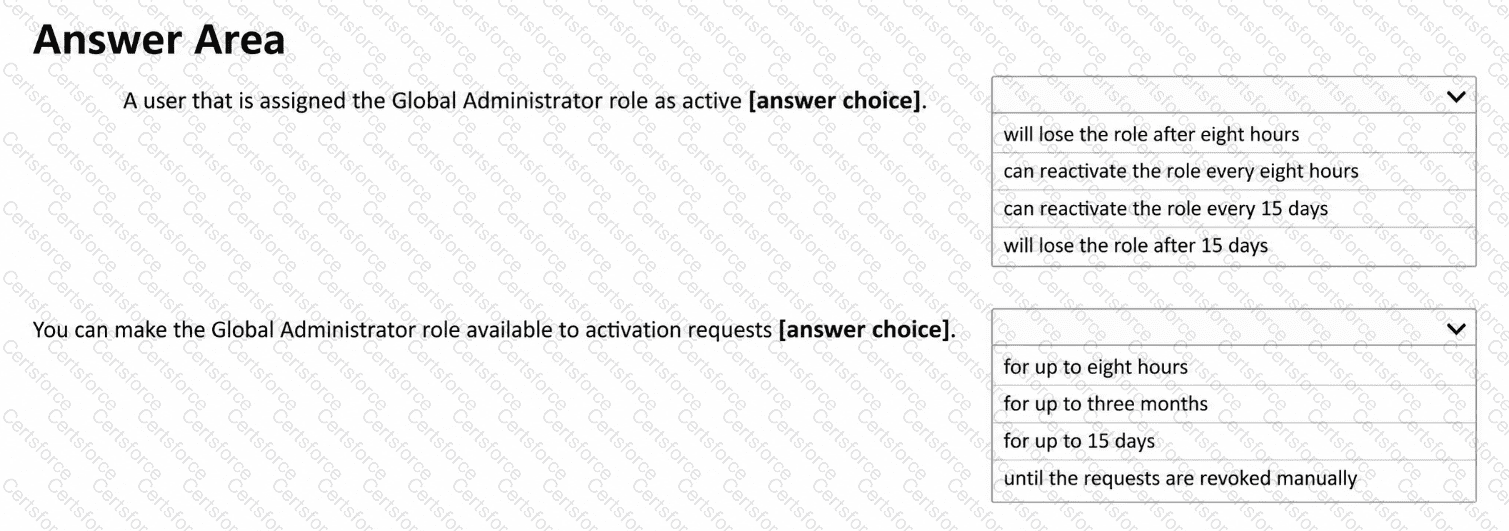
From Microsoft Entra Privileged Identity Management, you configure Role settings for the Global Administrator role as shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.