
Refer to Exhibit.
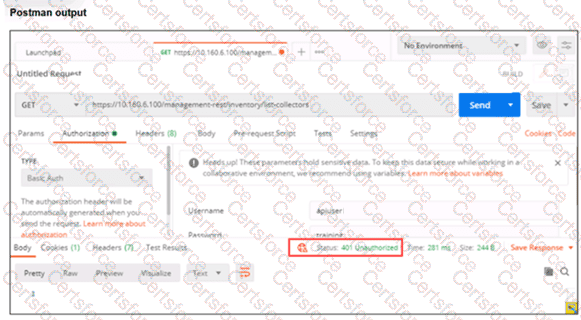
Based on the Postman output shown in the exhibit, why is the user receiving an unauthorized error? (Choose one answer)
A collector attempts to access a known malicious website. FortiEDR is configured for eXtended detection with FortiAnalyzer. What two roles does Fortinet Cloud Services (FCS) perform in this process? (Choose two answers)
Refer to the exhibit.
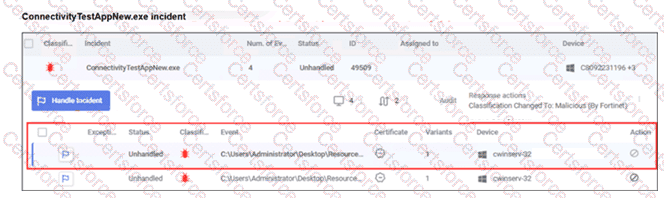
What observation can you make about the ConnectivityTestAppNew.exe incident? (Choose one answer)
You find third-party software on a user’s computer that does not appear in the application list on the communication control console. Which two statements are true about this situation? (Choose two answers)
Which two Python commands are supported when using FortiEDR Connect to directly access a protected device shell? (Choose two answers)
What action does an on-premises reputation server take when it receives a hash request that is not found in its local database? (Choose one answer)
You added three new applications to FortiEDR using only the Path attribute. What are two expected outcomes of this configuration? (Choose two answers)
A playbook is configured with two actions: terminate process and isolate device. The terminate process action fails because the process is protected by Windows. What is the expected behavior for the second action, isolate device? (Choose one answer)
Refer to the Exhibit:
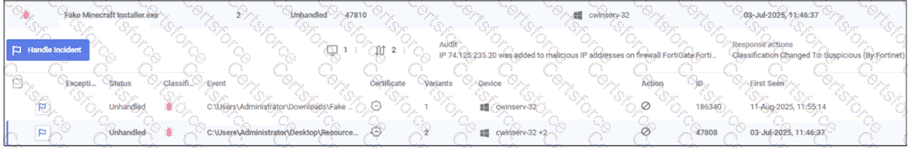
Based on the incident details shown in the exhibit, which two statements about this incident are true? (Choose two answers)
You are asked to configure a query to run every 15 minutes, automatically searching for specific registry modifications across all endpoints. Which FortiEDR feature must you configure? (Choose one answer)
