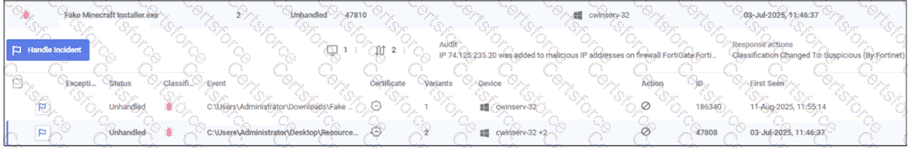
The exhibit shows an audit/response action stating that IP address 74.125.235.20 was added to malicious IP addresses on firewall FortiGate . This matches the FortiEDR playbook action Block address on Firewall . The guide states that this action ensures connections to remote malicious addresses associated with the security event are blocked, and that a firewall connector must already be configured for this action. It also explains that a checkmark in a classification column means communication with the affected destination is automatically blocked when a security event with that classification is triggered.
Option C is the second best answer because FortiEDR events are initially classified by FortiEDR detection logic/Core, and the guide states that classifications are initially determined by the Core but can later be changed automatically by FortiEDR Cloud Service or manually. The exhibit shows “Classification Changed To: Suspicious (By Fortinet)” , but it does not say the event was manually classified by an administrator. So the event classification process is FortiEDR-driven, with later Fortinet/FCS-style automatic classification possible.
Option B is wrong. The exhibit shows one raw-data row with device cwinserv-32 +2 , which indicates more than one affected device/raw item is represented in the aggregation. So it did not occur on only one device.
Option D is wrong because the incident rows clearly show Unhandled . The guide states that security events are initially marked as unread and unhandled, and the unread/unhandled status helps users track whether anyone has read and handled the event.
=========
Contribute your Thoughts:
Chosen Answer:
This is a voting comment (?). You can switch to a simple comment. It is better to Upvote an existing comment if you don't have anything to add.


Submit