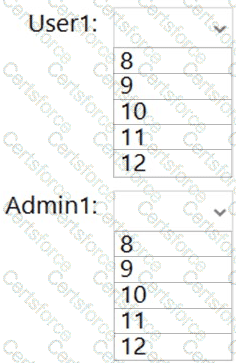
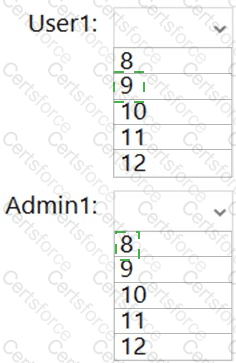
Fine-grained password policies delivered through Password Settings Objects (PSOs) take precedence over the domain-wide Default Domain Policy for any user they apply to. When more than one PSO would apply to the same user only through different group memberships (as opposed to one being linked directly to the user), the PSO with the lowest numeric precedence value wins. User1 is a member of both Group2 (targeted directly by PSO1, precedence 10, minimum password length 9) and Group4 (targeted directly by PSO2, precedence 20, minimum password length 11); since PSO1 ' s precedence value of 10 is lower than PSO2 ' s 20, PSO1 governs, giving User1 an effective minimum password length of 9. Admin1 is a member only of Domain Admins, which is not targeted by either PSO, so no fine-grained password policy applies. Admin1 is also in OU1, which has GPO1 linked to it with a minimum password length of 10, but Account Policy settings such as password policy configured in an OU-linked GPO never affect the effective password policy of domain user accounts -- only a GPO linked at the domain root can supply a fallback domain-wide default, and PSOs otherwise take precedence over that default. With no applicable PSO, Admin1 ' s effective policy falls back to the Default Domain Policy, whose minimum password length in this environment is 8.
Contribute your Thoughts:
Chosen Answer:
This is a voting comment (?). You can switch to a simple comment. It is better to Upvote an existing comment if you don't have anything to add.


Submit