In Huawei’s BGP/MPLS IP VPN forwarding model:
???? Traffic Flow:
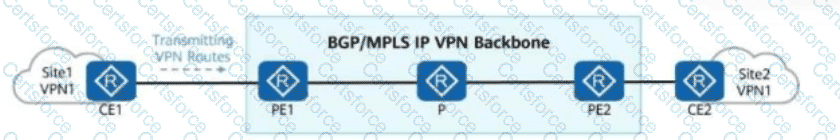
CE1 sends an IPv4 packet (unencrypted, unlabeled) to PE1.
PE1 determines the VPN routing table (VRF) based on the incoming interface.
PE1 performs a lookup in the VPN routing table for the destination.
PE1 finds the VPNv4 route (with BGP label) and also gets the LDP tunnel label for the next-hop PE router.
PE1 pushes two labels onto the packet:
Inner label: VPN label (BGP label for VPN route)
Outer label: LDP label (tunnel label to PE2)
???? Option A: PE1 searches for a VPN label based on the tunnel ID and adds a label header to the packet.
❌ Incorrect – VPN labels are not searched based on tunnel ID.
The VPN label is derived from VPNv4 BGP route, not from tunnel ID.
???? Option B: PE1 checks the forwarding table corresponding to VPN1 and obtains the tunnel ID.
✅ Correct –
PE1 first determines the VRF based on interface binding.
It then uses that to look up the VPNv4 route and retrieves the tunnel information (e.g., next-hop PE).
???? Option C: PE1 uses the LDP label corresponding to the Next_Hop address of a VPNv4 route as the outer label of a labeled packet.
✅ Correct –
The outer label is the LDP label for the LSP to the next-hop PE (e.g., PE2).
???? Option D: PE1 ' s interface that receives the traffic is bound to VPN1.
✅ Correct –
In MPLS VPN, PE routers bind CE-facing interfaces to VRFs (VPN routing tables).
This is how the device knows which VPN instance the traffic belongs to.
✅ Final Answer: B, C, D
Official Huawei Extract:
" In BGP/MPLS IP VPNs, PE devices use interface bindings to associate CE traffic with VRFs. When forwarding packets, PE devices push two labels: a VPN label (from BGP) and a transport label (from LDP) to reach the next-hop PE. "
— [Huawei HCIA-Datacom Certification Guide – MPLS VPN Packet Forwarding Chapter]


Submit