
Black Friday Reward - Upto 75% off - Ends in 0d 00h 00m 00s - Coupon code: CFsave75

HPE Network Security Expert Written Exam HPE7-A10 Question # 9 Topic 1 Discussion

HPE Network Security Expert Written Exam HPE7-A10 Question # 9 Topic 1 Discussion

HPE7-A10 Exam Topic 1 Question 9 Discussion:
Question #: 9
Topic #: 1

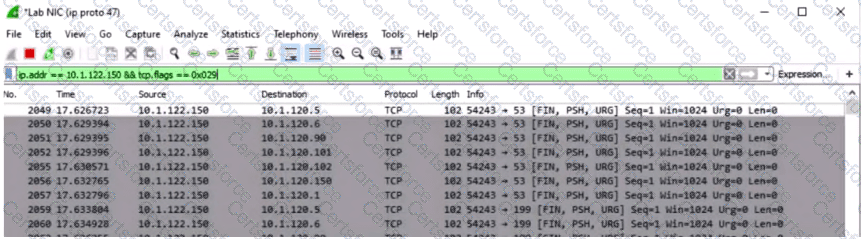
Refer to the exhibit.
HPE7-A10 Question 9

Packet trace display:

    Source: 10.1.122.150 - > Destination: 10.1.120.5 TCP 54243 - > 53 [FIN, PSH, URG] Seq=1 Win=1024 Urg=0 Len=0

    Source: 10.1.122.150 - > Destination: 10.1.120.6 TCP 54243 - > 53 [FIN, PSH, URG] Seq=1 Win=1024 Urg=0 Len=0

    Source: 10.1.122.150 - > Destination: 10.1.120.90 TCP 54243 - > 53 [FIN, PSH, URG] Seq=1 Win=1024 Urg=0 Len=0

    Source: 10.1.122.150 - > Destination: 10.1.120.101 TCP 54243 - > 53 [FIN, PSH, URG] Seq=1 Win= 1024 Urg=0 Len=0

    Source: 10.1.122.150 - > Destination: 10.1.120.5 TCP 54243 - > 199 [FIN, PSH, URG] Seq=1 Win=1024 Urg=0 Len=0

What does this indicate?


A.

Someone is attempting to determine which ports are open on devices in subnet 10.1.120.0/24.


B.

Someone is attempting to launch a DoS attack against clients in the 10.1.120.0/24 subnet.


C.

Port forwarding policies are misconfigured on core routers or routing switches.


D.

A hacker is hijacking the connections between clients in 10.1.120.0/24 and the true owner of the 10.1.122.150 IP address.


Get Premium HPE7-A10 Questions

Contribute your Thoughts:


Chosen Answer:
This is a voting comment (?). It is better to Upvote an existing comment if you don't have anything to add.