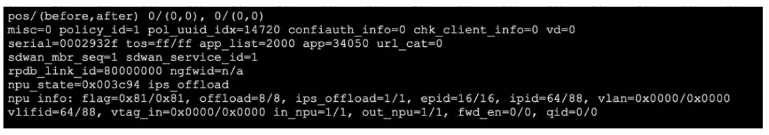
In the provided session table output, the following details justify the answers:
Policy ID Match: The line policy_id=1 directly confirms that this session was matched by Firewall Policy ID 1. According to Fortinet’s session table documentation, the policy_id field always references the policy that allowed this session, so this is a clear indicator.
Session Offloading: The presence of the strings npu_state, ips_offload, and notably the NPU info section such as offload=8/8, ips_offload=1/1 shows that this session has been offloaded to the Network Processor Unit (NPU). Fortinet technical documentation states that " offload " values greater than zero in both directions (and an NPU info section) affirm that NPU hardware processing (fast path) is handling this traffic, thus the session is not being handled in software only.
Other options:
VLAN Tagging (vlan=0x0000/0x0000): This means no VLAN tag is assigned to this session.
NP7: The actual NPU model handling the session isn’t exposed in this snippet–the offload parameters shown are generic and not specific to NP7 hardware, so it cannot be concluded from the session data.
[References:, , Fortinet Technical Tip: FortiGate Session Table and NPU Offloading, , FortiOS Diagnostics Guide: Policy ID, Offload, and VLAN Session Table Fields, , , ]


Submit