
Weekend Sale Special Limited Time 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: CFsave75

Fortinet NSE 5 - FortiWeb 8.0 Administrator NSE5_FWB_AD-8.0 Question # 9 Topic 1 Discussion

Fortinet NSE 5 - FortiWeb 8.0 Administrator NSE5_FWB_AD-8.0 Question # 9 Topic 1 Discussion

NSE5_FWB_AD-8.0 Exam Topic 1 Question 9 Discussion:
Question #: 9
Topic #: 1

Refer to the exhibit.
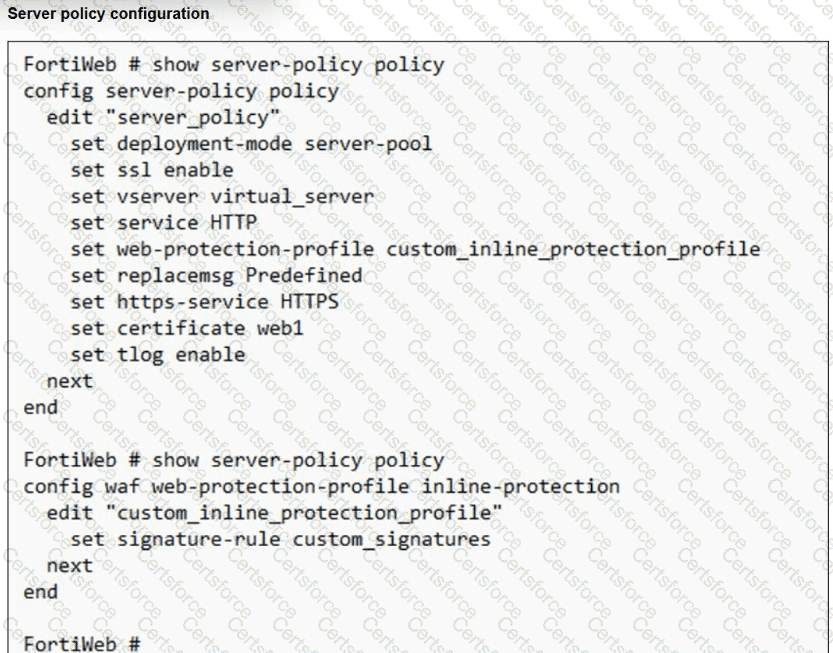
NSE5_FWB_AD-8.0 Question 9

You have deployed FortiWeb behind a FortiGate that is configured as a reverse proxy and inserts the X-Forwarded-For HTTP header when forwarding HTTP and HTTPS traffic.

FortiWeb is using a custom inline protection profile, and logging is enabled, as shown in the exhibit.

You notice that FortiWeb is blocking legitimate users, and all requests in the attack logs appear to come from the FortiGate IP address, not the original client IP address.

Which action should you take to fix this issue?


A.

Replace the current deployment mode with a one-arm proxy to expose source IP addresses.


B.

Disable IP-based detection features on FortiWeb to avoid IP-related blocking.


C.

Recreate the server policy using the predefined profile instead of a custom one.


D.

Modify the protection profile to use the X-Forwarded-For header for client IP address detection.


Get Premium NSE5_FWB_AD-8.0 Questions

Contribute your Thoughts:


Chosen Answer:
This is a voting comment (?). It is better to Upvote an existing comment if you don't have anything to add.