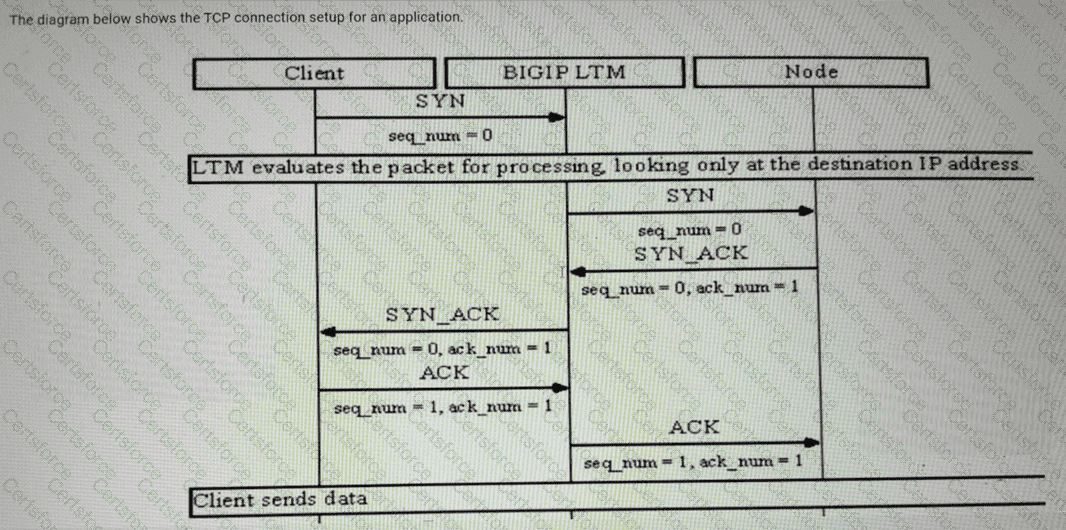
The diagram illustrates a specific TCP handshake sequence where the BIG-IP system acts as a transparent forwarder rather than a full proxy. The key indicators that identify this as a Forwarding (IP) virtual server are as follows:
Initial Packet Processing : The diagram explicitly states that the LTM evaluates the packet looking only at the destination IP address . This is the fundamental characteristic of a Forwarding IP virtual server, which uses the system ' s routing table to make forwarding decisions instead of load balancing to a pool of members.
Handshake Sequence : Unlike a Standard virtual server, which completes the three-way handshake with the client (SYN, SYN-ACK, ACK) before initiating a separate connection to the server, the Forwarding IP virtual server passes the client ' s original SYN packet directly to the destination node.
Response Timing : The BIG-IP system waits for the SYN-ACK from the destination node before it sends a SYN-ACK back to the client. It essentially " passes through " the handshake signals while still maintaining a state entry in the connection table to track the flow.
Packet-by-Packet Logic : While it tracks the state, it does not perform address translation (unless SNAT is specifically configured) or deep packet inspection like a full proxy would.
Why other options are incorrect:
Standard virtual server : A Standard virtual server is a " full proxy. " It would finish the handshake with the client first and only then open a second, independent TCP connection to the backend server.
Stateless virtual server : A stateless virtual server does not track connections in the connection table. The diagram shows the system meticulously passing sequence numbers ($seq\_num$) and acknowledgment numbers ($ack\_num$) between the two sides, which requires stateful tracking of the TCP flow.
Contribute your Thoughts:
Chosen Answer:
This is a voting comment (?). You can switch to a simple comment. It is better to Upvote an existing comment if you don't have anything to add.


Submit