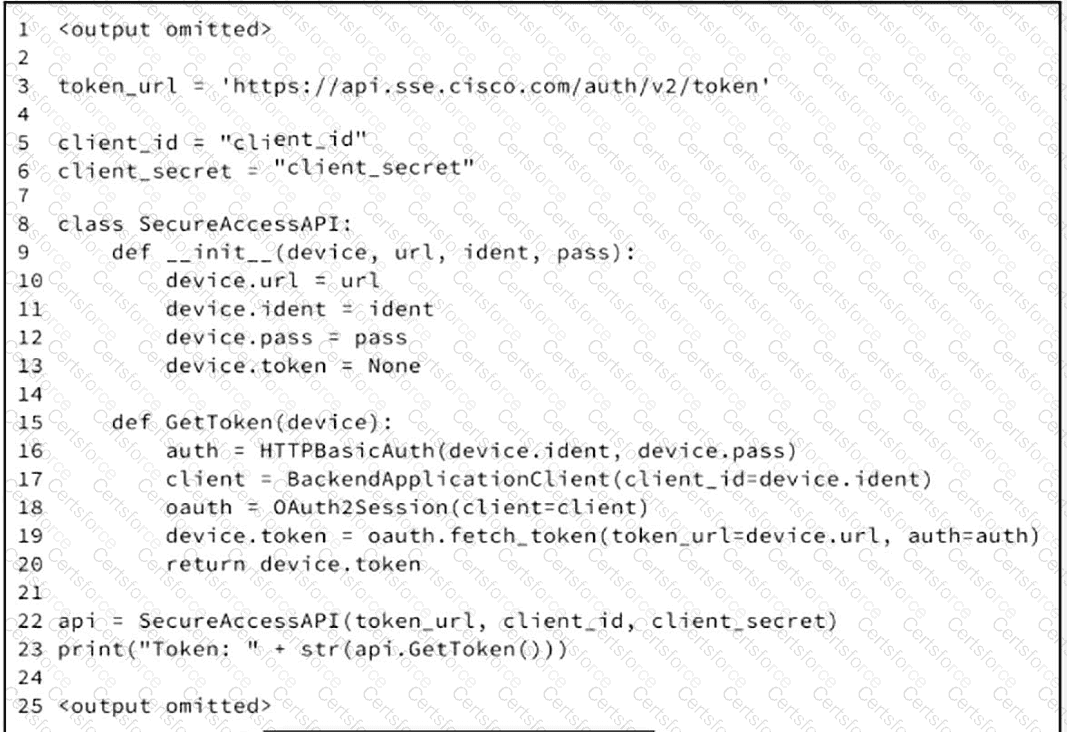
The script implements the OAuth 2.0 client-credentials flow. HTTPBasicAuth supplies the client ID and client secret to the Secure Access token endpoint, while BackendApplicationClient and OAuth2Session construct the machine-to-machine authorization request. The call to fetch_token() posts to https://api.sse.cisco.com/auth/v2/token and returns the token response, which contains an OAuth access token and related metadata. GetToken() returns that response, and the final print() statement displays it after the Token: prefix. Cisco’s API documentation identifies this endpoint as the Secure Access Token Authorization endpoint and states that it generates an API access token using the client-credentials flow. The URL and client secret are inputs to the request, not the resulting authorization credential, and “endpoint token” is not the documented output. Therefore, the expected output is an access token. Cisco Secure Access API authentication guide
Contribute your Thoughts:
Chosen Answer:
This is a voting comment (?). You can switch to a simple comment. It is better to Upvote an existing comment if you don't have anything to add.


Submit