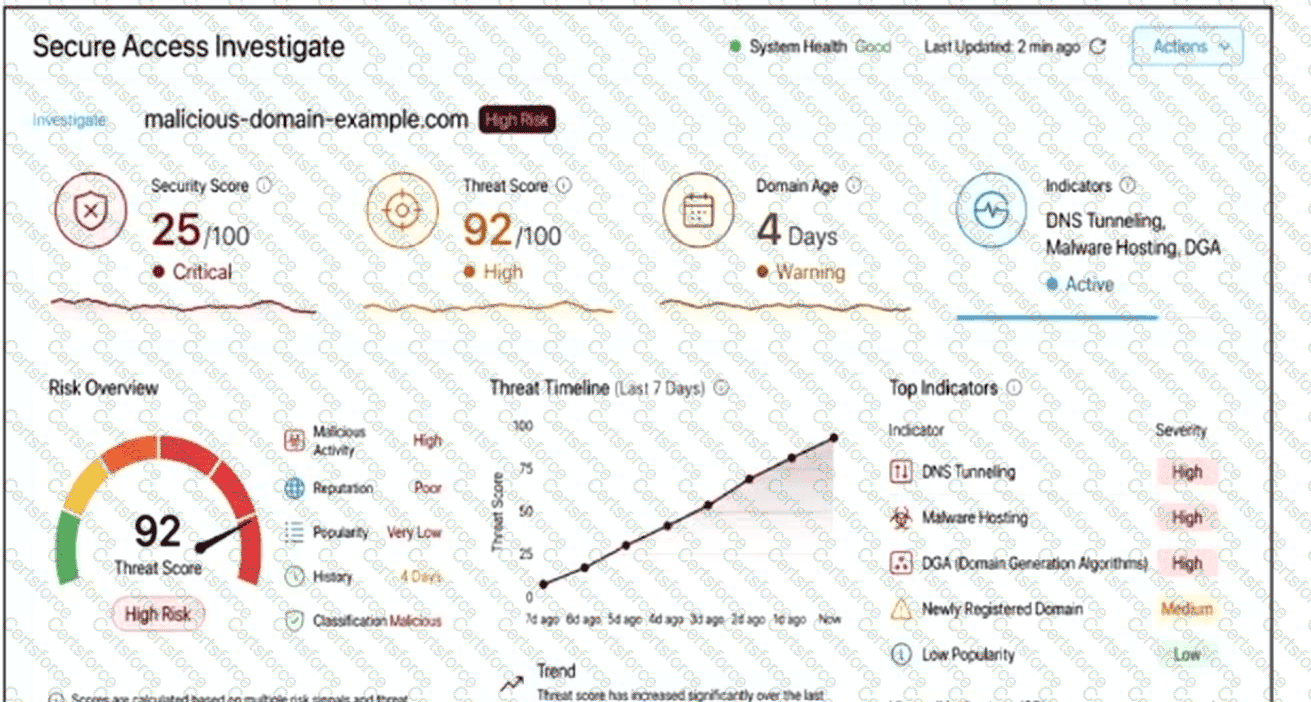
The exhibit presents several mutually reinforcing indicators: a Threat Score of 92/100, a High Risk classification, poor reputation, malicious classification, DNS tunneling, malware hosting, and domain-generation-algorithm activity. Option D is therefore the supported conclusion. The domain’s age of four days is a warning signal, but the display does not say that age alone caused the block, so option A overstates one factor. Option B conflicts with the four-day age and incorrectly describes the domain as legacy. Option C reverses the meaning of the Security Score display: 25/100 is explicitly labeled Critical, not safe. Cisco states that Investigate risk scoring combines domain-name characteristics and query patterns, and that analysts should use the contributing security features for triage. Cisco Secure Access Investigate API supports this evidence-based interpretation.
================
Contribute your Thoughts:
Chosen Answer:
This is a voting comment (?). You can switch to a simple comment. It is better to Upvote an existing comment if you don't have anything to add.


Submit