
Halloween Sale Special Limited Time 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: CFsave75

Cisco Securing Networks with Cisco Firepower (300-710 SNCF) v1.2 300-710 Question # 86 Topic 9 Discussion

Cisco Securing Networks with Cisco Firepower (300-710 SNCF) v1.2 300-710 Question # 86 Topic 9 Discussion

300-710 Exam Topic 9 Question 86 Discussion:
Question #: 86
Topic #: 9

300-710 Question 86

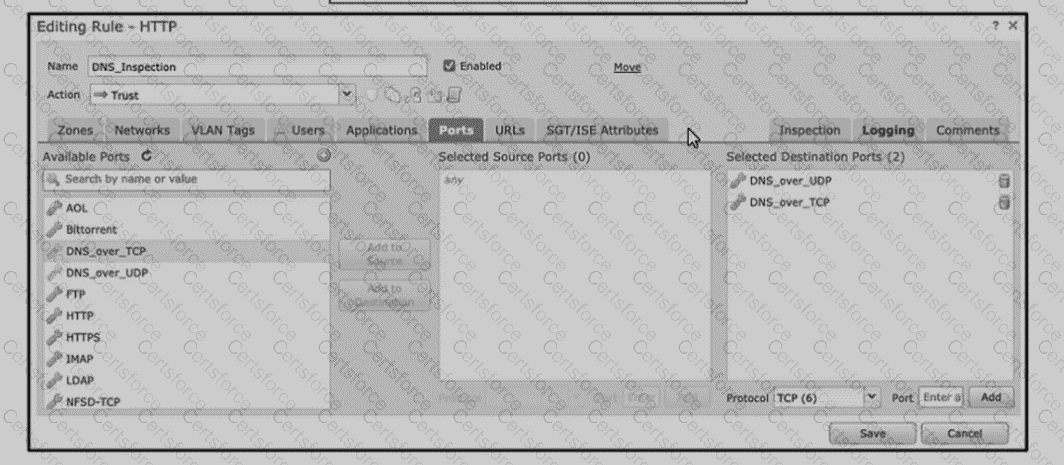
Refer to the exhibit An engineer is modifying an access control pokey to add a rule to inspect all DNS traffic that passes through the firewall After making the change and deploying thepokey they see that DNS traffic is not bang inspected by the Snort engine What is the problem?


A.

The rule must specify the security zone that originates the traffic


B.

The rule must define the source network for inspection as well as the port


C.

The action of the rule is set to trust instead of allow.


D.

The rule is configured with the wrong setting for the source port


Get Premium 300-710 Questions

Contribute your Thoughts:


Chosen Answer:
This is a voting comment (?). It is better to Upvote an existing comment if you don't have anything to add.