Employees in the accounting department of a company receive an email about the latest federal accounting regulations. The email contains a hyperlink to register for a webinar providing updates on financial transaction security. The webinar claims to be hosted by a government agency.
As a security officer, you notice that the hyperlink points to an unknown third party.
Which type of cybersecurity threat should you investigate?
How do threat actors launch ransomware attacks on organizations?
What should you create to prevent spoofing of the internal network?
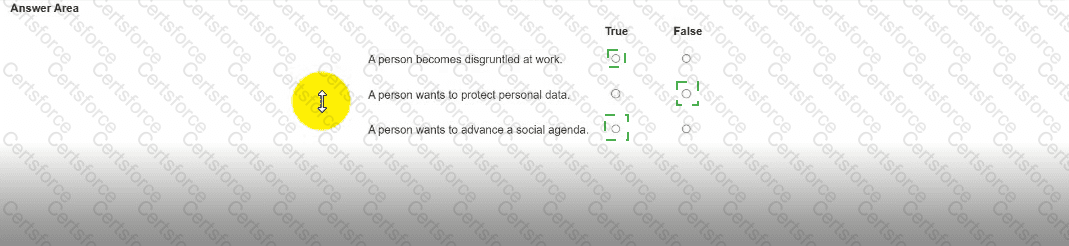
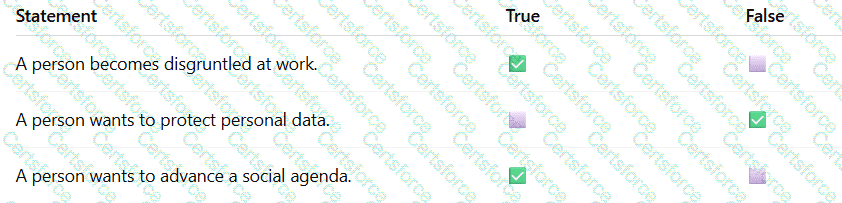
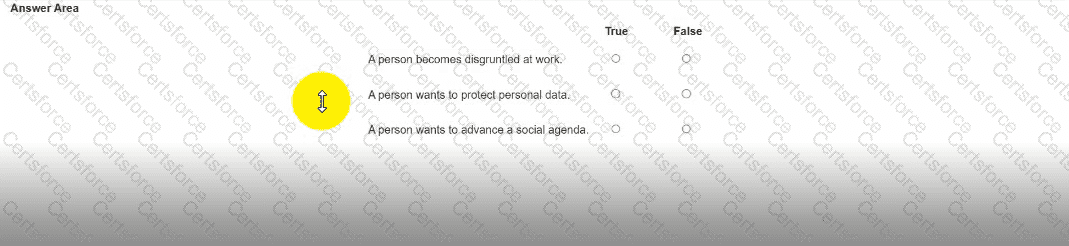
For each statement, select True if it is a common motivation to commit cyber attacks or False if it is not.
Note: You will receive partial credit for each correct selection.
Which step should be performed immediately after identifying a critical vulnerability affecting internet-facing systems?
Why is it necessary to update firmware to the latest version?
You need a software solution that performs the following tasks:
Compiles network data
Logs information from many sources
Provides orchestration in the form of case management
Automates incident response workflows
What product should you use?
Which activity performed by an adversary is an example of an exploit attempting to obtain user credentials?
How does sandboxing help with the analysis of malware?
Your supervisor suspects that someone is attempting to gain access to a Windows computer by guessing user account IDs and passwords. The supervisor asks you to use the Windows Event Viewer security logs to verify the attempts.
Which two audit policy events provide information to determine whether someone is using invalid credentials to attempt to log in to the computer? (Choose 2.)
Note: You will receive partial credit for each correct selection.