
You have an Azure subscription that contains a Microsoft Sentinel workspace named MWS1 and an Azure Data Lake Storage account named lake1. Firewall log data is ingested into MWS1.
You plan to export historical firewall log data from MWS1 to lake1.
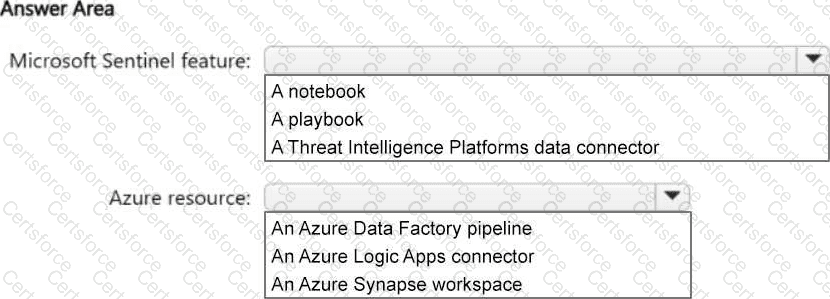
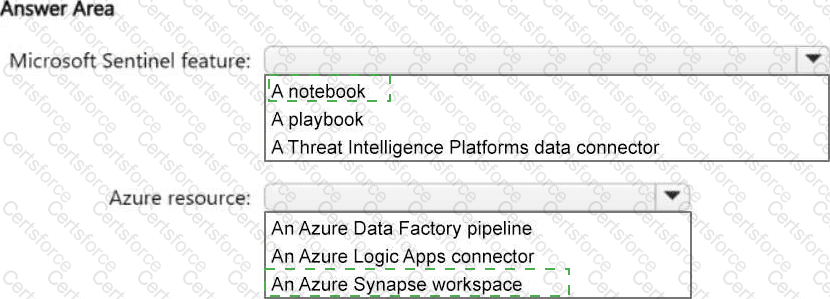
You need to ensure that security analysts can perform threat hunting from MWS1. The solution must ensure that the firewall logs stored in lake1 can be included in threat hunting queries.
What should you configure? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.

Submit