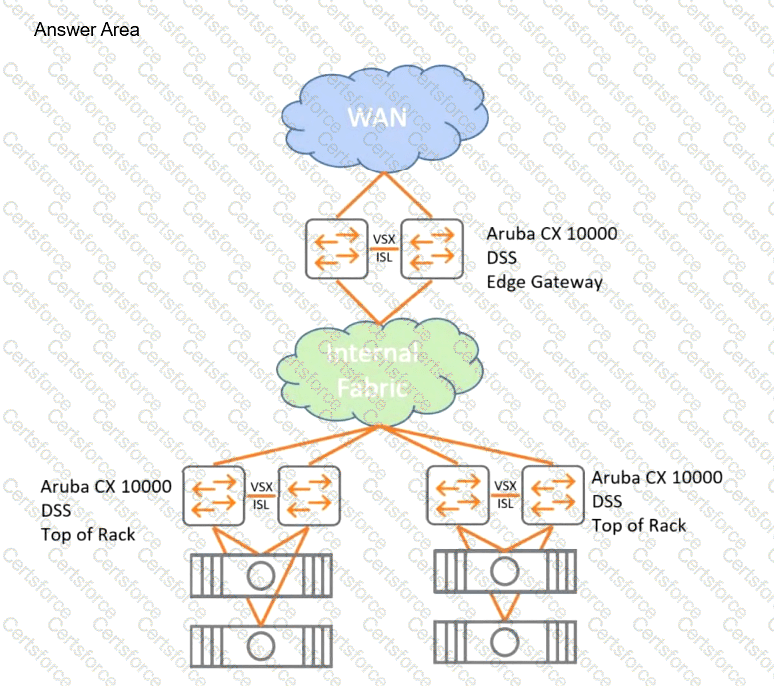
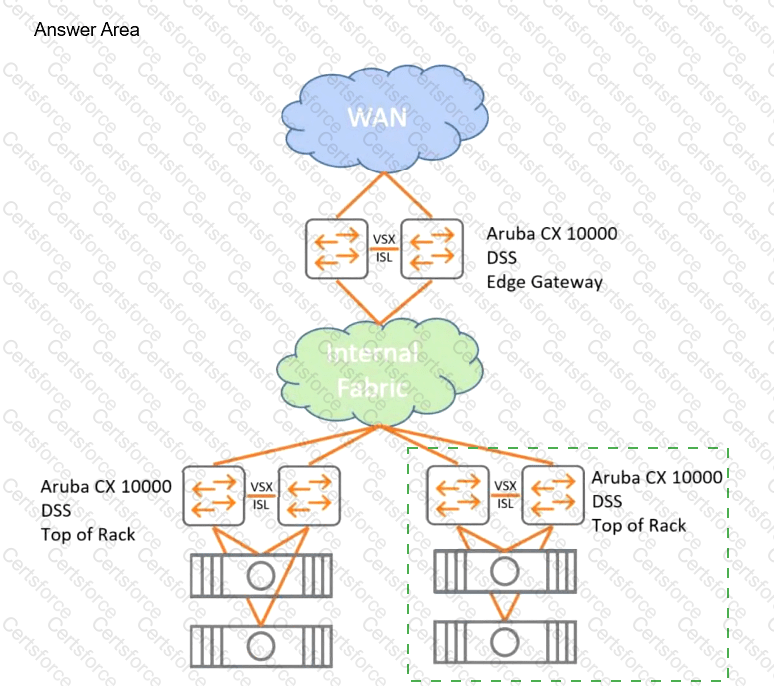
Aruba CX 10000 DSS Top of Rack switches (Targeting the Top-of-Rack layer directly adjacent to the server racks)
The fundamental architectural objective of deploying Distributed Services Architecture with the HPE Aruba CX 10000 Series is to implement zero-trust microsegmentation directly at the workload access edge.
In traditional perimeter-focused networks, east-west server-to-server traffic within the data center must either remain uninspected or be hairpinned up through centralized edge firewalls, creating massive bandwidth bottlenecks, latency penalties, and routing complexity. By implementing network-segmentation policies on the Aruba CX 10000 DSS switches positioned at the Top of Rack (ToR) layer, stateful firewall inspection and microsegmentation rules are applied on the very first physical switch hop.
The integrated AMD Pensando Elba DPU enforces stateful Layer 4 through Layer 7 access policies between workloads directly at the rack access layer, including inspecting traffic between virtual machines or bare-metal servers residing within the exact same Layer 2 VLAN or subnet. Placing the primary segmentation policies at the ToR switches contains lateral threat propagation instantly, enforces east-west zero-trust security boundaries locally, and offloads the Edge Gateway switches, which remain dedicated to north-south WAN perimeter policy enforcement.
Reference Topics: HPE Aruba CX 10000 Architecture – Distributed Services Top-of-Rack vs. Border Edge Gateway Placement; Microsegmentation Implementation.


Submit